 Do Son
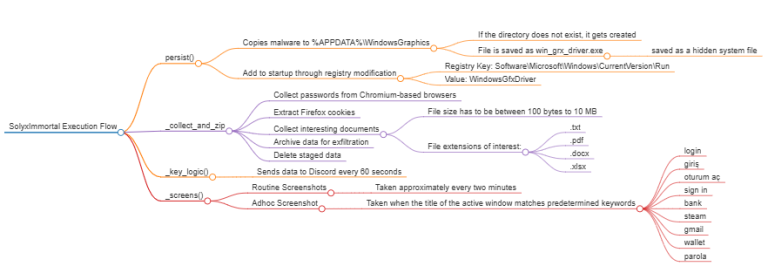
The SolyxImmortal info stealer targets user data. Learn how this Python malware steals passwords and abuses Discord webhooks to exfiltrate files.
Python Malware
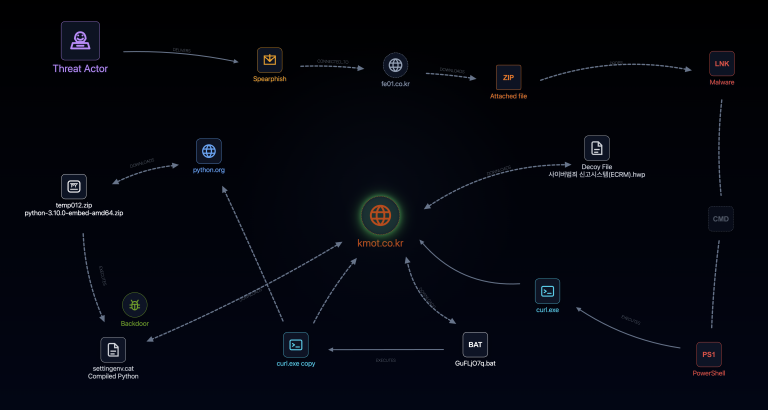
Genians unmasks an APT37 campaign using environment variable tricks and compiled Python malware to bypass EDR. Protect your network from these stealthy lures.
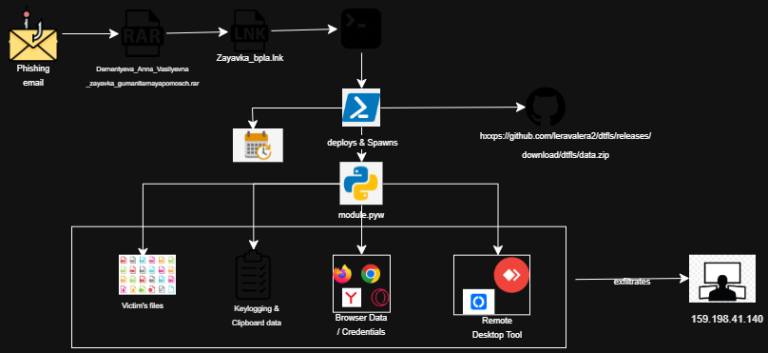
CRIL exposes a cyberespionage campaign using fake humanitarian aid forms to deploy fileless Python malware via GitHub for full-spectrum surveillance.
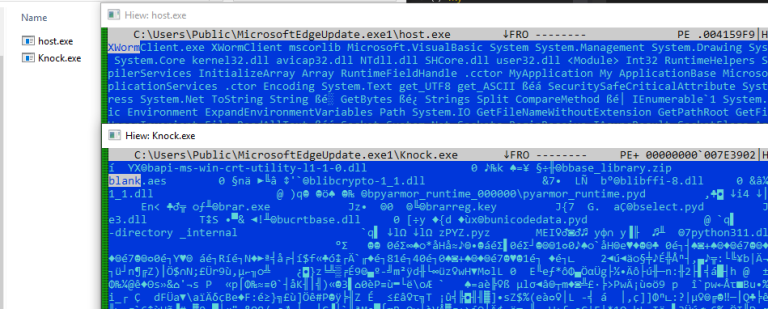
Splunk unmasks BlankGrabber: a modular Python info stealer using Discord and GitHub to swipe credentials and Discord tokens. Learn how to stay protected.
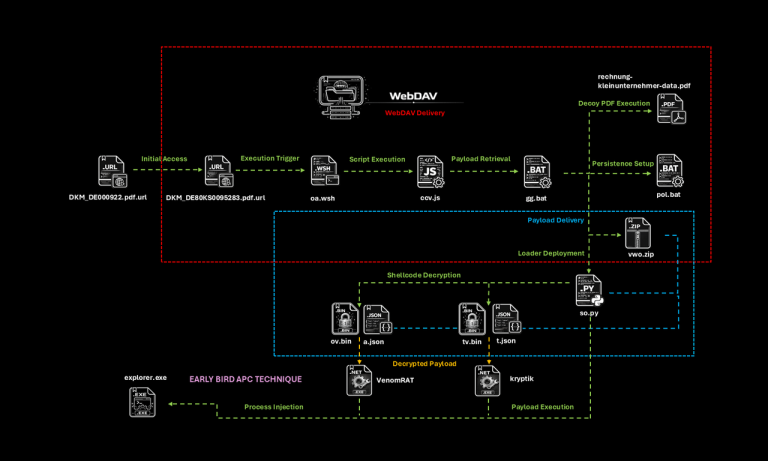
G DATA analysts chat with a malware author via Notepad while analyzing "Kiss Loader," a new threat using Early Bird APC injection and VenomRAT. Read more!
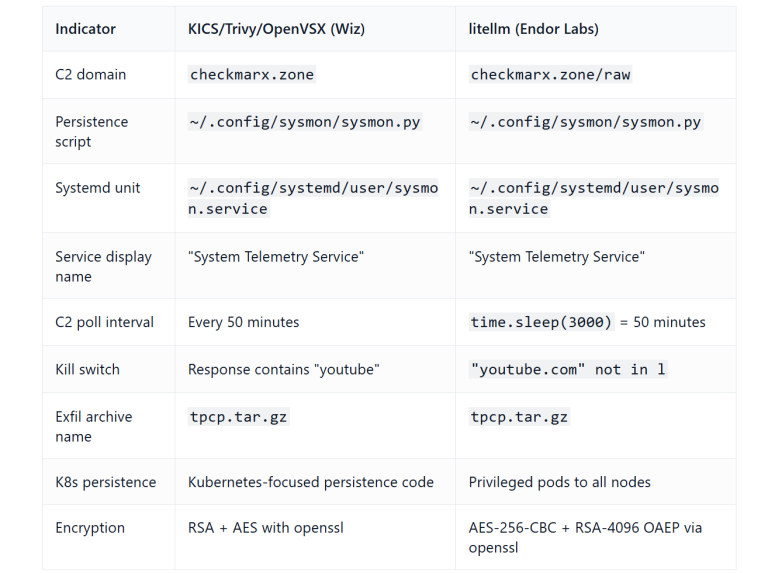
95M-download LiteLLM library hijacked on PyPI. TeamPCP's backdoor steals cloud tokens and hijacks Kubernetes clusters. Check for version 1.82.8 now.
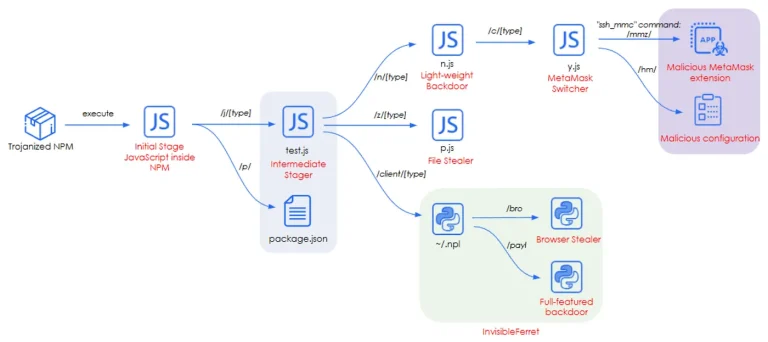
North Korean hackers target IT pros with "Contagious Interview" malware. Fake job offers install trojanized MetaMask extensions to steal crypto.

Microsoft warns: Infostealers now target macOS & use WhatsApp worms. "Eternidade" & "Crystal PDF" steal credentials via cross-platform attacks.
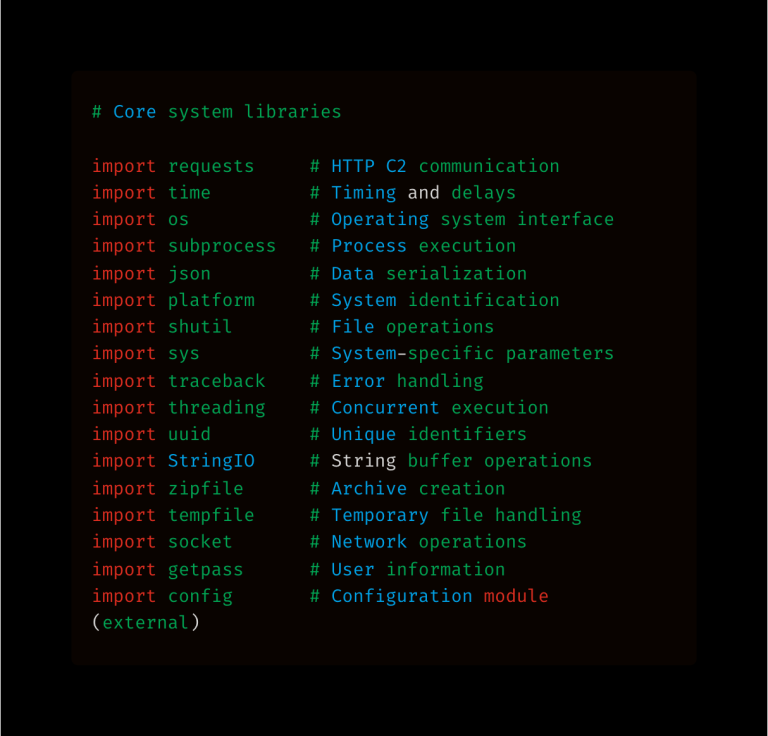
K7 Labs uncovers a stealthy Python-based RAT disguised as an ELF binary. Features adaptive beaconing and anti-forensics to stay hidden. Read the analysis.

Malicious npm package "ansi-universal-ui" drops "G_Wagon" infostealer to steal cloud keys and wallets. Check for .gwagon_status and rotate creds now.

CYFIRMA reveals SolyxImmortal, a Python info-stealer using Discord webhooks for C2. It logs keys and steals files while evading detection.

New macOS malware "MonetaStealer" disguises itself as a Windows .exe to steal crypto & Keychain data. It currently has zero VirusTotal detection.

CloudSEK exposes "RedLineCyber," an impostor hijacking crypto clipboards on Discord. This stealthy malware drains wallets without a C2 server.

Unit 42 unmasks VVS Stealer, a Python-based threat using Pyarmor obfuscation to bypass AV, hijack Discord sessions, and steal browser credentials.

K7 Labs exposed a Python malware using multi-layer encoding (Base64/BZ2/Zlib) and a PNG-disguised RAR archive. The payload executes in memory and achieves stealth by injecting into cvtres.exe.