 Do Son
Discover how CVE-2026-48207, a critical PyFory deserialization policy bypass flaw, lets attackers execute remote code, and learn how to patch it now.
Python Security

OceanLotus targets Python developers worldwide via PyPI supply chain attacks. New ZiChatBot malware hijacks Zulip APIs for invisible C2 traffic. Patch now!
Langflow patches a critical 9.6 CVSS path traversal vulnerability (CVE-2026-42048). Learn how an unsafe bulk delete function put entire filesystems at risk.
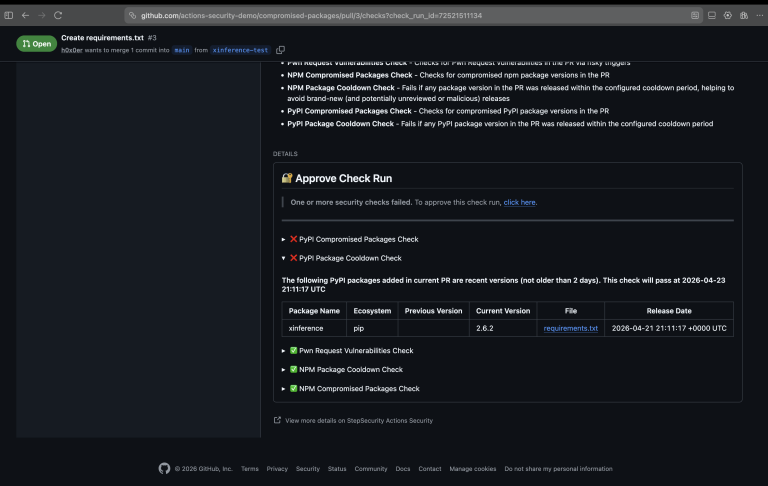
Critical supply chain attack hits Xinference (v2.6.0-2.6.2). TeamPCP’s malware siphons cloud credentials and MLOps secrets. Audit your MLOps pipeline today.
CERT/CC warns of critical flaws in CrewAI. Insecure fallbacks and prompt injection enable RCE and SSRF. No full patch yet—learn how to secure your agents.
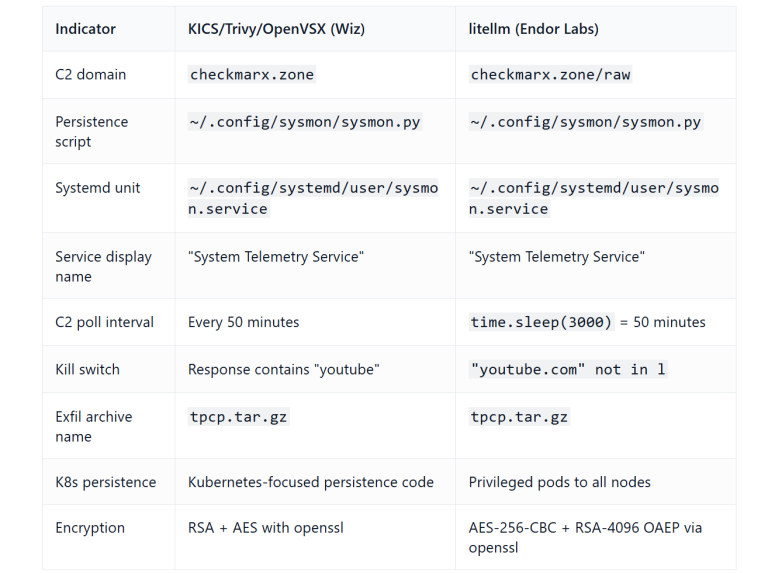
95M-download LiteLLM library hijacked on PyPI. TeamPCP's backdoor steals cloud tokens and hijacks Kubernetes clusters. Check for version 1.82.8 now.

Three critical flaws in Authlib (including CVSS 9.1 CVE-2026-27962) allow JWT forgery and padding oracle attacks. Update to version 1.6.9 immediately.

Critical SQL injection flaw (CVE-2026-26198) in ormar Python ORM allows unauthenticated attackers to leak entire databases. Update to version 0.23.0 immediately!

Splunk Enterprise Windows flaws (CVSS 7.7) CVE-2026-20143 & CVE-2026-20140 allow system takeover via DLL and Python search path hijacking. Patch immediately.

Critical Unstructured library flaw CVE-2025-64712 (CVSS 9.8) allows RCE via malicious .msg files. 4M+ downloads affected. Update to v0.18.18 now.

PyTorch patches CVE-2026-24747 (CVSS 8.8). The "weights_only" safety flag failed, allowing RCE via malicious models. Update to v2.10.0 now.

CVE-2026-0994 (CVSS 8.2) in Google Protobuf Python allows DoS via nested "Any" messages. Recursion limit bypass causes crashes. Update now.

Abandoned Python PLY library contains a critical RCE flaw (CVE-2025-56005) via an undocumented "picklefile" parameter. No patch is expected.

Malicious PyPI package "sympy-dev" impersonates SymPy to install XMRig miners via fileless execution. Check your dependencies immediately.

CVE-2025-14026: Attackers can reconstruct a crippled Python runtime in Forcepoint DLP to execute arbitrary code. Update now to remove the vulnerability.

CVE-2025-68668: A critical n8n flaw lets attackers escape the Python sandbox for full RCE. Learn how this bridge failure leads to total system compromise.

LangChain patches a critical 9.3 CVSS flaw (CVE-2025-68664) where unescaped "lc" keys allow attackers to steal API secrets via prompt injection.