
 Do Son
ViperSoftX, a stealthy malware, is actively spreading via fake software to steal cryptocurrency and enable remote control, affecting users globally.
Quasar RAT

ViperSoftX malware is being used by Arabic-speaking attackers to target South Korea, according to ASEC. This malware uses PowerShell and spreads through torrents, delivering PureCrypter and Quasar RAT

Stay informed about the latest cyber threat: Mauri ransomware exploiting a critical vulnerability (CVE-2023-46604) in Apache ActiveMQ.
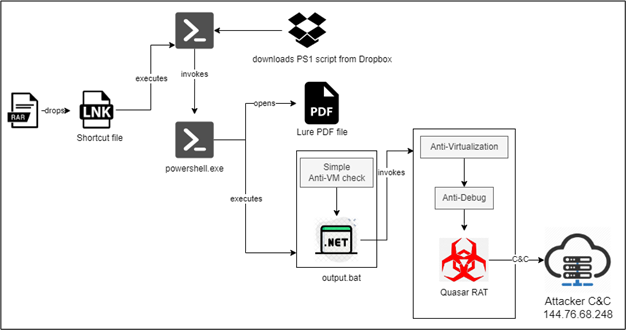
Discover the tactics used by a Vietnamese threat actor to target Meta Ads specialists with malware like Ducktail and Quasar RAT.

This novel use of Tesseract is part of a broader strategy by ViperSoftX to install additional malware strains, including Quasar RAT

The open-source RAT, Quasar RAT, employs the DLL Sideloading technique to discreetly extract data from infected Windows-based devices