 Do Son
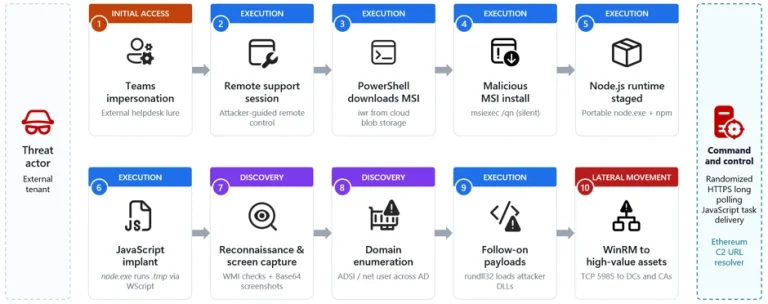
Microsoft Teams IT support impersonation lets attackers plant a Node.js implant and pivot to domain controllers over WinRM. See how to defend.
Quick Assist

A new GoGRPC backdoor spreads through Microsoft Teams vishing and Quick Assist. Zscaler links the campaign to a likely ransomware access broker.
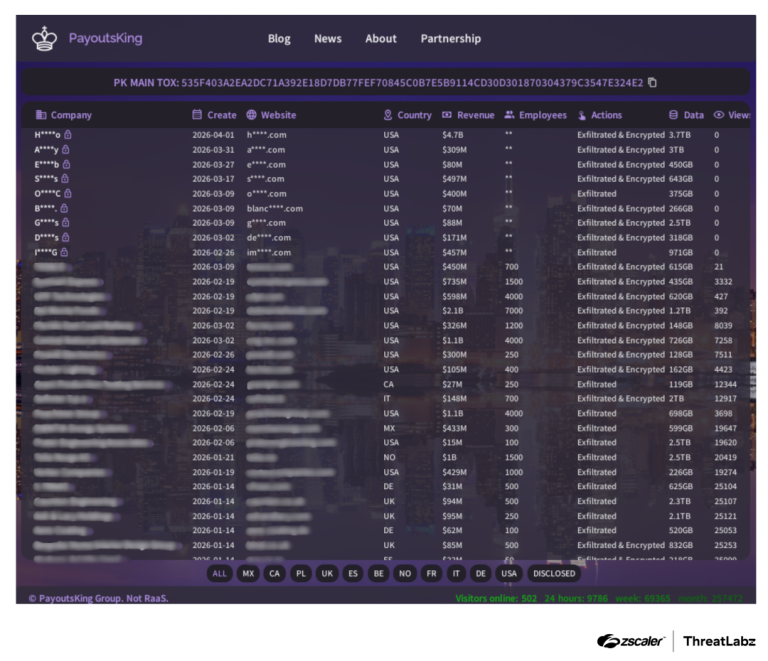
Payouts King, the successor to BlackBasta, uses vishing and direct syscalls to bypass EDR and strike global targets. Learn how to defend your enterprise.

Microsoft warns of a Teams campaign using fake IT support to hijack workstations via Quick Assist, move laterally with WinRM, and steal data using Rclone.

Rapid7 reveals BlackSuit ransomware affiliates are adopting Black Basta tactics, using email bombing, fake Quick Assist scams, and evolving Java RATs.

Uncover the details of the VEILDrive threat campaign leveraging Microsoft services for C2. Learn how the attackers exploited trusted infrastructure to evade detection.

Microsoft Threat Intelligence has uncovered a sophisticated ransomware campaign orchestrated by the cybercriminal group Storm-1811

Forensic investigations by Rapid7 have linked these activities to the Black Basta ransomware group, known for its disruptive cyber attacks