 Do Son
Proofpoint found the PackClient RAT sold on Telegram and used by Chinese-speaking TA4922 malware operators in tax-themed phishing attacks.
rat
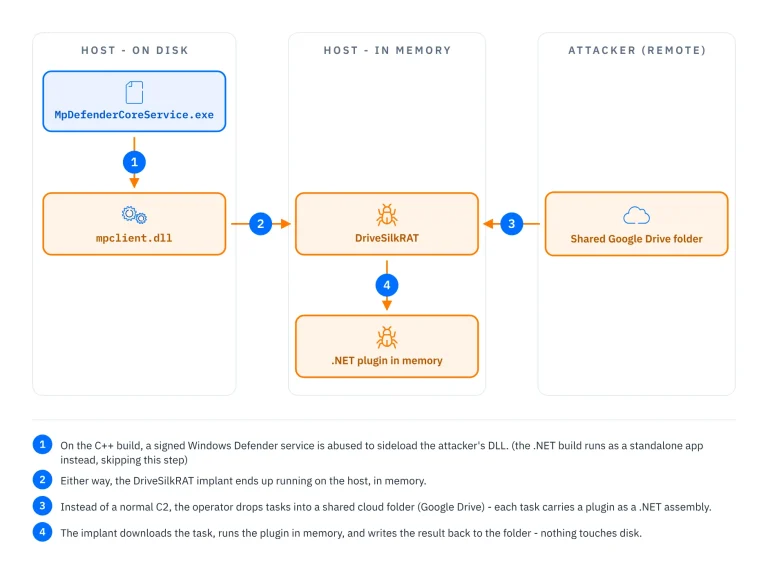
SilkParasite APT ran China-nexus cyberespionage across Central Asia, using 7 custom RATs, DLL sideloading, and AI-assisted malware.

Zscaler ThreatLabz analysts discovered the Abyssos modular RAT. This Abyssos RAT gives attackers total remote control, stealing data and credentials.

A fake Xeno cheat spreads Xeno Roblox malware, a Java stealer that grabs accounts and crypto wallets and spies via webcam. Learn how to stay safe.

North Korea's ClickFake Interview campaign targets crypto pros with fake skill tests, dropping the PylangGhost RAT on Windows and GolangGhost on macOS.

LabubaRAT is a Rust-based remote access tool disguised as NVIDIA software. It supports HTTPS, WebView2, and DNS tunneling for command and control.
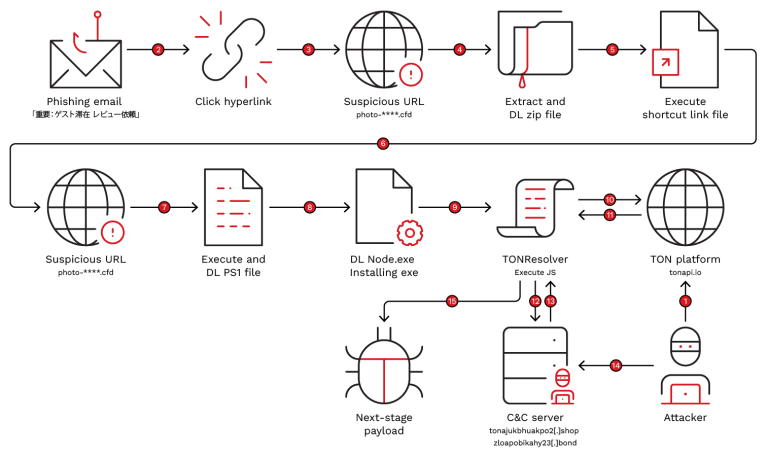
Trend Micro found TONResolver malware hitting Booking.com hotel partners in Japan. It hides its C2 in a TON blockchain smart contract. Details inside.
SHEETCREEP malware is a C# Google Sheets RAT tied to APT36. It hides command-and-control inside Google Sheets to evade network detection.

FortiGuard Labs uncovered AsyncRAT AI lures using fake AI guides and an AutoHotkey loader to inject a stealthy .NET RAT into memory.
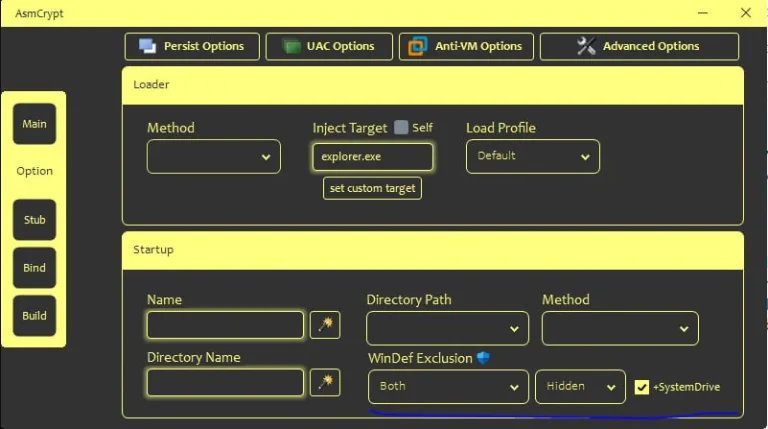
SilabRAT malware, aka SnappyClient, is a $5K/month MaaS RAT flagged as HijackLoader. It uses HVNC and cracks crypto wallets, per Group-IB.

Point Wild exposes a sophisticated PyInstaller loader using in-memory AMSI patching and SHA-512 decryption to drop XWorm V7.4. Patch now!
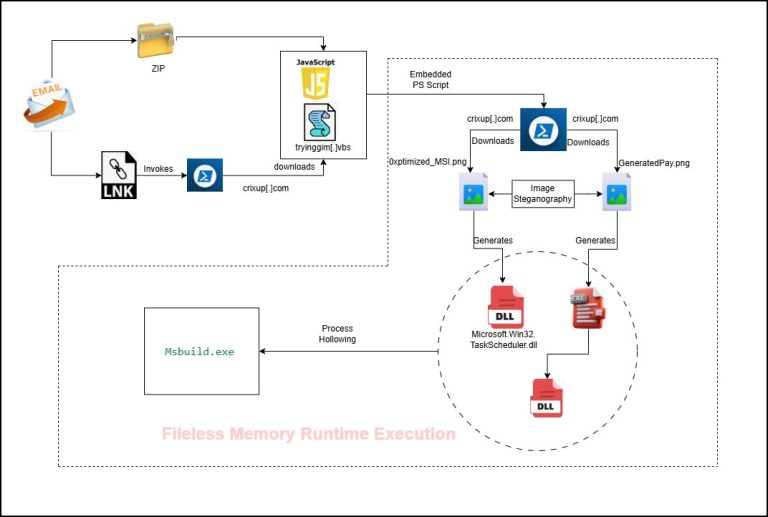
Trellix uncovers PureRAT, a modular Trojan hiding malware in PNG images. Learn how it uses steganography and fileless delivery to bypass Windows security.
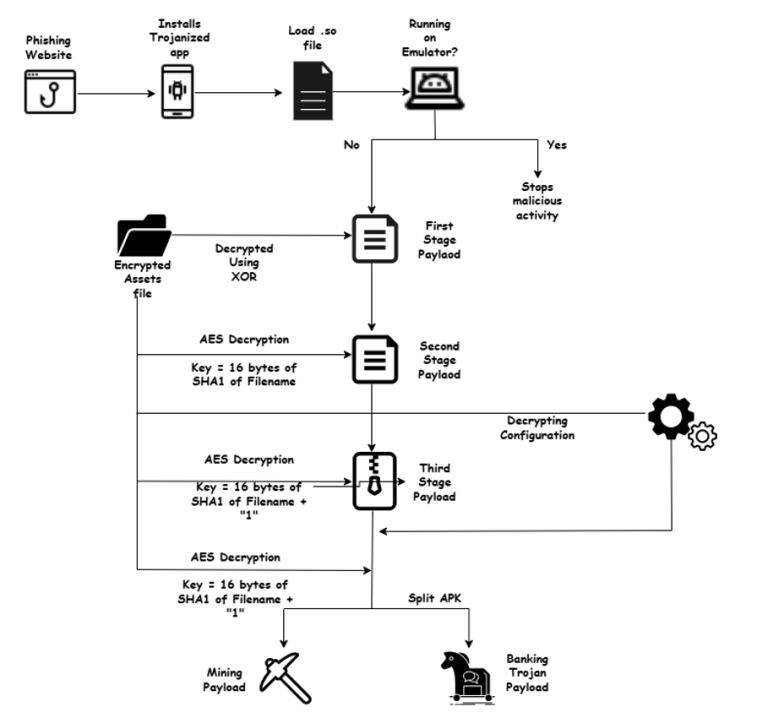
Cyble reveals MiningDropper, a modular Android threat delivering RATs and infostealers via multi-stage payloads. Protect your mobile devices now.
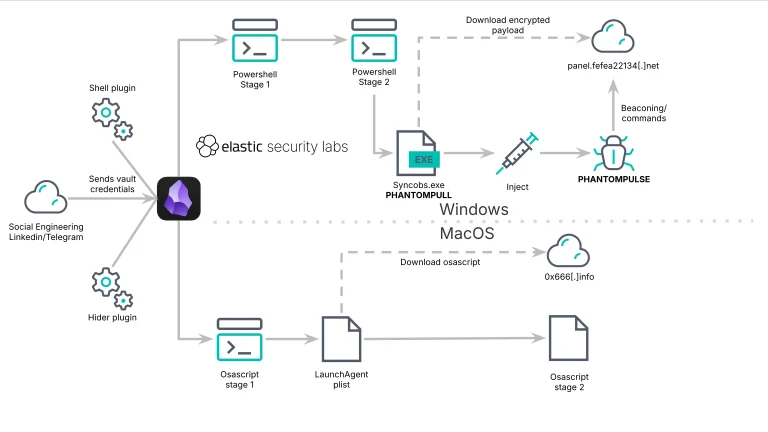
Elastic uncovers PHANTOMPULSE: A novel RAT abusing Obsidian plugins and blockchain C2. Stay safe from this AI-assisted campaign targeting crypto firms.

North Korea’s "graphalgo" campaign uses fake job interviews and real Florida LLCs to infect developers. Learn how to spot this sophisticated state-sponsored trap.

eSentire TRU uncovers STX RAT, a modular Trojan targeting finance with HVNC, AMSI Ghosting, and advanced encryption. Secure your perimeter—learn how it works.

Researchers unmask ResokerRAT, a stealthy Trojan using Telegram to spy on systems and block security tools like Task Manager. Is your PC calling home?

Google warns of a massive Axios supply chain attack. Versions 1.14.1 & 0.30.4 deploy the WAVESHAPER.V2 backdoor via a hijacked NPM account. Patch now!

Axios versions 1.14.1 & 0.30.4 have been poisoned. A hijacked maintainer account is dropping a RAT via postinstall scripts. Revert to safe versions now!
Malwarebytes uncovers a PureHVNC RAT campaign using Google Forms to bait professionals. Learn how this stealthy infection chain targets 2026 business docs.

Cyfirma uncovers the RuTaxi Android banking Trojan, a highly persistent malware using VNC capabilities to hijack Russian bank accounts and crypto wallets.

Socket researchers uncover a Packagist supply chain attack where fake Laravel utility packages secretly install a persistent Remote Access Trojan (RAT).