
 Do Son
CYFIRMA reveals a new cyber espionage campaign by Transparent Tribe (APT36) targeting Indian defense with stealthy multi-stage malware and decoy PDFs.
rat

Cofense uncovers a stealthy campaign abusing legacy WebDAV in Windows File Explorer to bypass browsers and EDR, delivering XWorm and Async RAT via UNC paths.
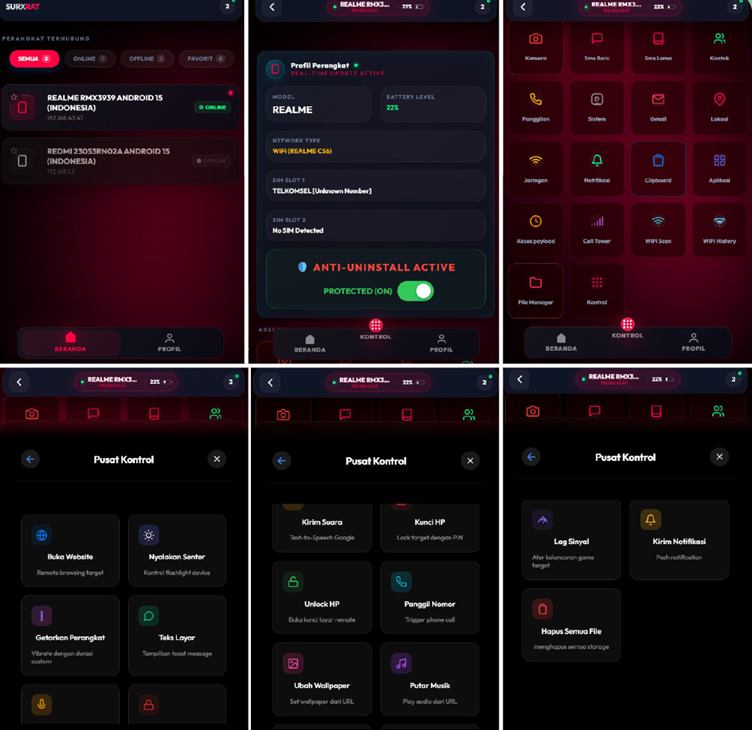
Cyble Research unmasks SURXRAT V5, a professionalized Android RAT experimenting with AI-assisted modules and hybrid monetization via Firebase infrastructure.
Cybercriminals are using fake DocuSign emails and the JWrapper framework to stealthily deploy SimpleHelp remote access tools. Learn how to spot the threat.
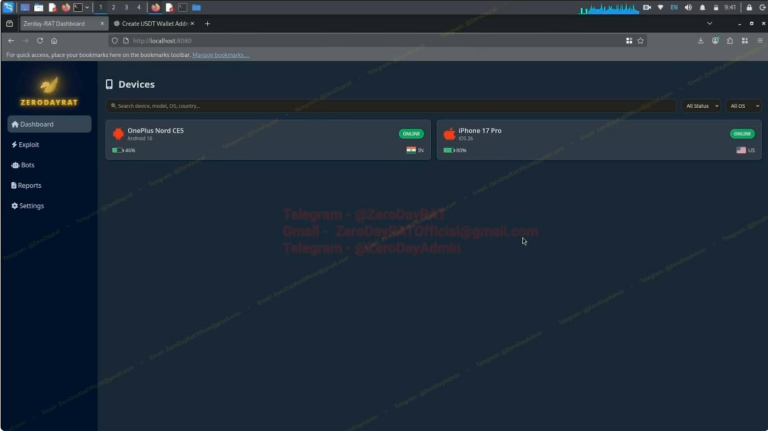
ZeroDayRAT mobile spyware is sold on Telegram. It offers full remote control of Android & iOS devices, including camera streaming & crypto theft.

Phishing emails use malicious Excel files to deploy XWorm RAT. The fileless attack exploits CVE-2018-0802 to steal data & control systems.

Stan Ghouls group targets Uzbekistan via fake court emails and malicious Java loaders. Learn how they deploy NetSupport RAT to spy on victims.
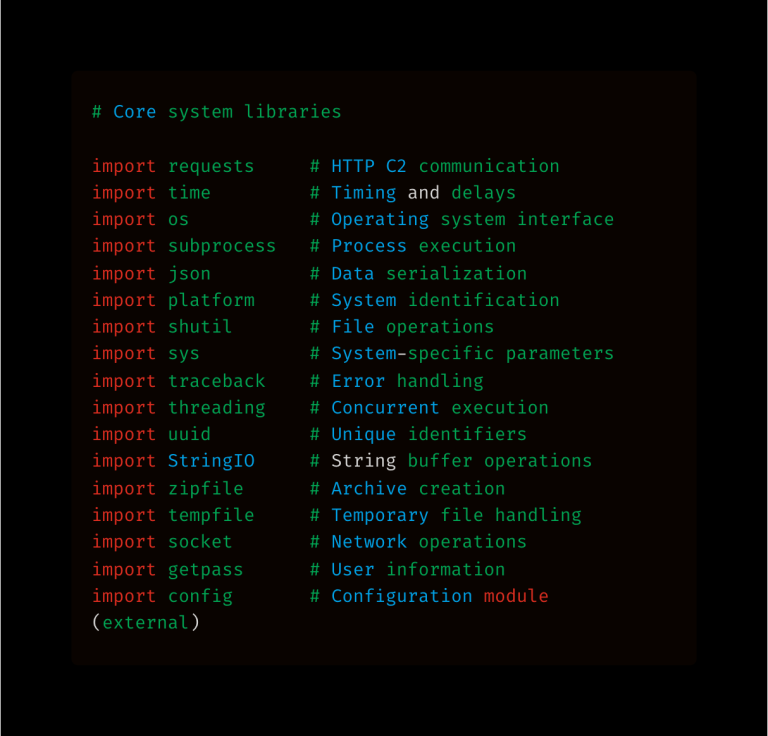
K7 Labs uncovers a stealthy Python-based RAT disguised as an ELF binary. Features adaptive beaconing and anti-forensics to stay hidden. Read the analysis.
CYFIRMA unmasks APT36's latest campaign: a fake JLPT exam lure using fileless LNK malware to evade antivirus and spy on Indian government targets.

SEQRITE Labs uncovers a China-linked campaign targeting Indian firms with fake tax notices to install persistent Remote Access Trojans.

Kimsuky is deploying a new DOCSWAP RAT via QR codes and smishing. The DPRK-linked malware turns phones into surveillance tools for data theft.

PyStoreRAT, a new fileless RAT, is spreading via fake GitHub repositories targeting developers. It executes as a JS implant via mshta.exe and includes explicit evasion logic against CrowdStrike.

A new C-compiled RAT, CastleRAT, uses Steam Community pages to hide its C2. The malware deploys advanced features like UAC Bypass, screen capture, and clipboard hijacking for espionage.

A deep-dive on Lazarus’s ScoringMathTea RAT reveals a full reflective DLL injection system, TEA/XTEA C2 encryption, and a polyalphabetic cipher for API hashing—a highly evasive tool for espionage.

Akamai exposed a malware that hides RAT C2 traffic by spoofing LLM chat-completion API requests on Tencent Cloud Serverless Functions. The payload is delivered via LNK/Sangfor DLL sideloading.

A new campaign is using Bitcoin wallet lures to distribute DarkComet RAT. The UPX-packed trojan gains persistence via a fake explorer.exe binary and uses keylogging and remote control to steal data.

NTT exposed WaterPlum APT's multi-platform OtterCandy RAT (v2), which uses Node.js for remote control, targets 7 browser extensions, and now includes anti-forensic trace deletion.

Seqrite discovered a campaign using SVG smuggling and a fake Colombian court lure to deploy AsyncRAT. The SVG executes JS to stage a malicious HTA file, evading detection.

Ransomware groups are hijacking legitimate RATs like AnyDesk and Splashtop to gain stealthy persistence, spread laterally, and disable antivirus software in enterprise networks.

XWorm V6.0 has resurfaced with 35+ plugins, including ransomware functionality. The modular RAT uses stealth injection and obfuscated PowerShell to bypass AMSI.

Huntress details a multi-stage attack that uses DLL sideloading and obfuscated Python to deliver PureRAT, a commercial-grade remote access trojan linked to PXA Stealer.

A new campaign uses a malicious LNK shortcut sent via Discord to deploy a multi-functional RAT that hijacks legitimate Windows binaries to evade detection.