
 Do Son
Multiple critical vulnerabilities (CVSS up to 9.8) in Alcatel-Lucent OmniAccess Stellar WLAN APs enable unauthenticated remote code execution and full device takeover. Patch immediately!
rce

NVIDIA patched critical vulnerabilities in its Container Toolkit and GPU Operator, allowing privilege escalation, data tampering, and DoS in containerized environments.

A critical pre-authentication root RCE (CVE-2025-34068) in Samsung WLAN AP WEA453e allows full device takeover. Update firmware immediately to version 5.2.4.T1.

A critical SSTI flaw (CVE-2025-53833, CVSS 10.0) in LaRecipe allows unauthenticated RCE on affected servers via template injection. Update to v2.8.1 immediately!

CISA adds critical Wing FTP Server RCE flaw (CVE-2025-47812, CVSS 10.0) to KEV. Actively exploited via null byte and Lua code injection; patch to 7.4.4 immediately!

A flaw (CVE-2025-53101) in ImageMagick allows stack buffer overflows via filename templates, risking memory corruption and remote code execution. Patch now!

A critical RCE flaw (CVE-2025-5333) in Symantec Endpoint Management (Altiris) allows unauthenticated attackers to execute arbitrary code via insecure .NET Remoting deserialization.

Fortinet released a critical patch for FortiWeb (CVE-2025-25257). This unauthenticated SQL injection flaw allows remote code execution. PoC Releases!

CYFIRMA unveils RenderShock, a zero-click attack strategy exploiting silent OS background processes like file previews and search indexing to execute malware and steal credentials without user interaction.

CERT/CC warns of critical flaws in Gigabyte UEFI firmware, allowing SMRAM writes and SMM code execution. Patch immediately to prevent firmware implants and Secure Boot bypass.

Axis warns of a critical flaw (CVE-2025-30023, CVSS 9.0) in Camera Station Pro/5 and Device Manager, allowing authenticated RCE via protocol deserialization. Update immediately.

A supply chain attack injected backdoor malware into Gravity Forms plugin downloads from the official website. The backdoor allows RCE and creates admin accounts.

Two flaws (CVE-2025-6376/6377 in Rockwell Arena Simulation allow RCE via crafted DOE files. Update to 16.20.09 immediately; avoid untrusted files.

Huntress witnessed active exploitation of a critical RCE flaw (CVE-2025-47812) in Wing FTP Server, allowing root/SYSTEM access via null byte injection and Lua code execution.
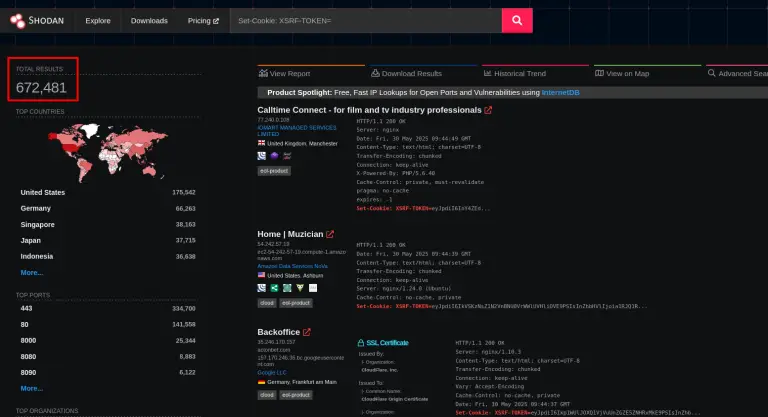
Synacktiv reveals Laravel’s APP_KEY vulnerability allows RCE via deserialization attacks when the key is leaked or guessable, risking full application compromise.

A critical flaw (CVE-2025-6691, CVSS 8.8) in the SureForms WordPress plugin allows unauthenticated arbitrary file deletion (e.g., wp-config.php), leading to full site takeover.

A critical flaw (CVE-2025-7206, CVSS 9.8) in D-Link DIR-825 firmware 2.10 allows unauthenticated remote buffer overflow, crashing the web interface.

Multiple critical flaws (CVE-2025-44954, -44957, -44963, -44955, -6243) in Ruckus vSZ/RND allow unauthenticated RCE, auth bypass via hardcoded SSH keys and JWT.

Schneider Electric warns of critical flaws (CVSS 10.0 RCE, SSRF, EoP) in EcoStruxure IT Data Center Expert. Patch to v9.0 immediately to prevent data center disruption.

GeoServer's RCE flaw (CVE-2024-36401) is actively exploited to deploy NetCat reverse shells and XMRig CoinMiners on Windows/Linux, hijacking resources.

Unit 42 reveals "Gold Melody" uses leaked ASP.NET Machine Keys to achieve in-memory RCE via View State deserialization and privilege escalation via GodPotato, compromising web servers.

The Git Project has released updates addressing three significant vulnerabilities impacting Git versions up to v2.50.0, including...