
 Do Son
Critical CVSS 9.8 RCE in Netflix Conductor lets attackers gain remote shell via JavaScript injection. Exploit PoC available. Patch now!
rce

DataEase has critical flaws in database connection handling, allowing remote RCE and JDBC parameter bypasses for H2, Redshift, and PostgreSQL. Update to v2.10.11 now!

CERT@VDE and Pilz disclose critical flaws in IndustrialPI 4: unauthenticated remote bypass (CVSS 9.6) and RCE (CVSS 10.0) via exposed Node-RED. Update or mitigate immediately.

Electron has critical flaws: CVE-2024-46993 allows RCE via image buffer overflow, and CVE-2024-46992 is an ASAR integrity bypass on Windows.

A critical CSRF flaw (CVE-2025-53095, CVSS 9.7) in Sunshine game streaming host allows remote attackers to execute arbitrary system commands with admin privileges.

A critical vulnerability—CVE-2025-49596—affected the AI developer ecosystem in June 2025, when Oligo Security Research disclosed a severe...

Google has urgently patched a high-severity zero-day (CVE-2025-6554) in Chrome's V8 JavaScript engine. This type confusion flaw is actively exploited in the wild, risking RCE.

A critical flaw (CVE-2025-6328) in D-Link's EOL DIR-815 router allows remote code execution via a stack-based buffer overflow. No patches will be issued.

Six critical flaws in D-Link's EOL DIR-816 routers are exposed. No patches will be issued; replace device immediately to avoid remote code execution.

IBM warns of a critical RCE flaw (CVE-2025-36038) in WebSphere Application Server 8.5/9.0, allowing unauthenticated attackers to execute arbitrary code via serialization.
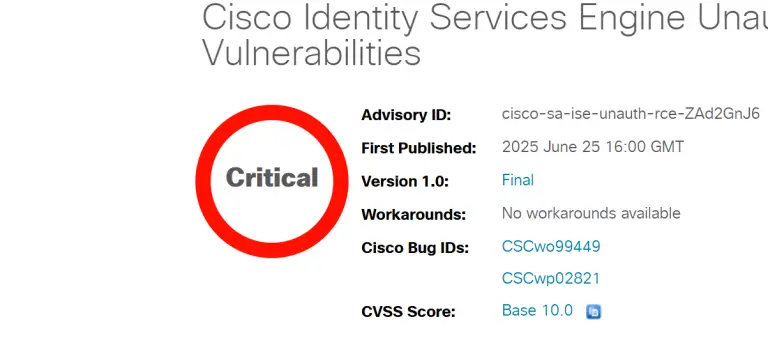
Cisco warns of two critical flaws (CVE-2025-20281, CVE-2025-20282, CVSS 10.0) in ISE and ISE-PIC allowing unauthenticated remote root code execution. Apply patches immediately.
CISA warns of critical flaws in MICROSENS NMP Web+ (v3.2.5 & earlier), including hardcoded JWTs, persistent sessions, and path traversal (CVSS 9.8 RCE). Update to 3.3.0 now!
Rapid7 warns of critical flaws (CVE-2024-51978, CVSS 9.8) in multi Brother printers, allowing auth bypass and RCE. Update firmware & change passwords immediately!
Quest KACE SMA faces critical flaws, including a CVSS 10.0 auth bypass (CVE-2025-32975) allowing full admin control. Update immediately to prevent RCE and compromise.
CISA warns of critical flaws in Kaleris Navis N4 terminal OS: unauthenticated RCE (CVSS 9.8) via Java deserialization and cleartext data transmission.

A critical flaw (CVE-2025-48703) in CentOS Web Panel allows unauthenticated RCE via authentication bypass and command injection, risking over 200,000 servers.

Elastic patches two Kibana flaws: CVE-2025-2135 (CVSS 9.9) allows heap corruption/RCE via Chromium, and CVE-2025-25012 (CVSS 4.3) is an open redirect/SSRF risk.

NVIDIA warns of two high-severity flaws in its Megatron-LM LLM framework, allowing RCE and privilege escalation via malicious file input.

JPCERT/CC warns of critical flaws in ELECOM wireless LAN routers, including unauthenticated RCE (CVSS 9.8) via Telnet/SOAP. Many affected models are unsupported; replace them immediately.

A rogue WordPress plugin is distributing multi-functional malware, performing credit card skimming, credential theft, ad fraud, and RCE through advanced evasion tactics.

Two severe Gogs flaws: CVE-2024-56731 (CVSS 10.0) allows RCE via symlink exploit, and CVE-2025-47943 (CVSS 6.3) is a stored XSS in PDF.js.

A critical flaw (CVE-2025-34037, CVSS 10.0) in Linksys E-Series routers allows unauthenticated remote command injection. TheMoon worm is actively exploiting it to infect devices.