 Do Son
A critical Rclone auth proxy bypass vulnerability exposes cloud storage. A public PoC is disclosed for GHSA-xwwr-4h3p-r22c and GHSA-p569-5gjg-9cmj.
Rclone

A critical rclone command execution flaw allows users to execute local commands. Secure your cloud synchronization setup against this risk.

Microsoft warns of a Teams campaign using fake IT support to hijack workstations via Quick Assist, move laterally with WinRM, and steal data using Rclone.
Technical details and PoC for Rclone’s critical 9.2 CVSS vulnerabilities (CVE-2026-41176/41179) are now public. Patch to version 1.73.5 to prevent RCE.
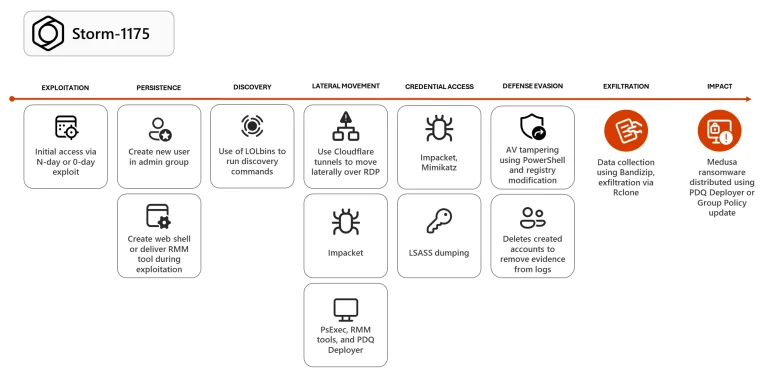
Microsoft exposes Storm-1175: a high-speed threat actor deploying Medusa ransomware in under 24 hours via zero-day exploits. Learn how to stop the blitz.

Google Drive access is vanishing in GNOME 50 and Ubuntu 26.04 LTS. Learn why the "libgdata" orphan caused this break and how to fix it using rclone in 2026.

Seqrite Labs exposes Operation CamelClone, a global cyber espionage campaign using the HOPPINGANT loader and public cloud services to evade detection.

New Osiris ransomware hits Southeast Asia, linking to Inc & Medusa groups. It uses BYOVD tactics to disable defenses. Unrelated to the 2016 variant.

Ashen Lepus (Hamas-APT) significantly evolved during the conflict, deploying the AshTag modular .NET malware suite. It uses in-memory execution and Rclone for stealthy cyber-espionage against diplomatic targets in the Middle East.

BlackSuit, a rebranded Royal/Conti ransomware, unleashes destructive multi-stage attacks. It uses Cobalt Strike, rclone for data exfil, and deletes shadow copies for stealth and speed.

A six-day RansomHub attack exploited RDP, used Atera/Splashtop RMM, Mimikatz, and Rclone to breach an enterprise, exfiltrate data, and deploy ransomware.

Discover the rise of Akira, a highly active Ransomware-as-a-Service (RaaS) group targeting organizations worldwide.