 Do Son
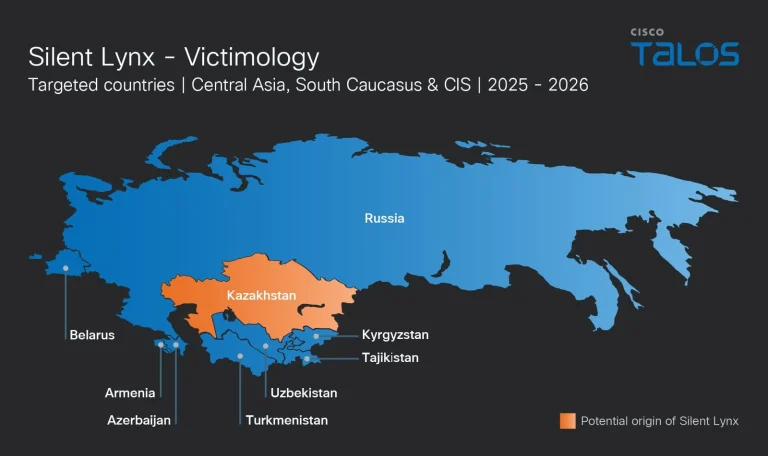
Cisco Talos and Recorded Future exposed the UAT-6275 threat actor targeting CIS governments with WinRAR exploits and custom reverse shells.
Recorded Future

Insikt Group discovered the TAG-182 threat cluster spreading MarkiRAT malware via fake VPN apps to spy on Iranians and alleged dissidents globally.

Russian group BlueDelta targets energy researchers in Europe & Middle East. Learn how they abuse free web services for credential harvesting.

DRAT V2, a new Delphi-compiled RAT from TAG-140 (SideCopy/Transparent Tribe), is targeting Indian government entities with expanded post-exploitation and refined C2 techniques.
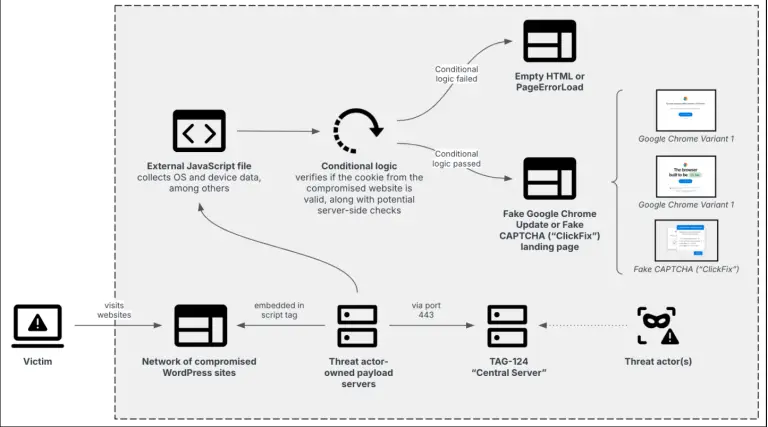
GrayAlpha, linked to FIN7, escalates tactics with fake browser/7-Zip updates and TAG-124 TDS, spreading NetSupport RAT in a multi-pronged infection campaign.