 Do Son
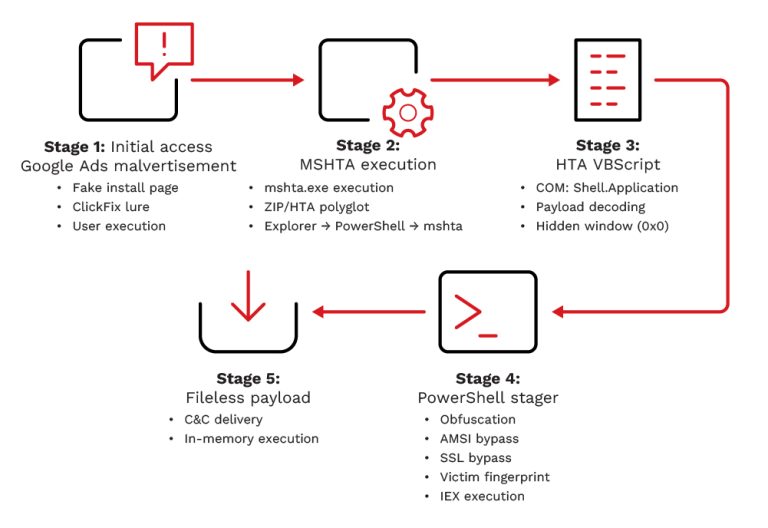
Beware of InstallFix: Fake Claude AI Google Ads trick users into running fileless scripts that deploy RedLine Stealer to steal passwords and crypto.
Redline stealer
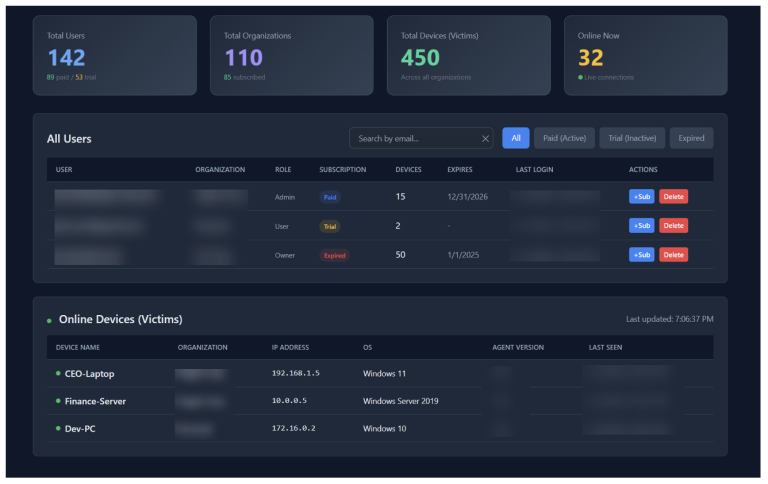
Proofpoint exposes TrustConnect, a new Malware-as-a-Service masquerading as an IT tool. The AI-assisted fake RMM software replaces dismantled threats.

CloudSEK exposes "RedLineCyber," an impostor hijacking crypto clipboards on Discord. This stealthy malware drains wallets without a C2 server.
Splunk exposes a campaign weaponizing Inno Setup installers to deploy RedLine Stealer, using obfuscated Pascal scripts and HijackLoader to steal browser/crypto data.

Beware of refund schemes targeting consumers in the Middle East. Learn how scammers exploit government portals and remote access tools to steal sensitive data and money.

Uncover the details of CVE-2024-43451, a zero-day vulnerability targeting Windows systems in Ukraine. Learn how attackers exploit URL files for malicious activity.

Researchers have uncovered a dangerous new variant of the Redline Stealer malware that uses clever obfuscation tactics
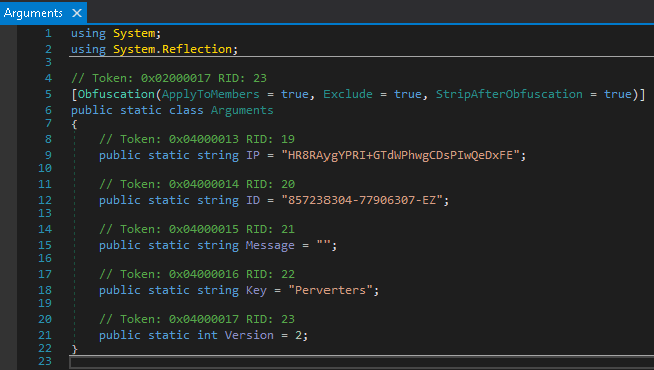
Among the myriad of threats, GuLoader and RedLine Stealer stand out for their sophisticated anti-analysis techniques.
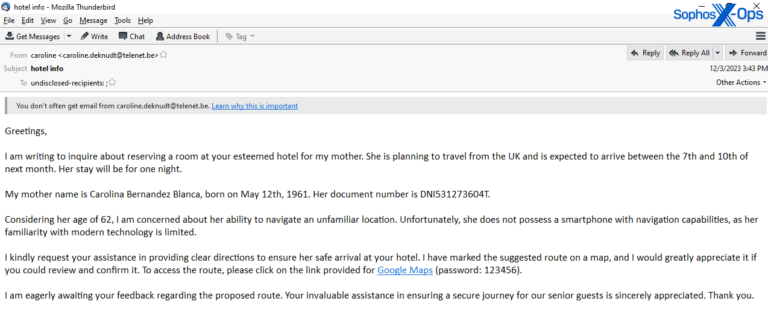
Sophos X-Ops warns that the "Inhospitality" malspam campaign represents a cunning blend of social engineering and malware

A marked increase in malicious advertisement campaigns circulating within Google's search engine, all bearing themes related to AI tools