 Do Son
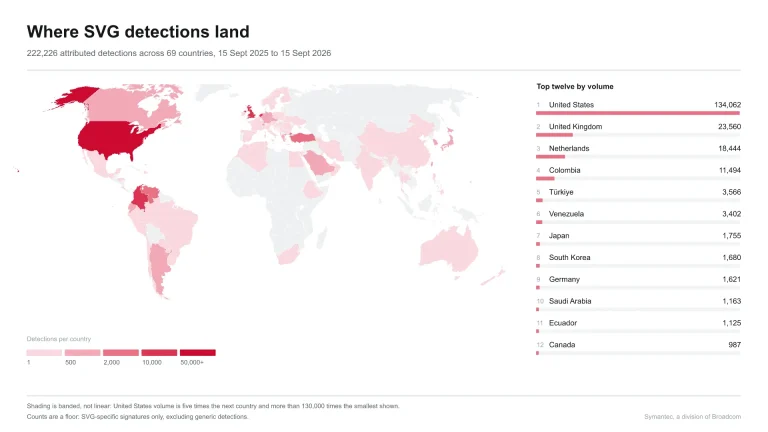
SVG phishing attacks jumped in August 2026. Symantec explains how SVG smuggling hides fake logins and malware inside image files, and how to stop it.
Remcos
A global phishing campaign hides a low-detection Lua loader inside fake .ttf font files to drop Remcos, XWorm, Agent Tesla, and a Snake Keylogger.
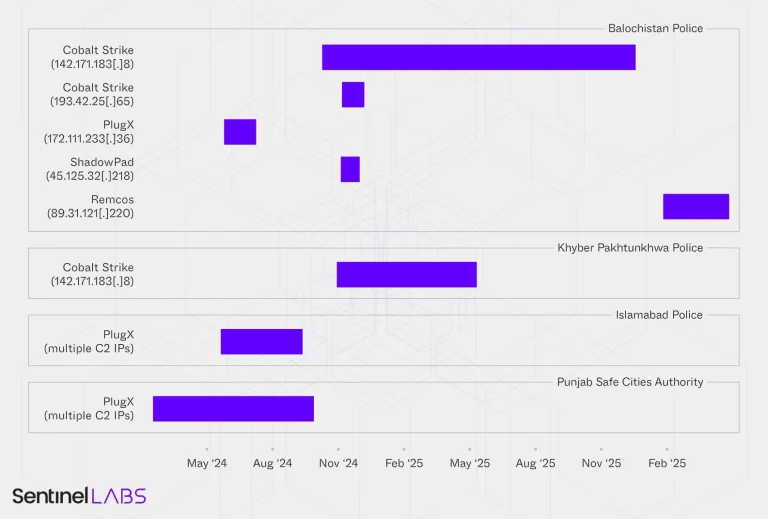
SentinelLABS found Chinese cyberespionage and India-nexus actors converging on Pakistani law enforcement, hitting Balochistan Police records and citizens.

Attackers exploit legitimate ahost.exe via DLL sideloading to deploy RATs & stealers. Trusted dev utility bypasses security scanners. Watch out.

A new stealthy campaign uses Windows LNK files to deploy the REMCOS backdoor via multi-stage PowerShell commands, bypassing antivirus and gaining full system control.

Trustwave exposes Blind Eagle (APT-C-36) leveraging exposed infrastructure and VBS malware in phishing campaigns, targeting Colombian banks with blatant disregard for concealment.

The SERPENTINE#CLOUD campaign exploits Cloudflare Tunnel subdomains and LNK files to deliver in-memory RATs like AsyncRAT and Remcos, evading detection.

Censys uncovers "sostener.vbs," an obfuscated VBScript launching a multi-stage RAT delivery pipeline, affecting dozens and potentially linked to Blind Eagle APT.

Learn how UAC-0006 Espionage is linked to Russian cyber operations targeting Ukraine through financial and psychological warfare.

Uncover the ongoing steganographic campaign that distributes malware like Remcos RAT. Learn how it operates.
Discover HeartCrypt, the powerful Packer-as-a-Service used by cybercriminals to protect malware from detection.

Uncover the targeted GuLoader campaign impacting European industrial and engineering companies. Learn about the evasive malware and its sophisticated tactics.

Recently, the group utilized the Spyder Loader as a means to disseminate the Remcos Remote Access Trojan (RAT)

Hackers disseminated phishing emails containing Remcos RAT attachments disguised as PDF files, sent by the Security Service of Ukraine