 Do Son
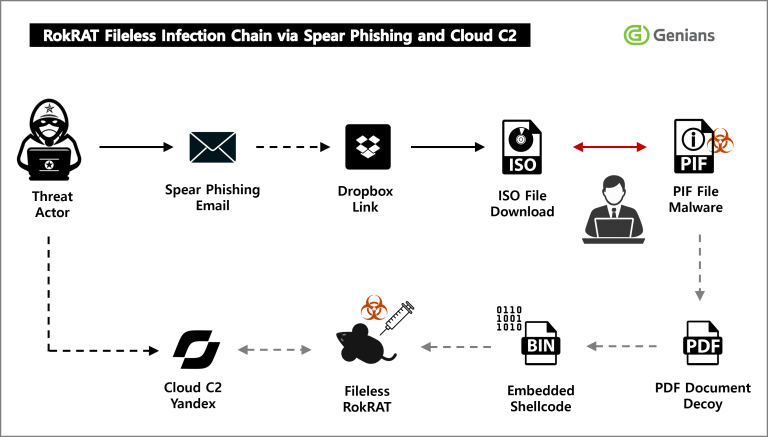
Genians exposed Operation Capsule Vault, an APT37 campaign. The RokRAT malware hides inside a fake PDF to spy on academics and researchers.
RokRAT
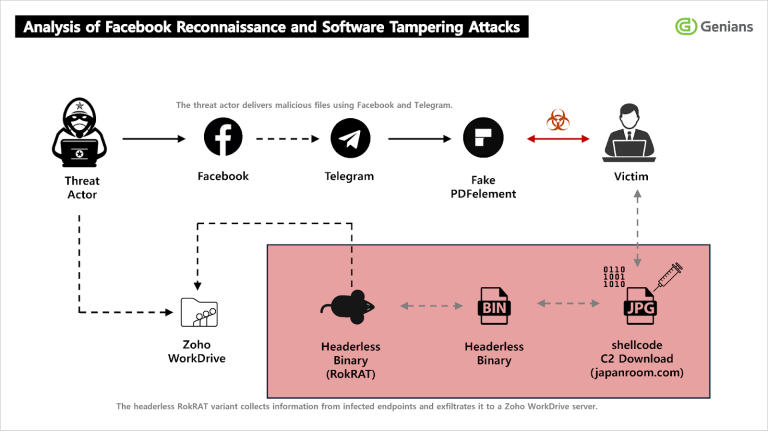
APT37 pivots to Facebook social engineering, using Wondershare PDFelement "code caves" to deploy RokRAT. Learn how they bypass EDR with memory-only payloads.

A new report reveals North Korea's APT-37 is using malicious LNK files in a campaign, "Operation HanKook Phantom," to spy on South Korean government and research.

APT37, a North Korea-linked group, is using a new RoKRAT backdoor to target South Korea. The malware uses stealthy LNK files and steganography to evade detection.

New report details APT37's "ToyBox Story" campaign, using spear phishing and cloud services to deploy RoKRAT malware. Fileless attacks and stealthy tactics revealed.

Learn how APT-C-28 operates in cyber espionage, targeting industries with advanced techniques and the RokRat Trojan.

Explore the impact of South Korean cyberattack threats on civil society organizations and their defenders in a detailed study.
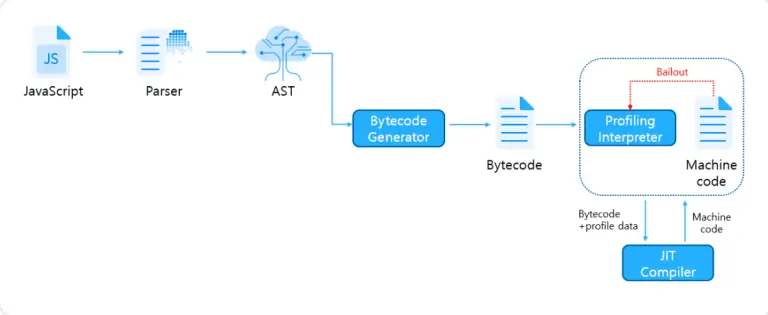
Learn about the sophisticated cyber attack dubbed 'Operation Code on Toast' and the North Korean-linked hacking group TA-RedAnt behind it.

SentinelLabs unraveled a campaign orchestrated by ScarCruft threat actor targeting media organizations and experts on North Korean affairs