 Do Son
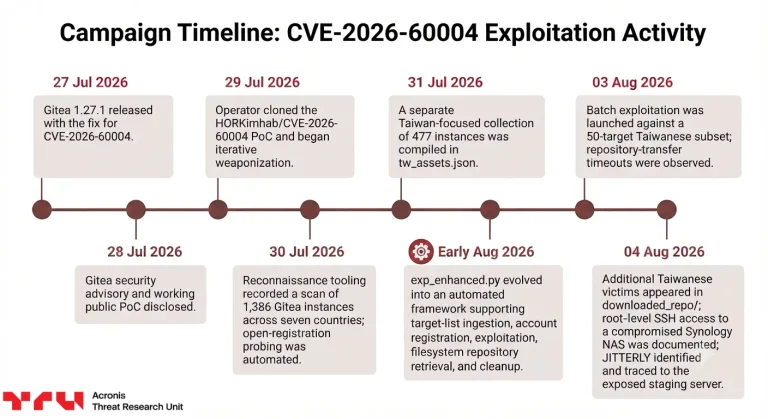
A critical Gitea RCE vulnerability exploited in wild attacks exposes servers. Patch this Gitea RCE vulnerability now to prevent full system compromise.
rootkit
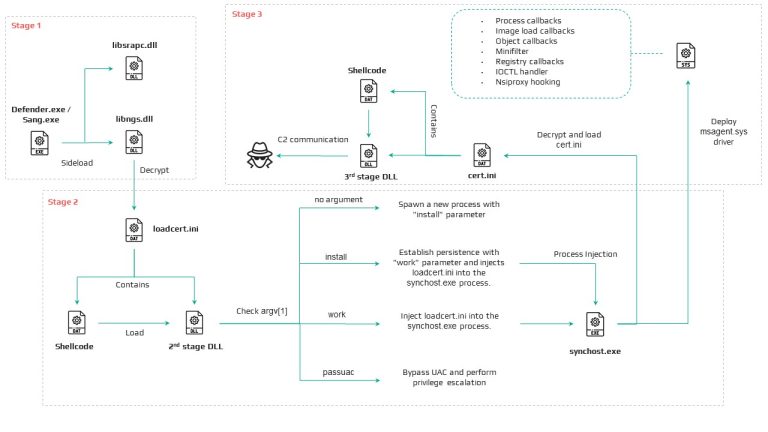
Kaspersky uncovered the new HoneyMyte CoolClient rootkit. The HoneyMyte CoolClient rootkit deploys a kernel driver to hide malware on Windows.
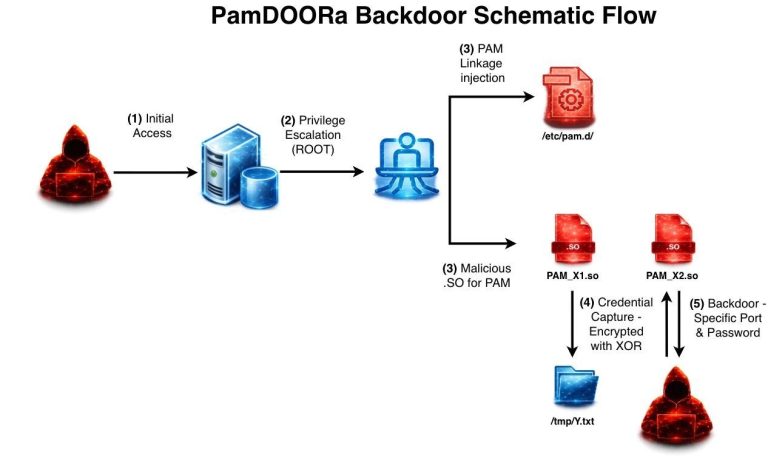
Flare unmasks PamDOORa: a $1,600 Linux backdoor that hijacks the PAM stack to harvest credentials and manipulate authentication logs to evade detection.
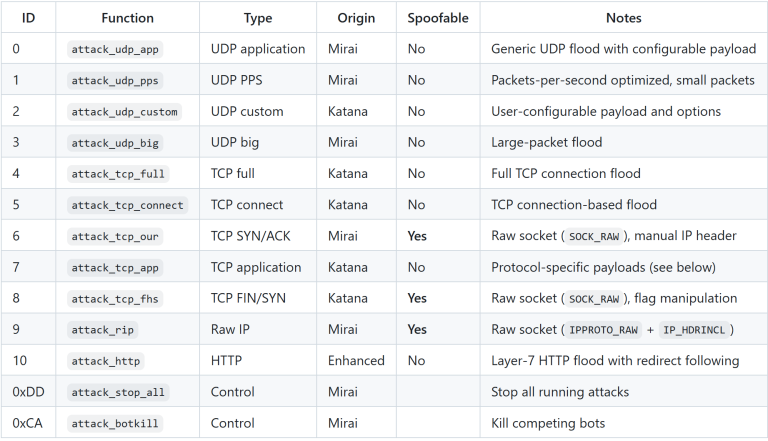
Nokia researchers uncover the Katana botnet, a Mirai variant using custom rootkits to hijack unmanaged Android TV boxes in a massive IoT turf war.

Kaspersky unmasks HoneyMyte's 2025 campaign, using the ProjectConfiguration.sys kernel rootkit to deploy ToneShell backdoors with elite stealth.

Aqua Security's Nautilus team discovered Koske, an advanced Linux cryptojacker likely crafted by AI, hiding in panda images and using rootkits for stealthy operations.

The Mimo threat actor has broadened its scope to Magento, employing advanced persistence, fileless execution, cryptojacking, and proxyjacking in a sophisticated new campaign.

Google's GTIG uncovers UNC6148 using stolen credentials and a new rootkit, OVERSTEP, to gain persistent access to end-of-life SonicWall SMA 100 series appliances.

A IGEL OS 10 flaw (CVE-2025-47827) allows full Secure Boot bypass, enabling attackers to load untrusted kernels and rootkits. No patch is available.

A Insyde H2O UEFI flaw (CVE-2025-4275) allows Secure Boot bypass via NVRAM, enabling attackers to inject undetectable malware and rootkits. Update firmware now!

Darktrace uncovers PumaBot, a stealthy Linux botnet using Go binaries, SSH brute-force, and rootkits to compromise IoT devices, aiming for persistent, undetected access.
ARMO researchers reveal how io_uring blinds Linux security tools like Falco, Tetragon, and Defender, exposing systems to undetected rootkit attacks.