 Do Son
A GL.iNet cloud zero-day in GoodCloud remote management was exploited to plant malware on routers and KVMs. How to check your device and patch.
router security
Zyxel firmware vulnerability CVE-2026-79614 (CVSS 9.8) allows unauthenticated command execution, and CVE-2026-86676 adds command injection. Patch now.
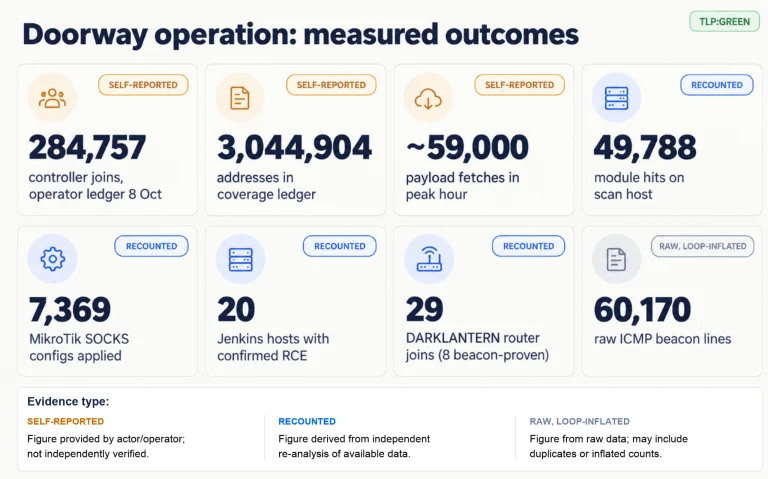
CloudSEK uncovers the Doorway botnet. The Rust Doorway botnet exploits routers, cameras, and servers to build a global proxy network.
Four ASUS router vulnerabilities are fixed, including critical XSS flaw CVE-2026-14911 and code execution bug CVE-2026-19386. Update firmware now.
Technical details and a PoC for the D-Link DAP-1360 vulnerability (CVE-2026-95675) are public. Learn how this unauthenticated flaw impacts legacy routers.
Public PoC exploit details emerge for critical D-Link DIR-822A vulnerabilities. Learn how these D-Link DIR-822A vulnerabilities impact unpatched devices.
A TP-Link Archer AX55 vulnerability (CVE-2026-18167) risks remote code execution via EasyMesh buffer overflow. Update to build 20260527 now.
TP-Link patches CVE-2026-75616, an Archer C20 command injection flaw that can lead to full device compromise. Update firmware now.
CVE-2026-75501 exposes an unauthenticated UPnP service on Calix routers. Public PoC code shows how attackers bypass NAT and firewall protections.

TP-Link patched 5 TP-Link router vulnerabilities in ISP-managed mesh, router, and modem lines, including auth bypass and command injection.

CVE-2026-9044 is a command injection flaw in TP-Link Archer AXE75 OpenVPN, CVSS 8.5. Update to firmware 1.5.6 Build 20260623 now.

A TP-Link TL-WR940N flaw, CVE-2026-12935, allows unauthenticated remote code execution via an RTSP stack buffer overflow. Update the router firmware now.

ASUS security advisories cover seven flaws. CVE-2026-13385 (CVSS 9.5) lets MITM attackers run commands on CN SKU routers. Update firmware now.
A 20-nation alert warns that Russia's FSB Center 16 is hacking vulnerable routers. The group targets critical infrastructure through weak SNMP settings.

CVE-2026-11405 is a Tenda authentication backdoor. It allows full administrative access without valid credentials. Protect your network with these steps.

A NetComm authentication bypass (CVE-2026-35019, CVSS 9.2) uses a hardcoded AES key to forge admin session cookies. Update to firmware R6B032 now.

Read the latest Gafgyt malware analysis revealing how the dangerous COXMO botnet variant spreads via standalone scripts.

A critical Archer MR600 command injection vulnerability surfaces within the WireGuard client configuration. Update your TP-Link firmware now.
A dangerous Acer router flaw allows a critical authentication bypass. Install the latest firmware patch to secure your network now.
A critical TP-Link router vulnerability affects Archer models. Download the latest CVE-2026-5509 patch immediately to secure your network environment.

ELECOM routers hit by critical 9.8 CVSS flaws (CVE-2026-42062). Unauthenticated attackers can execute OS commands and bypass auth. Update firmware now!
TP-Link urges Archer AX53 v1.0 users to update firmware to fix 5 critical flaws, including OS command injection & file leaks. Secure your network now!