
 Do Son
NCSC unmasks APT28’s "digital funnel" using router DNS hijacking to steal OAuth tokens and passwords. Protect your remote workforce—patch your routers now.
router security

ASUS issues an emergency 8.5 CVSS patch for routers (CVE-2025-15101). A CSRF flaw lets attackers hijack sessions and change settings. Update your firmware today!
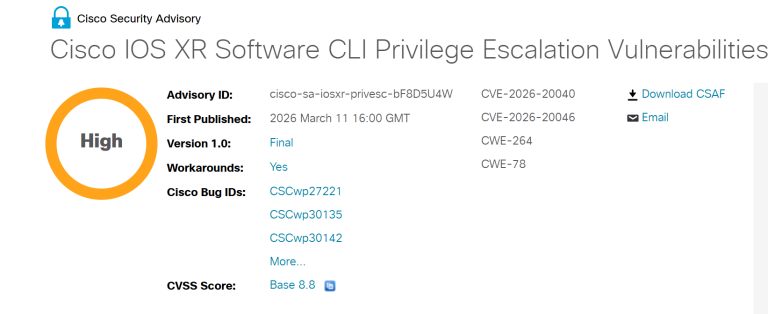
Cisco patches critical privilege escalation flaws (CVE-2026-20040, CVE-2026-20046) in IOS XR software that allow local attackers to gain full root access.

A critical 8.5 CVSS command injection flaw (CVE-2025-15568) in TP-Link Archer AXE75 routers allows complete root-level network takeover. Patch immediately.

Zyxel issues urgent patches for a critical 9.8 severity flaw (CVE-2025-13942) in UPnP functions that allows remote attackers to execute OS commands. Patch now!

Cisco Talos exposes DKnife, a router malware that inspects traffic and swaps legitimate downloads for ShadowPad backdoors. Active since 2019.
TP-Link discloses command injection flaws in Archer BE230 routers (CVE-2026-0630). Authenticated attackers can gain root access. Update firmware now.

CVE-2026-0625: Unpatchable D-Link routers face critical RCE attacks. Hackers are actively exploiting this zero-day. Replace legacy DSL models immediately.

JD Cloud alerts users to CVE-2025-66848, a 9.8 critical flaw allowing remote attackers to bypass auth and gain root access on NAS routers.

A Linksys zero-day (CVE-2025-52692) allows attackers to bypass login screens and enable Telnet for root access. No patch planned!

ASUS fixes 8 severe router flaws, including a critical AiCloud authentication bypass (CVSS 9.4). Users must update firmware immediately to patch vulnerabilities.

D-Link warned that DIR-878 has reached EOL with three unpatched RCE flaws. Unauthenticated remote attackers can execute arbitrary commands via Dynamic DNS and DMZ settings due to insecure CGI parameters.

A new report reveals a CWMP service flaw in TP-Link routers that can be exploited for RCE. Researchers have published a detailed write-up and a PoC on GitHub.

CISA adds two flaws to its KEV Catalog: a TP-Link factory reset flaw and a WhatsApp zero-click vulnerability used in targeted spyware attacks. Patching is urgent.

FBI warns cybercriminals are exploiting outdated routers with TheMoon malware to build anonymous proxy networks for illicit activities.

TP-Link WR841N routers are vulnerable to a stored XSS attack. Update firmware and change your password to protect your device from potential admin password theft.

RustoBot, a sophisticated botnet written in Rust, is exploiting vulnerabilities in TOTOLINK & DrayTek routers to launch DDoS attacks. Learn how this malware operates and how to protect your network.

ASUS routers have a critical vulnerability (CVE-2025-2492) allowing unauthorized access. Update firmware and strengthen security now.