 Do Son
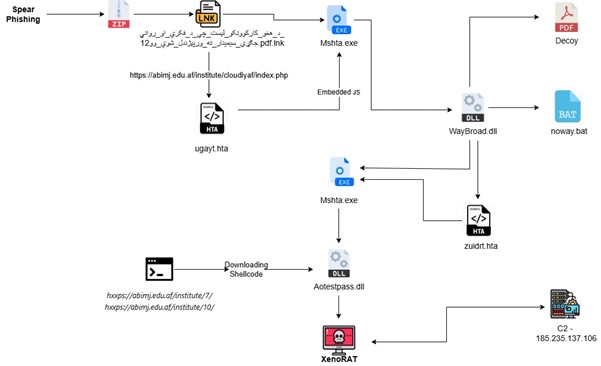
A deep look at the SideCopy XenoRAT malware attack targeting the Afghan Ministry of Finance. Learn how Operation XENOFISCAL bypasses defenses.
Seqrite Labs
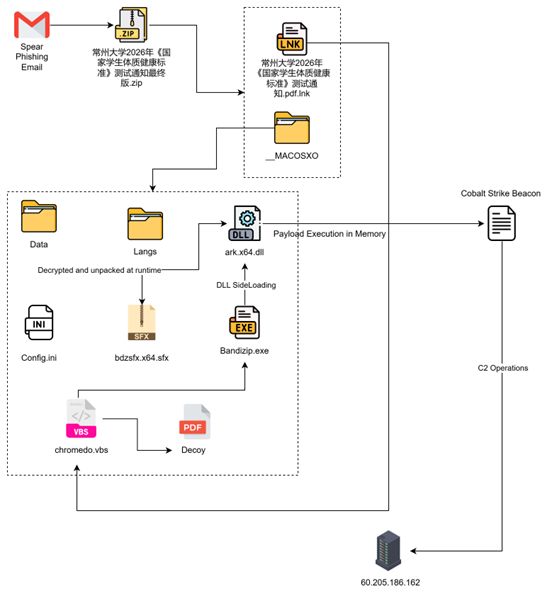
Discover how the Operation Dragon Whistle phishing campaign leverages student fitness lures to deploy stealthy memory-only malware.
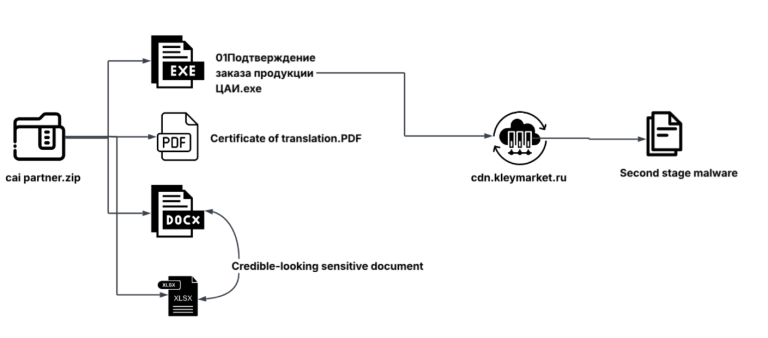
SEQRITE Labs uncovers Operation Silent Rotor, a targeted Rust-based cyberattack on the Eurasian unmanned aviation sector ahead of the 2026 Moscow forum.
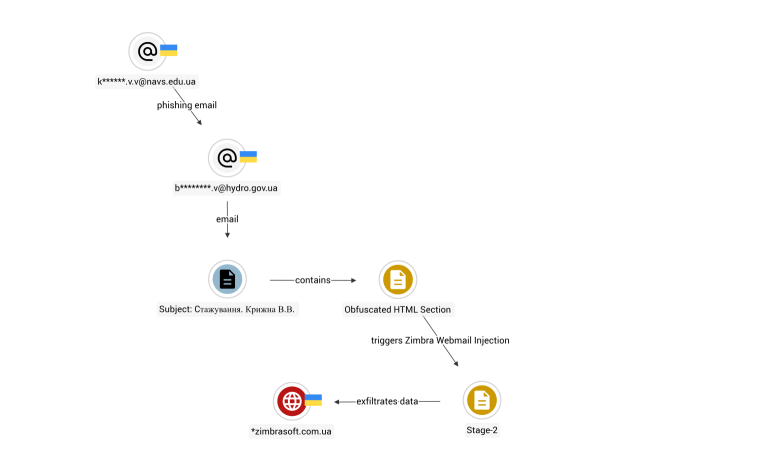
Seqrite Labs uncovers Operation GhostMail, an APT28-linked campaign using a zero-click XSS flaw in Zimbra to silently hijack Ukrainian government webmail.

Seqrite Labs exposes Operation CamelClone, a global cyber espionage campaign using the HOPPINGANT loader and public cloud services to evade detection.

Seqrite exposes "Operation Covert Access": A Rust RAT targeting Argentina's legal system via fake court rulings. Includes anti-analysis & encryption tools.

Nomad Leopard targets Afghan officials with fake ministry docs. SEQRITE reveals how the "afghanking777000" OPSEC fail exposed the spies.
SEQRITE Labs uncovers Operation IconCat, a campaign by UNG0801 using spoofed SentinelOne and Check Point icons to deploy PYTRIC and RUSTRIC in Israel.

SEQRITE Labs uncovers a China-linked campaign targeting Indian firms with fake tax notices to install persistent Remote Access Trojans.

A new campaign uses encrypted VBScript (.VBE) to deploy a fileless Masslogger infostealer, which hides in the Windows Registry to steal credentials and evade antivirus.
Seqrite Labs uncovers APT36 phishing campaign using Pahalgam terror attack-themed lures to deploy Crimson RAT against Indian government targets.