 Do Son
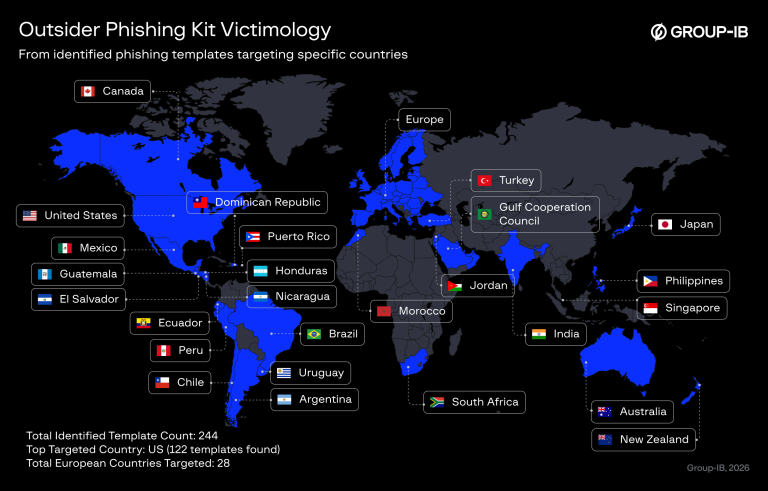
The Outsider Phishing Kit persists despite the Operation Ghost Hook takedown. Discover how the ChenLun Outsider PhaaS kit bypasses MFA via AiTM attacks.
smishing

Read the Group-IB phishing report detailing the massive Smishing Error524 campaign targeting millions across 72 countries with advanced evasion tactics.

Bitdefender uncovers a massive smishing campaign targeting drivers with fake toll and parking fines. Over 79,000 messages sent across 12 countries.

Group-IB unmasks the Phoenix System: a PhaaS platform using rogue cell towers and live-dashboards to bypass MFA across 2,500+ domains. Read the full report.

Discover how Operation False Siren weaponizes Israel's Red Alert app via smishing, deploying advanced Android spyware for geo-fenced mobile espionage.
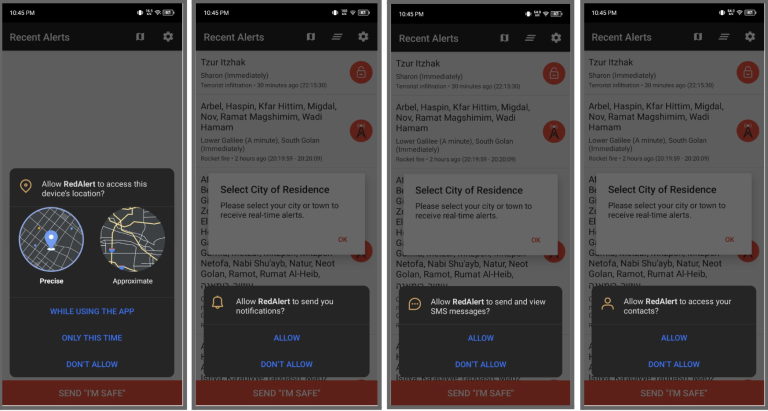
CloudSEK exposes a smishing campaign spreading a trojanized "Red Alert" app. The fake emergency tool tracks locations and steals data during air raids.

New "PayTool" fraud cluster targets Canadians via fake Gov & Air Canada sites. CloudSEK reveals how this PhaaS operation steals Interac logins.

Scammers target PNB MetLife users via mobile phishing. Attackers use Telegram bots to steal data & manipulate clipboards for UPI fraud.

Kimsuky is deploying a new DOCSWAP RAT via QR codes and smishing. The DPRK-linked malware turns phones into surveillance tools for data theft.

Frogblight, a new Android banking Trojan, is targeting Turkey via smishing with fake e-government apps. It uses WebView to steal credentials and is linked to the Coper MaaS family. It is being actively developed.

Unit 42 exposed the Smishing Triad, a PhaaS network that registered 194K+ malicious domains for global smishing. The group impersonates postal/banking services and uses Telegram for its underground market.
A Grooza cluster smishing campaign is exploiting unauthenticated APIs on 500+ industrial routers (Milesight) to send phishing texts impersonating Belgian and French government services.

SikkahBot, a new Android malware, is impersonating scholarship apps to steal financial data and automate transactions from students in Bangladesh.

A new report reveals Chinese-speaking smishing syndicates are using phishing-as-a-service, MFA bypass, and stolen cards to conduct a multi-billion dollar fraud campaign targeting digital wallets.

Chinese cybercriminals are escalating attacks on the Philippine financial sector, exploiting NFC technology and smishing to steal from mobile wallets, with a 230% surge in dark web activity.

A Chinese student was jailed in London for running a smishing campaign with an "SMS Blaster" hidden in his car, spoofing texts to steal data.


mnemonic exposes Darcula, a global phishing-as-a-service network using the Magic Cat toolkit to target mobile users with encrypted, real-time scam dashboards.
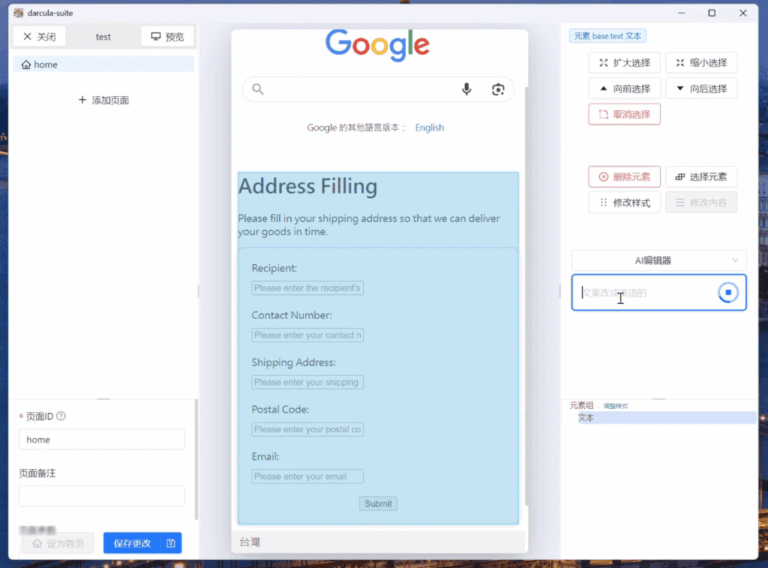
Darcula-Suite integrates AI to supercharge phishing-as-a-service operations, enabling faster, scalable, and more convincing phishing campaigns worldwide.

A widespread smishing campaign targeting toll road users across multiple U.S. states is stealing payment credentials. Learn how scammers are impersonating E-ZPass and other toll systems to trick victims

Silent Push reveals Smishing Triad's widespread SMS phishing campaigns targeting 121+ countries. The group uses sophisticated kits to steal credentials and financial data.

Uncover the sophisticated SilkSpecter phishing campaign targeting e-commerce shoppers during Black Friday. Learn how this financially motivated threat actor lured victims with fake discounts.