 Do Son
Socket uncovers malicious Firefox extensions spoofing Phantom, Jupiter, and Bitget. These malicious Firefox wallet extensions steal seed phrases.
Socket
A LiteLLM supply chain attack shipped a PyPI credential stealer in version 1.107.0 that grabs cloud, AI tool, and SSH secrets. Act now.
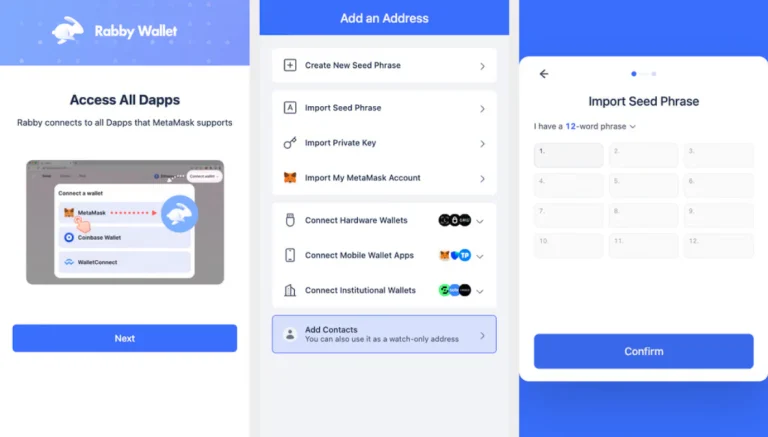
Socket found 16 malicious Firefox extensions posing as Rabby and OKX. These crypto wallet stealers grabbed seed phrases. Here is what to do.
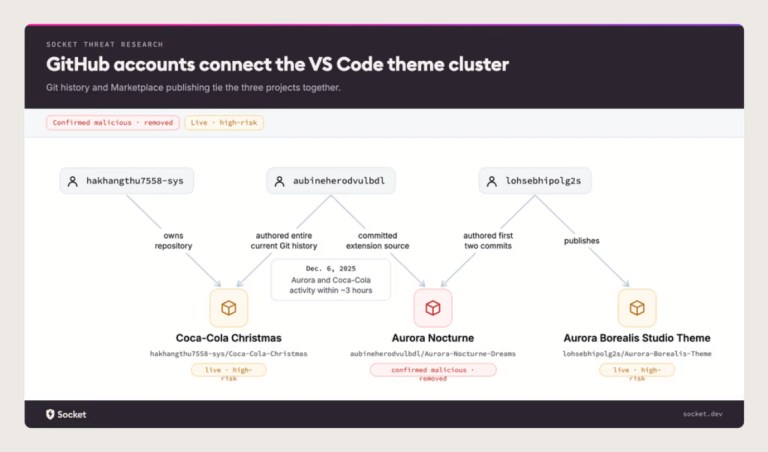
Socket links GlassWorm VS Code themes to malicious VS Code extensions with 8,000+ installs, including a Coca-Cola theme. See how to check yours.
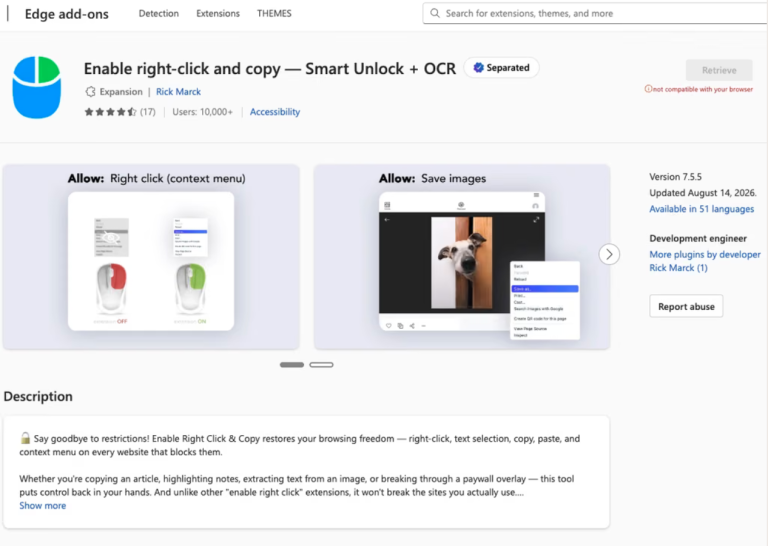
Socket found 19 malicious browser extensions acting as a crypto wallet drainer across Chrome and Edge, exposing up to 80,000 users in one case.
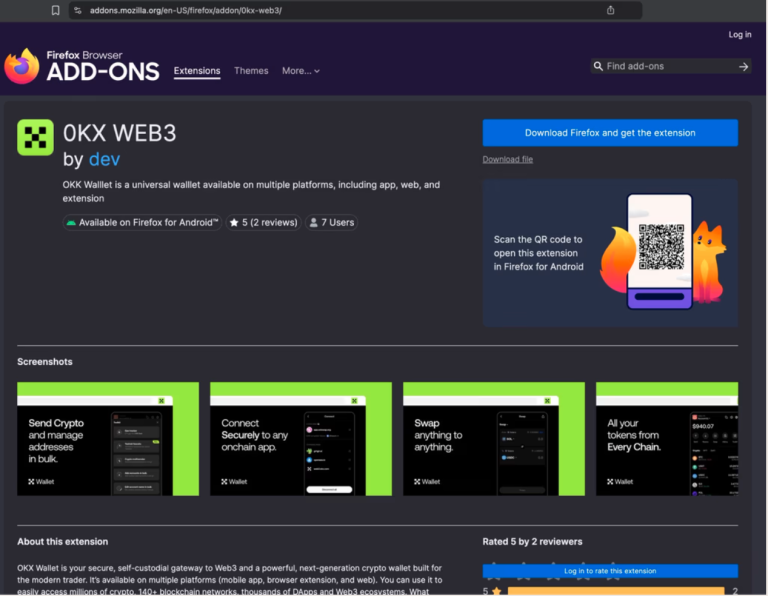
Socket tracked 77 malicious Firefox extensions that steal crypto wallet secrets and credentials. See how the Offside Wallet Theft Factory works.
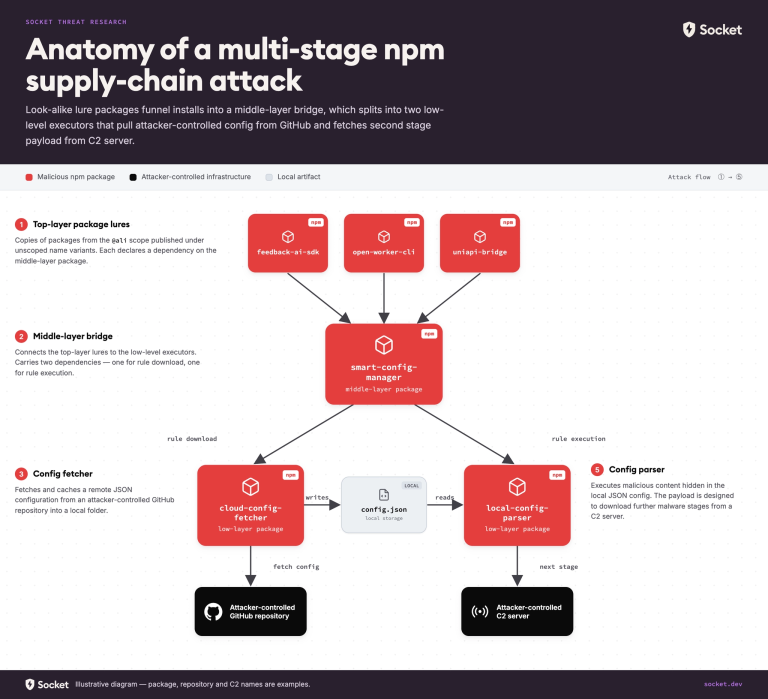
A distributed npm supply chain attack dropped a cross-platform RAT on Alibaba developers. Socket found malicious npm packages hiding loader code.
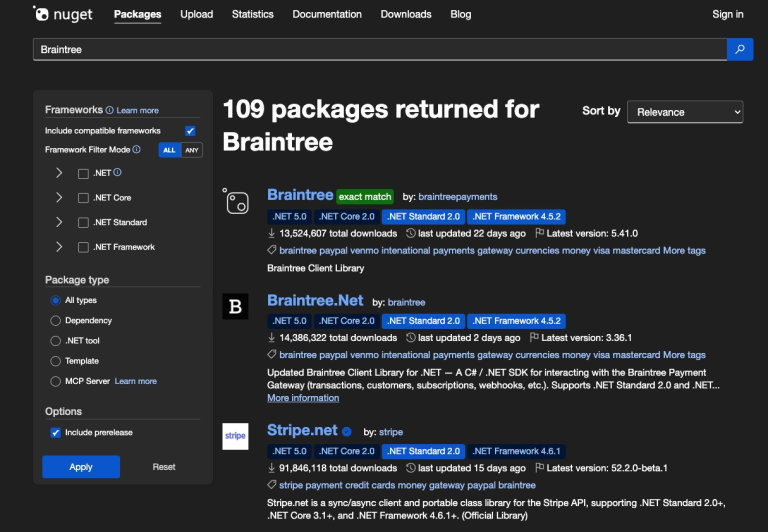
A malicious NuGet package, Braintree.Net, acts as a credit card skimmer and steals merchant API keys. The Braintree NuGet typosquat hits .NET devs.
A malicious Go module exposed a GitHub lure network of 222 repositories, dubbed Operation Muck and Load, staging RATs and infostealers.
Socket links the PolinRider supply chain attack to North Korean hackers. The campaign hid loaders in 108 open-source packages across four ecosystems.
A Mastra supply chain attack compromised 140+ npm packages, using the typosquatted easy-day-js dependency to drop a crypto-stealing infostealer.
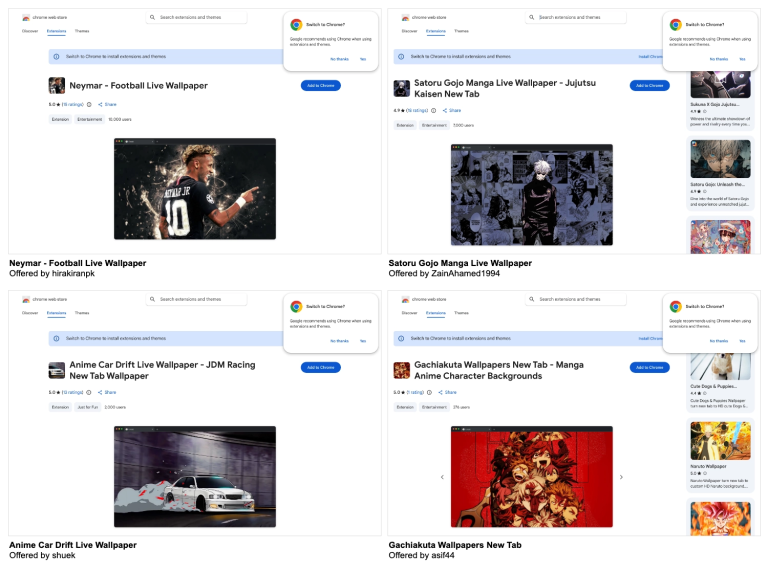
Discover how malicious Chrome extensions engage in traffic laundering while lying to users about collecting data on the official store.

A massive PyPI supply chain attack has hit developers. Learn how Socket malware detection uncovered the Hades cluster stealing cloud credentials.

GemStuffer exploits RubyGems as an illicit data transport to scrape UK council portals. Discover how this supply chain attack bypasses standard defenses.
Socket uncovers a BufferZoneCorp "sleeper" campaign targeting Ruby and Go. Malicious packages steal SSH keys and subvert CI/CD pipelines. Patch now!
Socket uncovers a massive Mini Shai-Hulud breach in the Intercom PHP SDK. Malicious version 5.0.2 steals cloud secrets and GitHub tokens. Rotate keys now!
Socket uncovers GlassWorm: a 73-extension sleeper campaign on Open VSX targeting VS Code and Cursor. Stealthy .node binaries turn trusted tools into malware.
North Korea’s "Contagious Interview" campaign expands to 1,700+ malicious packages across npm, PyPI, and more. Learn how to protect your dev environment.

Socket reveals how an AI bot hijacked the Aqua Trivy VS Code extension, using prompt injection to turn developer AI assistants into stealthy data thieves.

Socket uncovers "StegaBin," a North Korean malware campaign hiding C2 URLs in Pastebin essays to steal developer secrets via 26 typosquatted npm packages.

Socket uncovers an npm-based phishing campaign using CDNs to host lures targeting sales teams in critical infrastructure via fake MicroSecure pages.

The malicious 'Crypto Copilot' Chrome extension drains Solana funds from traders on X by injecting hidden transfers. Remove this malware immediately.