 Do Son
SolarWinds Observability vulnerabilities allow RCE via CVE-2026-28324. Update to version 2026.2.3 to secure your monitoring infrastructure today.
SolarWinds
A SolarWinds Web Help Desk SAML authentication bypass, CVE-2026-28323, scores a critical CVSS 9.8. Update to 2026.2.1 to stay protected.

SolarWinds patched 15 critical Serv-U vulnerabilities enabling privilege escalation, account takeover, and RCE as root. Update to Serv-U 2026.3 now.

Protect your network from active CVE-2026-28318 exploitation. Apply patches for this critical Serv-U vulnerability before the June 19 deadline.
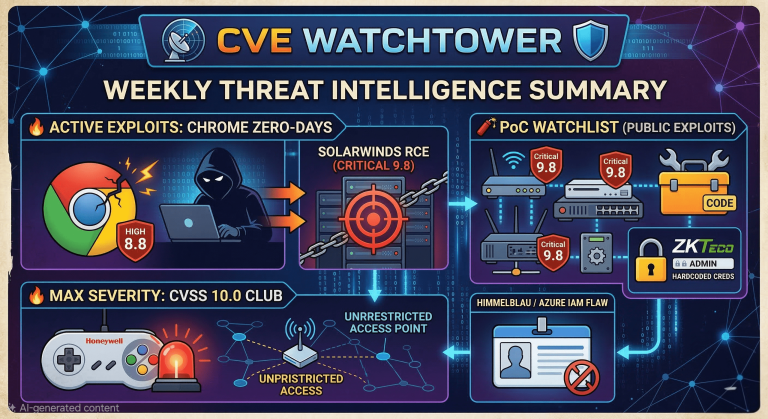
Google Chrome zero-days and a CVSS 10.0 building controller flaw top this week's 1,388 new CVEs. Patch the perimeter before threat actors automate the exploit.
CISA adds three actively exploited flaws in SolarWinds, Ivanti, and Omnissa to its KEV catalog. Patch these critical enterprise vulnerabilities immediately.

Microsoft finds hackers using SolarWinds WHD to run hidden QEMU VMs. The attack uses DLL sideloading for full domain compromise. Patch immediately.
The clock is ticking for organizations running SolarWinds Web Help Desk (WHD), as a nightmare scenario unfolds:...

Critical SolarWinds Web Help Desk flaws (CVSS 9.8) allow unauthenticated RCE and auth bypass. Hardcoded credentials also found. Patch immediately.
SolarWinds has released an urgent hotfix for its Web Help Desk software, patching an unauthenticated RCE vulnerability (CVE-2025-26399) that bypasses earlier fixes.

SolarWinds alerts on a Salesforce data breach impacting numerous companies. The breach exploited compromised OAuth tokens via the Salesloft Drift integration, exposing sensitive customer data.
Alarming rise of cyber threats targeting the UK by Russian threat actors. Learn about the dangerous shift in geopolitical tensions and their impact on critical infrastructure.

Discover the details & PoC exploit for the critical SolarWinds WHD flaw CVE-2024-28987. Protect your organization's sensitive IT support data
Find out about the security risks posed by the CVE-2024-28991 & CVE-2024-28990 vulnerability in SolarWinds Access Rights Manager software.

Urgent security advisory: SolarWinds' Web Help Desk (WHD) software vulnerable to critical hardcoded credential vulnerability (CVE-2024-28987).

Urgent security advisory: SolarWinds Web Help Desk vulnerability (CVE-2024-28986) allows unauthorized users to run arbitrary commands.

SolarWinds has issued an urgent security advisory regarding multiple critical vulnerabilities discovered in its Access Rights Manager product

CVE-2024-28995 is a path-traversal vulnerability that allows unauthenticated attackers to retrieve arbitrary files from the filesystem

The vulnerabilities, tracked as CVE-2024-28075 and CVE-2024-23473, were discovered by ZDI vulnerability researcher Piotr Bazydło

Industrial Espionage: The most alarming scenario is a targeted attack designed to steal sensitive data (credentials, design plans, etc.)
SolarWinds has disclosed and patched a serious remote code execution (CVE-2024-0692) vulnerability in its Security Event Manager solution
CVE-2024-23476, CVE-2024-23477, and CVE-2024-23479, these flaws represent a grave risk to the integrity & security of enterprise systems