 Do Son
BRONZE SANDCASTLE uses Sandboxie DLL sideloading to run a modified Meterpreter backdoor in memory against targets in Asia and Africa.
Sophos
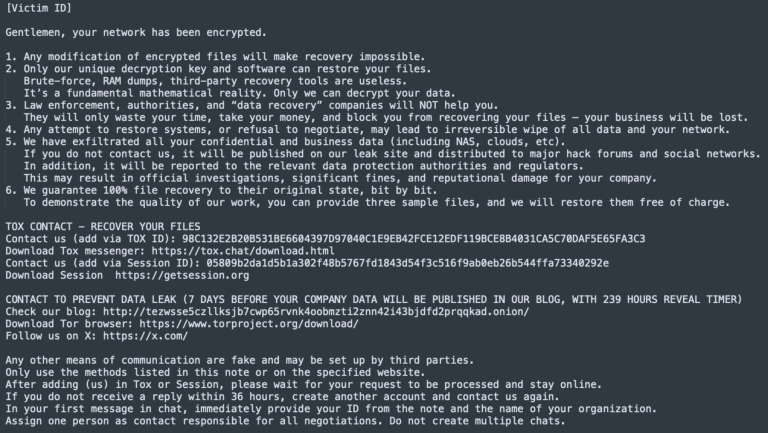
The Gentlemen ransomware, run by GOLD SHERWOOD, encrypts networks in under 24 hours. See the affiliate playbook and how to defend against it.

Interlock ransomware abused the legitimate Volatility3 tool to dump credentials from memory, Sophos found. Learn the attack chain and defenses.

North Korean group NICKEL ALLEY targets tech pros with "Contagious Interview" scams. Using fake job tests and RATs, they steal crypto and corporate access.

Sophos uncovers Keenadu, a persistent Android firmware backdoor embedded in core libraries that gives attackers total control via the Zygote process.

Black Basta ransomware now embeds a vulnerable NsecSoft driver (BYOVD) to silently kill antivirus processes like Sophos & CrowdStrike.

The Shanya Crypter (VX Crypt) is a new PaaS used by Akira/Medusa to bypass EDR. It deploys a kernel driver attack to kill security products and uses PEB manipulation for stealth.

Sophos uncovers GOLD SALEM, a new ransomware group exploiting SharePoint flaws. The group uses EDR evasion and legitimate tools to attack global targets.

Sophos has patched a critical authentication bypass flaw (CVE-2025-10159) with a CVSS 9.8 score in its AP6 wireless access points. Admins are urged to update now.

Sophos uncovers a new infection chain for GOLD BLADE's RedLoader malware, combining LNK files, WebDAV, and DLL sideloading to bypass defenses and deploy payloads stealthily.

Beware! Cybercriminals are using fake CAPTCHA pages to trick you into running commands that install the dangerous Lumma Stealer malware.

Learn about the indictment against Guan Tianfeng and the sophisticated hacking operation that exploited CVE 2020-12271.