 Do Son
Pega patched a SAML authentication bypass in Pega Platform, rated Critical 9.5 and High 7.0. No CVE, no known compromise. See affected versions and fixes.
SSO
A Dropbox Lenovo ID SSO flaw let attackers take over accounts with just an email address, no password needed. Dropbox has revoked sessions and hardened login.
CERT/CC discloses six Logto vulnerabilities, including CVE-2026-15611 and CVE-2026-15616, that enable SSO authentication bypass and MFA skipping.
CVE-2026-53513 is a Better Auth SSRF flaw (CVSS 9.6) in the SSO plugin. It exposes cloud metadata and enables account takeover. Patch to 1.6.11 now.

A critical OpenAM WebAuthn RCE flaw (CVE-2026-45051) allows code execution via Java deserialization. Update OpenAM to 16.1.1 to stay protected.

A critical ManageEngine account takeover vulnerability (CVE-2026-11374) exposes AD360 integrated deployments to unauthenticated attacks. Update systems now.
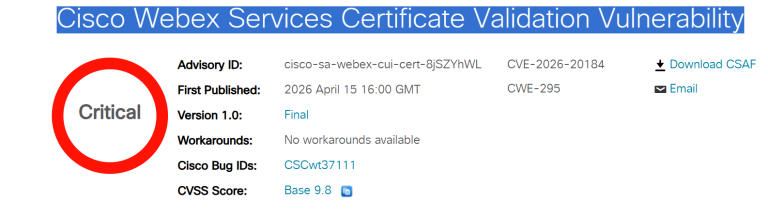
Cisco Webex CVE-2026-20184 allows unauthenticated user impersonation via SSO flaw. Fix requires a manual certificate update in Control Hub. Act now!
Critical Flaw in Wix’s New AI Platform Base44 Allowed Unauthorized Access to Private Enterprise Apps

Critical Flaw in Wix’s New AI Platform Base44 Allowed Unauthorized Access to Private Enterprise Apps
Wiz Research uncovered a critical flaw in Wix's new AI platform, Base44, that allowed unauthorized access to private enterprise applications and sensitive data by bypassing SSO.

A critical vulnerability (CVE-2025-54419, CVSS 10.0) in Node-SAML allows attackers to bypass SAML 2.0 authentication by manipulating unsigned assertion data.

A critical flaw (CVE-2025-54369) in Node-SAML allows attackers to bypass SAML 2.0 authentication by manipulating unsigned assertion data. Update to v5.1.0 immediately!

Critical vulnerability (CVSS 9.9) in samlify! This flaw puts many SSO implementations at risk, affecting a library with 768,000+ monthly downloads.