 Do Son
A China-linked operator ran an AI-driven hacking campaign from one server, hitting ministries in Vietnam, Taiwan, Indonesia, and India.
Taiwan

Symantec found Daxin malware active in Taiwan in May 2026, alongside a new Stupig backdoor that runs commands from the Windows logon screen.

Google exposed APT24's stealth BADAUDIO C++ downloader. The three-year campaign includes a supply chain hack hitting 1,000+ domains, using control flow flattening and AES-encrypted cookies for C2.
A new report from Cisco Talos details UAT-7237, a Chinese-speaking APT group targeting Taiwan's web infrastructure with customized open-source tools.

Proofpoint reveals a surge in China-aligned cyber espionage targeting Taiwan's semiconductor industry with spearphishing, Cobalt Strike, and new malware like Voldemort.

Taiwan's National Security Bureau warns against Chinese apps like TikTok, WeChat, and Rednote, citing excessive data collection and transfer to China as national security risks.

Taiwan's BitoPro exchange confirms North Korea's Lazarus Group stole $11.5M in crypto via phishing an employee and bypassing MFA on AWS infrastructure.

Silver Fox APT is conducting a multi-stage espionage campaign, leveraging backdoored medical software like Philips DICOM viewers to infect healthcare organizations
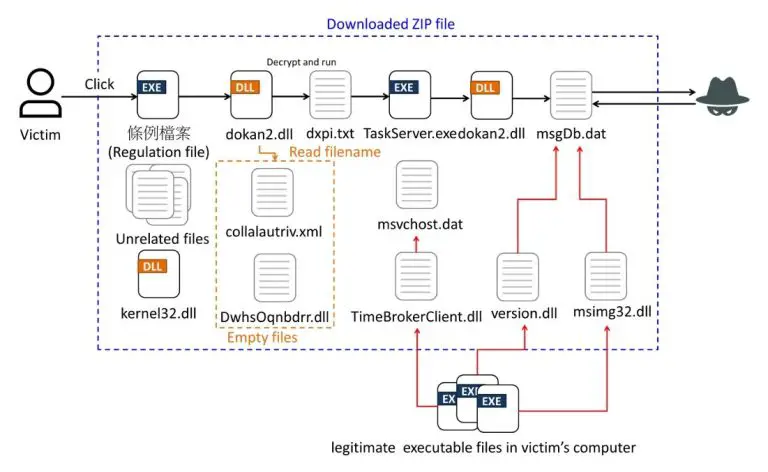
A sophisticated malware campaign is targeting Taiwan, impersonating the National Taxation Bureau to distribute Winos 4.0, HoldingHands RAT, and Gh0stCringe.

APT41 is leveraging Google Calendar as a covert C2 channel in a new multi-stage malware campaign targeting a Taiwanese government website.

Earth Ammit’s VENOM and TIDRONE campaigns target Taiwan and South Korea’s drone, military, and satellite sectors via stealthy supply chain attacks.

Swan Vector cyber-espionage campaign uses sophisticated malware to target institutions in Japan and Taiwan. Learn how they evade detection and steal data
Earth Kasha targets Taiwan and Japan in a March 2025 spear-phishing campaign using ANEL and NOOPDOOR backdoors for stealthy cyber espionage.

CrazyHunter ransomware group targets Taiwan's critical infrastructure with sophisticated attacks, using BYOVD techniques and open-source tools.