 Do Son
APT42 TAMECAT malware now blends AI-assisted phishing with cloud C2 to steal credentials from defense and nuclear-sector targets.
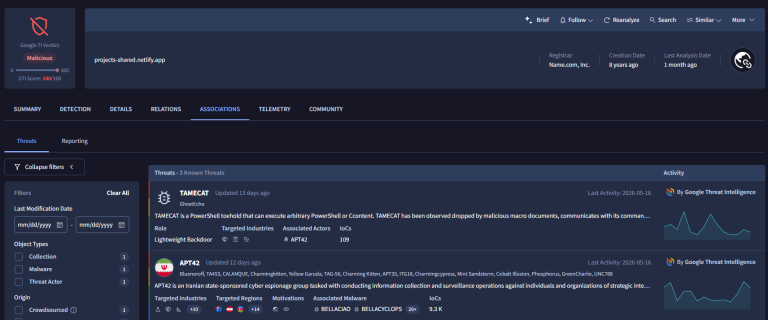
TAMECAT

APT42 targets defense officials with "TAMECAT," a modular PowerShell backdoor. The malware uses social engineering and Telegram C2 to steal secrets.

Israel disclosed SpearSpecter: an IRGC-IO espionage campaign using weeks-long WhatsApp social engineering and search-ms/WebDAV abuse to deploy the fileless TAMECAT PowerShell backdoor with Discord/Telegram C2.

APT42 operations are using two custom backdoors: NICECURL and TAMECAT. These backdoors are delivered via spear phishing