 Do Son
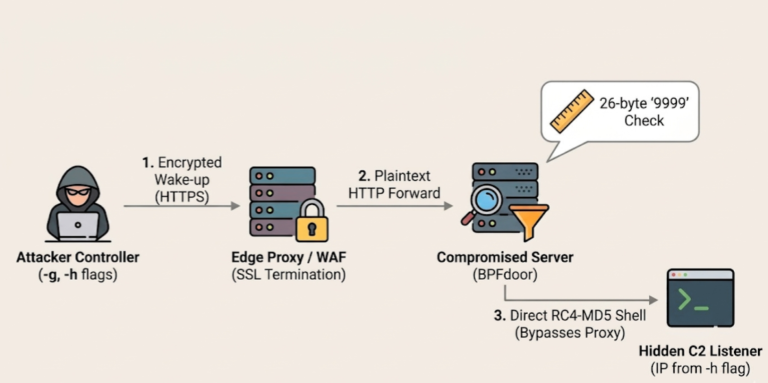
A new BPFDoor backdoor variant and the AVERAT implant hide on telecom edge devices by posing as mail traffic. See how they work and how to hunt them.
telecom

Nokia has issued a security advisory for two high-severity flaws (RCE and authentication bypass) in its CBIS and NCS platforms. Immediate patching is urged.

Palo Alto's Unit 42 reveals a sophisticated cyberespionage campaign by Liminal Panda (CL-STA-0969) targeting Southwest Asian telecom infrastructure with custom backdoors.

T-Mobile has acquired UScellular for $4.3B, but only after reportedly agreeing to end its DEI programs to secure FCC approval. The deal expands T-Mobile’s 5G network.

Nokia's WaveSuite NOC platform has two severe command injection vulnerabilities (CVE-2025-24938, CVE-2025-24936) allowing remote code execution, even with low privileges.

The FCC is reallocating part of the 6GHz Wi-Fi band to mobile carriers, shrinking Wi-Fi spectrum from 1200MHz to 500MHz. This threatens next-gen Wi-Fi speeds and innovation in the US.

Two unpatched CVSS 9.8 flaws in telecom gear enable remote code execution via buffer overflows, exposing critical infrastructure to attack.

A critical zero-day (CVE-2025-4428) in Ivanti EPMM is exploited by UNC5221, enabling unauthenticated RCE and data theft across multiple sectors.