 Do Son
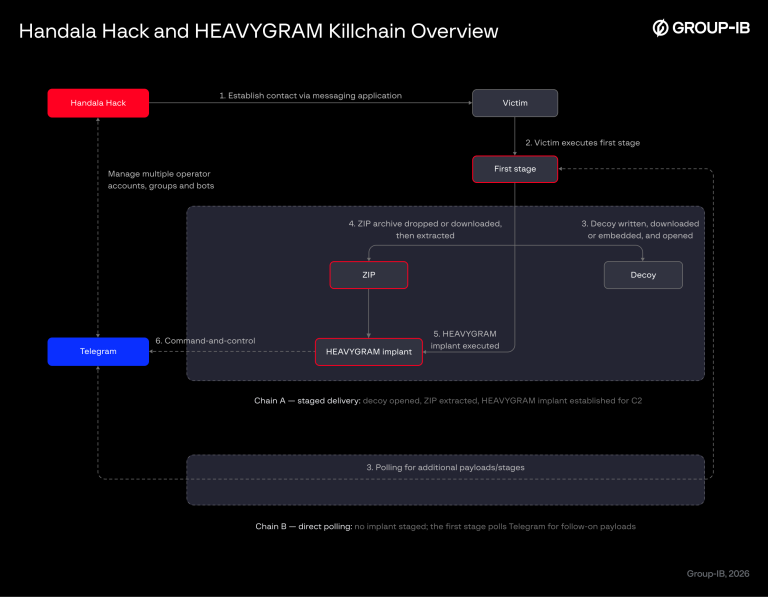
Group-IB uncovered Iranian HEAVYGRAM malware campaigns. The HEAVYGRAM malware abuses Telegram channels for command execution and data theft.
Telegram C2
Python NodeStealer now adds keylogging, clipboard, and screenshot spyware plus dual Telegram C2. See how the NodeStealer spyware upgrade works.
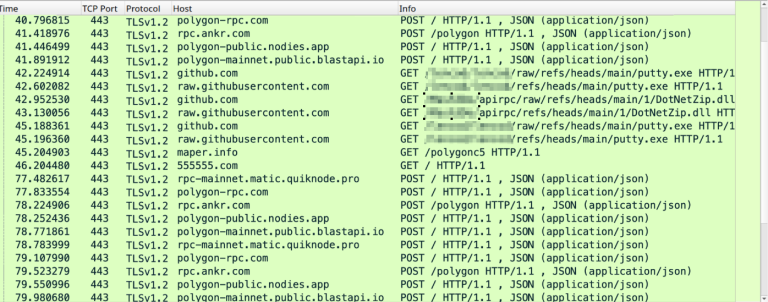
The Aeternum blockchain botnet hides C2 commands inside Polygon smart contracts, evading takedowns while dropping XWorm and XMRig payloads.

TELESHIM malware hits Middle East governments and abuses Telegram C2 to hide traffic. Zscaler ThreatLabz found the new backdoor and its tooling.

Starland RAT is new malware from Russian-speaking actor UAT-11795. It steals crypto wallets and credentials via fake Zoom and WebEx installers.
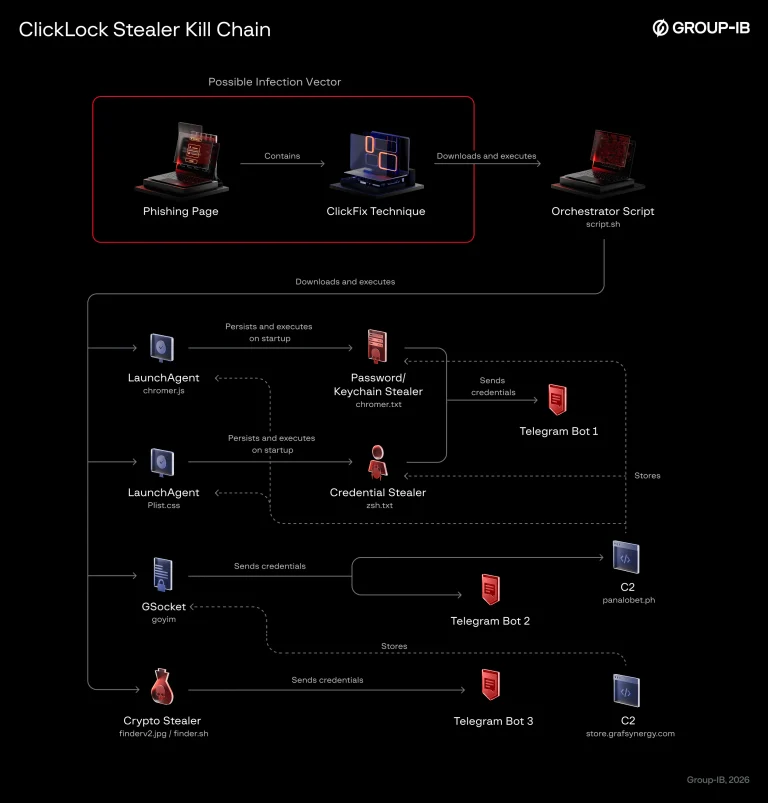
ClickLock Stealer is macOS malware that freezes your Mac until you type your password. Group-IB found 100+ victims across 33 countries.
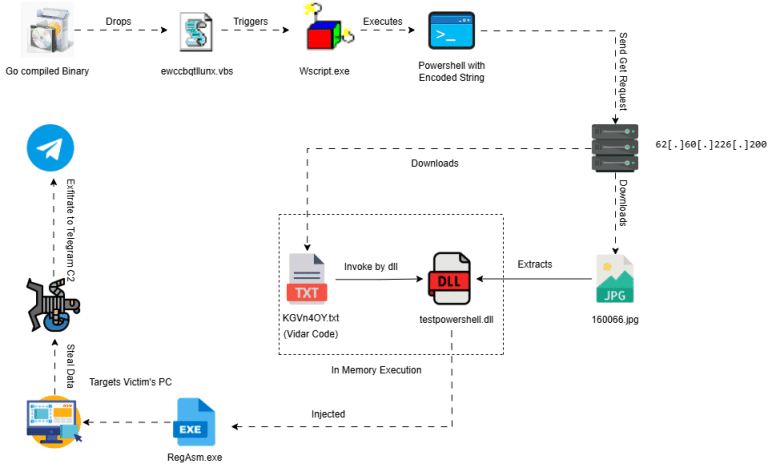
Vidar infostealer evolves into a fileless 2026 threat. From fake CAPTCHAs to "Claude Code" leaks, see how it steals crypto and passwords via Telegram C2.
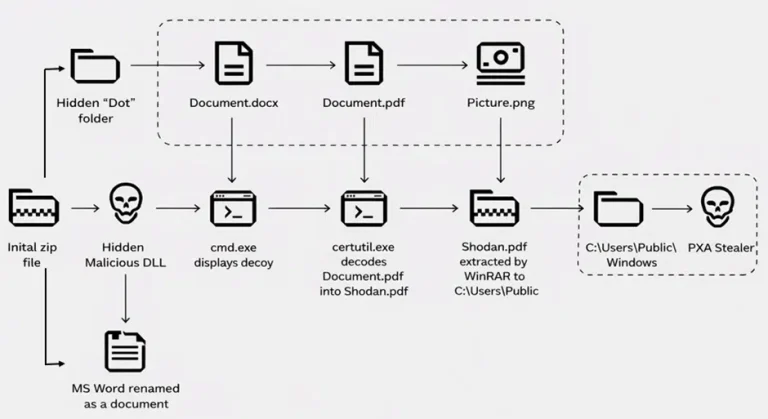
PXA Stealer activity surges in Q1 2026, targeting global finance. Learn how this Python-based malware uses Telegram and LOLBins to hijack crypto and banking data.
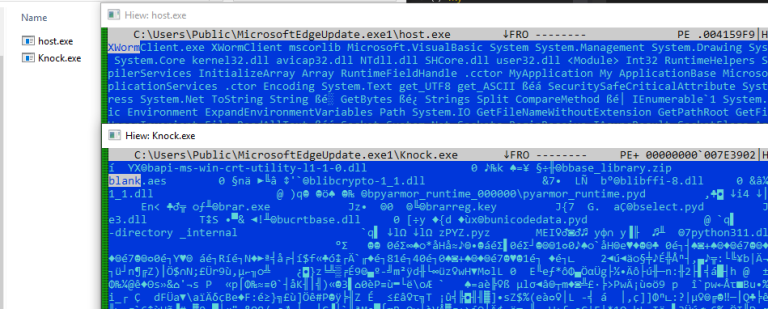
Splunk unmasks BlankGrabber: a modular Python info stealer using Discord and GitHub to swipe credentials and Discord tokens. Learn how to stay protected.
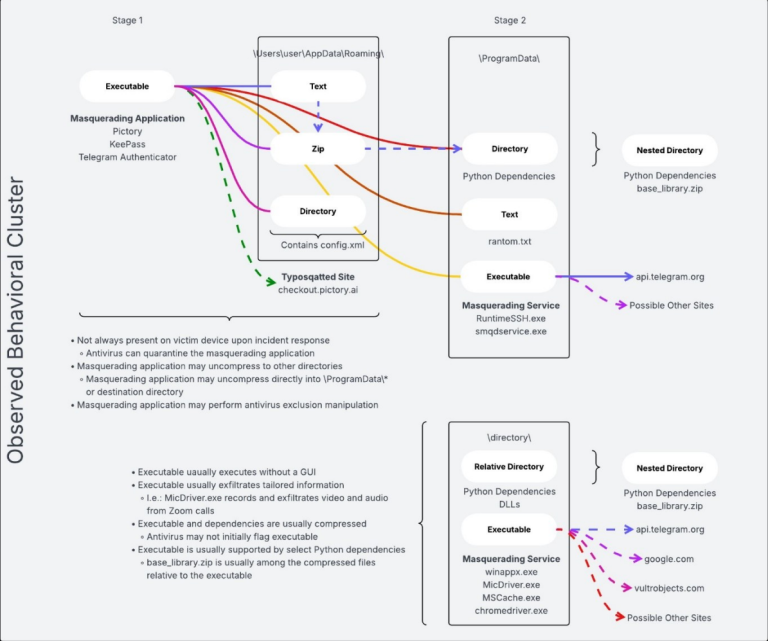
The FBI warns that Iran's MOIS is weaponizing Telegram as a Command-and-Control hub to deploy malware against global dissidents and journalists.
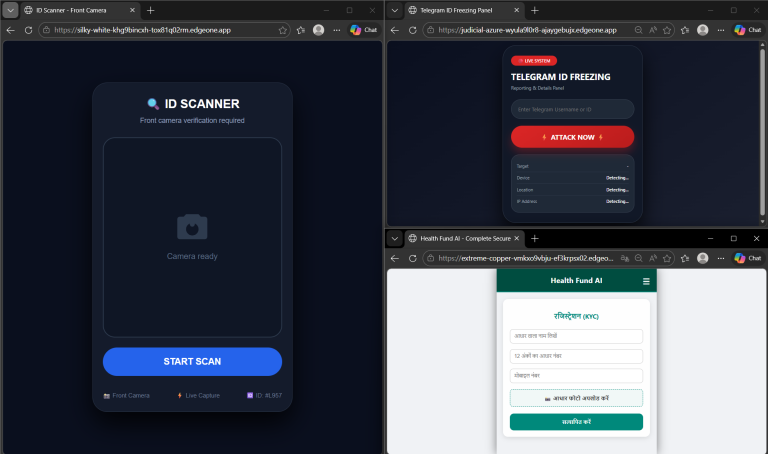
Cyble exposes a phishing campaign abusing browser permissions to silently steal biometric data, audio, and locations for deepfakes and identity fraud.

Group-IB exposes Operation Olalampo: MuddyWater's new MENA campaign using AI-assisted Rust malware (CHAR) and Telegram bots for stealthy C2 communication.

APT42 targets defense officials with "TAMECAT," a modular PowerShell backdoor. The malware uses social engineering and Telegram C2 to steal secrets.

"RedKitten" spies on Iranian protesters using AI-written malware. Attackers use fake death lists to deploy SloppyMIO surveillance tools.
SafeBreach reveals the return of the Prince of Persia (Infy) group, using Telegram and the new Tonnerre v50 malware to target victims in 2025.

CyberArmor exposed Autumn Dragon, a China-nexus APT using a WinRAR path traversal flaw (CVE-2025-8088) and DLL sideloading to deploy a Telegram C2 backdoor for espionage in Southeast Asia.

Group-IB exposed an automated PhaaS kit that impersonates Aruba S.p.A. to steal credentials, credit card details, and OTPs. The multi-stage scam uses a CAPTCHA filter and Telegram for real-time exfiltration.

CRIL exposed fileless phishing using malicious HTML attachments. Credentials are stolen via a fake Adobe login and instantly exfiltrated to Telegram bots, bypassing traditional domain filters.
Tap-and-Steal: Over 760 Android Apps Exploit NFC/HCE for Payment Card Theft in Global Financial Scam

Tap-and-Steal: Over 760 Android Apps Exploit NFC/HCE for Payment Card Theft in Global Financial Scam
Zimperium found 760+ Android apps exploiting NFC/HCE to steal payment data. The malware impersonates 20 banks across Russia, Poland, and Brazil, using Telegram for criminal coordination.

Netskope exposed a Python RAT (Nursultan Client) disguised as a Minecraft tool. It uses the Telegram Bot API for C2 to steal Discord tokens, credentials, and capture screenshots on Windows, Linux, and macOS.

A sophisticated GhostBat RAT campaign targets Indian users by spoofing RTO apps (mParivahan). The malware steals UPI credentials and OTPs via phishing pages and uses a Telegram bot for C2.

FortiGuard Labs identified a new Stealit malware variant abusing Node.js SEA for stealthy distribution. The campaign features a public C2 panel and uses Telegram for data exfiltration.