
 Do Son
An AI-powered botnet was migrated in six minutes by a solo actor using Gemini CLI. TrendAI Research analyzed 200 session logs from "bandcampro".
Trend Micro
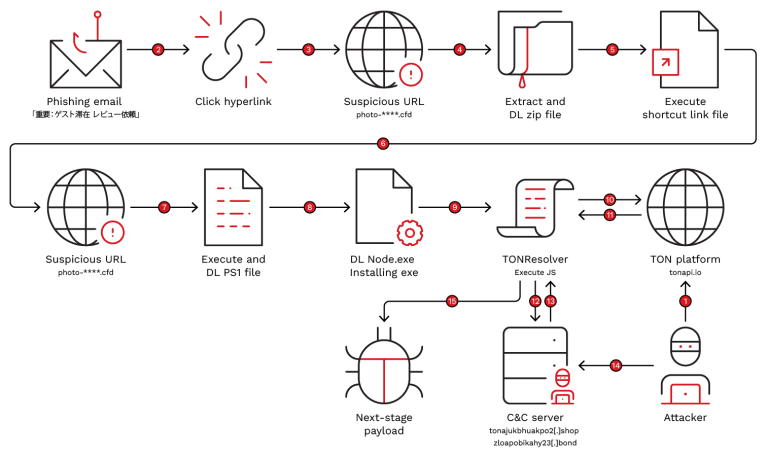
Trend Micro found TONResolver malware hitting Booking.com hotel partners in Japan. It hides its C2 in a TON blockchain smart contract. Details inside.

Trend Micro uncovers QLNX, a fileless Linux RAT targeting AWS, NPM, and Kubernetes keys. Learn how its eBPF rootkit hides from even the deepest system scans.

Trend Micro uncovers a phishing campaign abusing Kuse.ai and VEC to steal credentials via markdown notes. Don't trust a domain just because of its reputation.

Pawn Storm (APT28) debuts the PRISMEX suite, weaponizing Office zero-days against NATO logistics. Discover the stealth tactics behind this 2026 offensive.

Trend Micro uncovers a selective PureLog Stealer campaign using fake legal notices and fileless execution to target healthcare and government sectors.
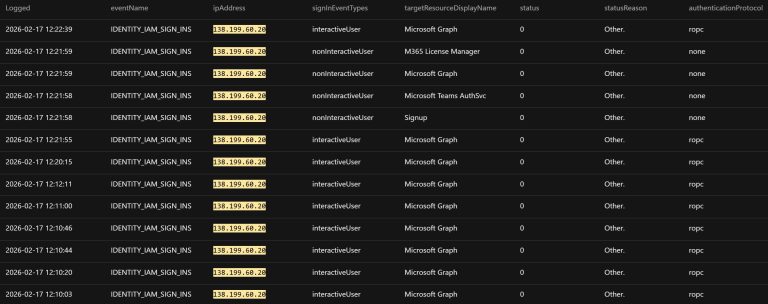
Trend Micro reveals how an exposed Spring Boot Actuator and a spreadsheet of plaintext secrets led to a malware-less SharePoint data exfiltration attack.

Trend Micro reveals Warlock ransomware is using kernel-level BYOVD attacks and abused IT tools to bypass security and hijack Active Directory.

Trend Micro exposes KongTuke's new "CrashFix" tactic, which tricks enterprise users via fake Chrome errors into deploying the fileless modeloRAT backdoor.

Trend Micro reveals the BoryptGrab info stealer campaign using SEO-optimized fake GitHub repos to deploy the TunnesshClient reverse SSH backdoor.

Hackers abuse Atlassian Jira notifications to bypass spam filters. Trend Micro warns of scams targeting enterprise users via trusted alerts.

Trend Micro uncovers PeckBirdy, a JScript C&C framework used by China-aligned APTs. It uses lightweight, fileless tactics to target Asian governments.
Trend Micro reveals Evelyn Stealer, a malware campaign weaponizing Visual Studio Code extensions. It uses DLL injection to steal developer secrets & crypto.

New AsyncRAT campaign abuses free Cloudflare tunnels for stealthy malware delivery. Learn how phishing emails lead to WebDAV attacks & Python injection.

SHADOW-VOID-042 impersonated Trend Micro via fake security advisories to breach defense, energy, and chemical firms. Tactics align with Void Rabisu (ROMCOM), using HR lures and targeted exploits.
Water Saci Campaign Uses LLMs to Convert Malware to Python, Spreads Banking Trojan Via WhatsApp Worm

Water Saci Campaign Uses LLMs to Convert Malware to Python, Spreads Banking Trojan Via WhatsApp Worm
Trend Micro exposed Water Saci, a campaign using LLMs to convert malware from PowerShell to Python, accelerating its spread via a WhatsApp worm. The multi-stage attack deploys a trojan capable of VNC mirroring and overlay attacks.

Despite a recent doxxing attempt, Lumma Stealer has resurfaced, integrating browser fingerprinting into its C&C to collect WebGL/Canvas signatures for sandbox evasion and victim assessment.

Trend Micro discovered that Axis Communications leaked hardcoded Azure SAS tokens in a signed DLL for its Autodesk Revit plugin, exposing three cloud storage accounts to unauthorized access.

Trend Micro discovered RondoDox, a new botnet leveraging 50+ exploits (including the Pwn2Own TP-Link flaw) in an "exploit shotgun" approach to compromise routers, DVRs, and IoT globally.

Trend Micro uncovered "Water Saci," a self-propagating malware (SORVEPOTEL) that hijacks WhatsApp Web sessions to spread aggressively and steal Brazilian banking credentials.

Trend Micro reveals a new global malware campaign, EvilAI, that impersonates productivity and AI tools to infiltrate organizations and steal data.

A new report reveals the AMOS infostealer is targeting macOS. The malware is spread via fake apps and malicious Terminal commands that bypass Gatekeeper.