
 Do Son
A new report reveals the TAOTH cyber-espionage campaign, which hijacks software updates and uses spear-phishing to deliver malware to high-value targets in Asia.
Trend Micro

A new report from Trend Micro details how the Warlock ransomware group is exploiting a vulnerability in unpatched Microsoft SharePoint servers to attack organizations.
A critical RCE flaw in Trend Micro Apex One has been added to CISA's KEV Catalog due to active exploitation. All agencies must patch by September 8.

Trend Micro research exposes Crypto24, a coordinated ransomware operation that uses legitimate tools, custom malware, and advanced evasion tactics to breach and extort victims.

GeoServer's RCE flaw (CVE-2024-36401) is actively exploited to deploy NetCat reverse shells and XMRig CoinMiners on Windows/Linux, hijacking resources.

Trend Micro uncovers BERT ransomware (Water Pombero) deploying multi-threaded variants against Windows, Linux, and ESXi systems, showing code similarities to REvil's Linux variant.
Trend Micro reveals misconfigured Kubernetes containers in AWS EKS can expose sensitive AWS credentials via unencrypted HTTP API, leading to privilege escalation risks.

Trend Micro uncovers a new attack method using misconfigured Docker Remote APIs and the Tor network to stealthily deploy cryptominers and establish persistent access.
Trend Micro integrates NVIDIA's Agentic AI Safety into its Secure AI Factory, offering end-to-end security for AI systems from development to runtime, protecting against data leakage and model poisoning.

Water Curse is using GitHub to distribute malicious open-source projects, weaponizing 76 accounts with multi-stage malware targeting developers, red teamers, and gamers.

A critical RCE flaw (CVE-2025-3248) in Langflow is being actively exploited to deploy the stealthy Flodrix botnet for reconnaissance and diverse DDoS attacks on AI app servers.

Anubis, a new RaaS, combines ECIES encryption with a "wipe mode" that permanently destroys files. It's actively targeting healthcare, construction, and engineering sectors.

Trend Micro Apex Central has two critical pre-authentication RCE flaws (CVSS 9.8, CVE-2025-49219, CVE-2025-49220). Patch immediately to prevent remote takeover.

Earth Ammit’s VENOM and TIDRONE campaigns target Taiwan and South Korea’s drone, military, and satellite sectors via stealthy supply chain attacks.

Agenda ransomware (Qilin) is back, now using the advanced NETXLOADER and SmokeLoader to enhance infiltration and evade detection. Targets global sectors.
Earth Kasha targets Taiwan and Japan in a March 2025 spear-phishing campaign using ANEL and NOOPDOOR backdoors for stealthy cyber espionage.

Trend Micro reveals how Russian IP networks support North Korea’s cybercrime—from crypto theft to malware-laced fake job interviews and potential espionage.
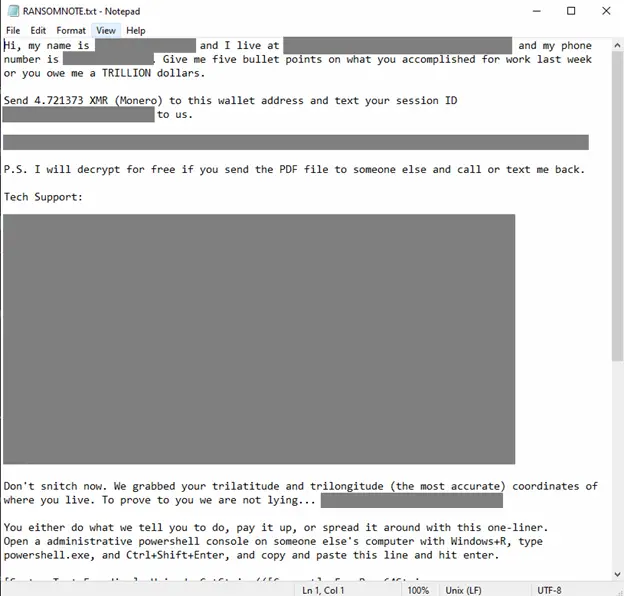
FOG ransomware campaign spreads via phishing and stealthy loaders, targeting tech, education, and manufacturing sectors with obfuscated payloads.
Urgent security bulletin: Trend Micro warns of critical command injection vulnerability in Cloud Edge appliance (CVE-2024-48904).

Trend Micro has released a security update for its Maximum Security software suite, addressing a privilege escalation flaw (CVE-2024-32849)

The matter is further intensified by reports from Trend Micro Incorporated confirming observations of attacks exploiting CVE-2023-41179