 Do Son
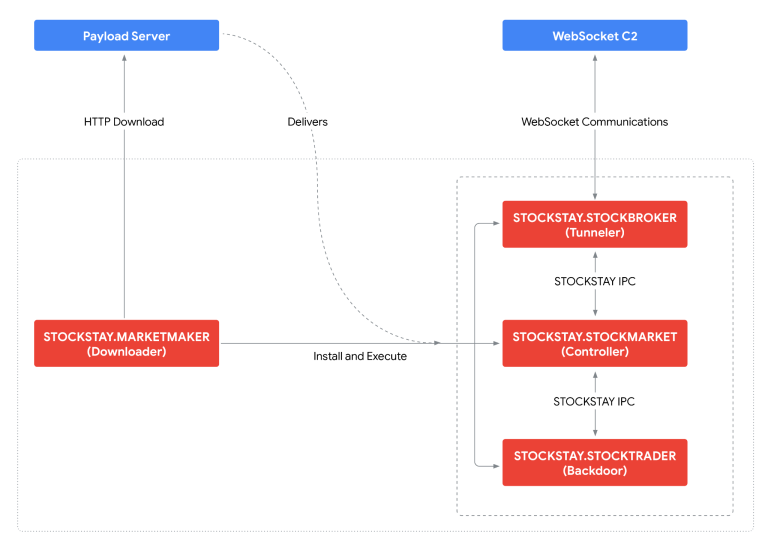
Turla STOCKSTAY backdoor attacks Ukrainian military targets. Russian cyber espionage groups deploy this .NET malware via malicious RDP and WinRAR flaws.
turla

Microsoft Threat Intelligence exposes a massive overhaul of the Kazuar backdoor. Secret Blizzard weaponizes a modular, multi-tiered P2P botnet.

Critical WinRAR flaw CVE-2025-8088 is exploited by spies & cybercriminals. "Zeroplayer" sells the exploit. Update to v7.13 to stop Startup folder attacks.

Microsoft reveals Russian state actor Secret Blizzard is targeting foreign embassies in Moscow with ISP-level AiTM attacks, deploying ApolloShadow malware to spy on diplomats.

Uncovering the tactics of Secret Blizzard: Learn how this threat actor co-opts tools from cybercriminals to target Ukraine.

Uncover the cyberespionage campaigns of GoldenJackal, an elusive APT group targeting governmental entities across Europe, the Middle East, and South Asia.

Uncover the evolving cyberwarfare tactics of Russian state-backed hackers. Find out how they exploit mobile devices for espionage and data theft.

CRIL identified a sophisticated campaign employing a tiny, stealthy backdoor, now suspected to be the work of the infamous Turla APT group

2023 witnessed a significant shift in the tactics and approaches of cyber attackers, influenced by global conflicts and advancements in technology

The ESET security team found that a state-funded Russian cyber espionage organization, Turla has added a new “weapon” to...