 Do Son
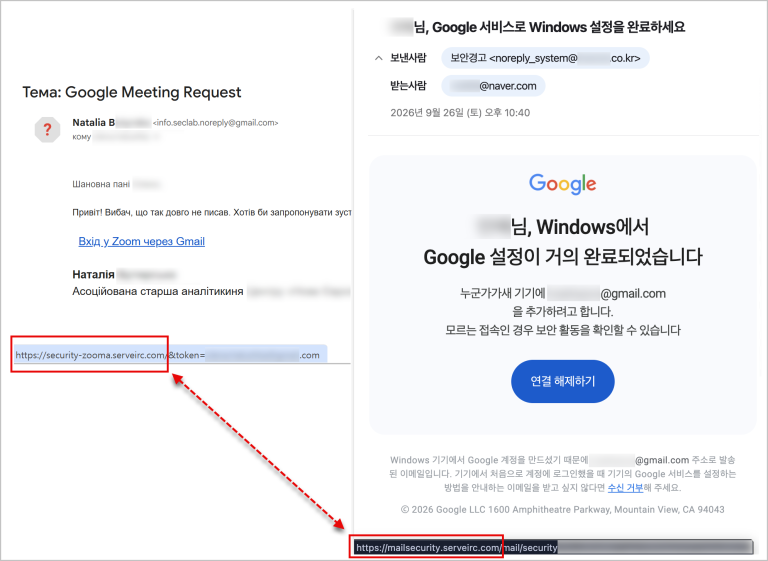
Kimsuky spear phishing lures target Ukrainian security experts with fake invitations, as Operation GitPower abuses GitHub and GitLab.
Ukraine
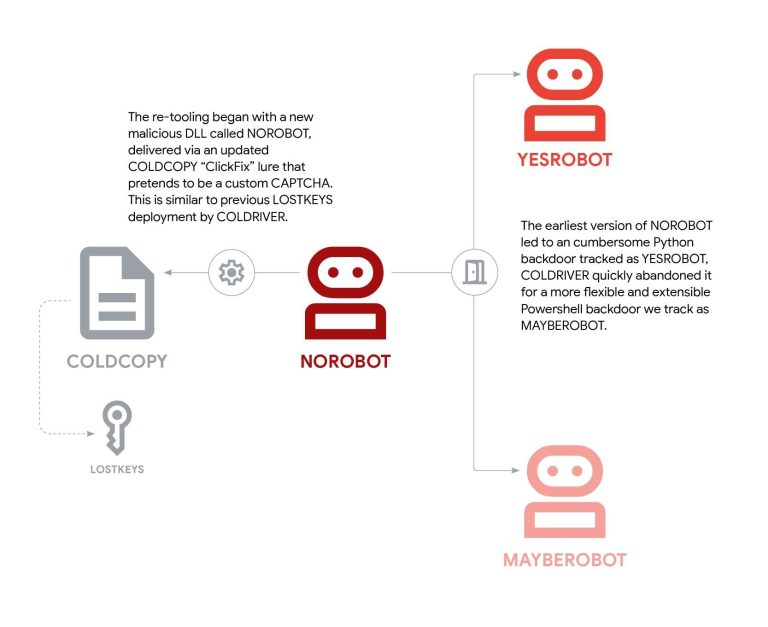
Star Blizzard RedFlick phishing hit 100+ groups that back Ukraine, using scheduled tasks to drop the CosmicPulse backdoor after a single click.
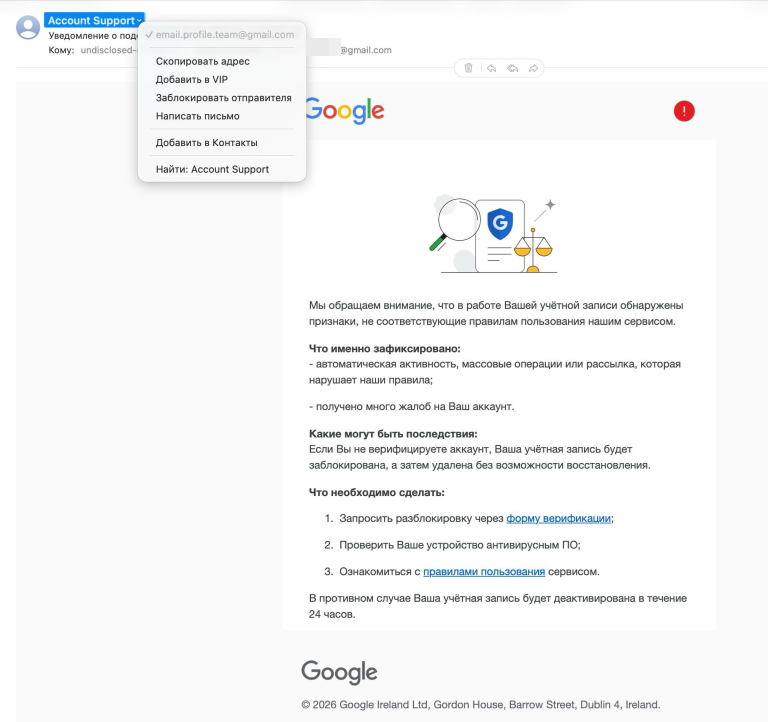
A suspected UNC1151 phishing campaign targets Belarusian politicians and Ukrainian portals to steal credentials using deceptive login pages.

A patched WinRAR vulnerability in Ukraine is still exploited via CVE-2025-8088 to deploy GIFTEDCROOK and espionage tools, says Trend Micro.

Pawn Storm (APT28) debuts the PRISMEX suite, weaponizing Office zero-days against NATO logistics. Discover the stealth tactics behind this 2026 offensive.

BlueDelta (APT28) is targeting UKR.NET users with a sophisticated phishing campaign using ngrok and Mocky to bypass security and steal 2FA codes.

Arctic Wolf Labs reveals Russian GRU Unit 29155 using SocGholish to deploy RomCom malware against a US firm with ties to Ukraine.

Symantec exposed a Russian-aligned espionage campaign in Ukraine using LotL tactics. Attackers used a Sandworm-linked webshell (Localolive) and abused scheduled tasks to dump credentials and bypass Windows Defender.
SentinelLABS exposed PhantomCaptcha, a ClickFix campaign targeting Ukraine NGOs. It uses a fake Cloudflare CAPTCHA to deploy a multi-stage PowerShell WebSocket RAT and a parallel Android spyware attack.

A new report reveals a network of Ukrainian and offshore hosting providers are fueling large-scale brute-force and password-spraying campaigns to enable global ransomware attacks.

A new report from HarfangLab details two recent UAC-0057 (Ghostwriter) campaigns targeting Ukraine and Poland with malicious archives and multi-stage implants.

CERT-UA uncovers a new UAC-0099 campaign targeting Ukraine's defense sector. The group uses a toolkit of MATCHBOIL, MATCHWOK, and DRAGSTARE malware for reconnaissance and data exfiltration.

IBM X-Force warns that Russian-aligned Hive0156 is intensifying spear-phishing campaigns against Ukrainian government and military, delivering Remcos RAT via LNK/PowerShell files.

The suspected administrator of xss.is, a notorious Russian-speaking cybercrime forum, has been arrested in Ukraine after a joint operation by French police and Europol.

Socket researchers uncovered widespread "protestware" in 28+ npm packages, silently disabling mouse interactions and playing the Ukrainian anthem for Russian-language users.

FortiGuard Labs exposes NordDragonScan, a new infostealer using weaponized HTA scripts in Ukrainian-themed phishing. It performs recon, steals browser profiles, and exfiltrates documents.

Pro-Russian hacktivists intensify 2025 digital assaults on Ukraine, NATO, and Western critical infrastructure, using DDoS, defacements, and targeting ICS.

Arctic Wolf Labs reveals UAC-0226 is using evolving GIFTEDCROOK malware in cyber-espionage against Ukrainian military and government, exfiltrating sensitive documents

Cisco Talos reveals "PathWiper," a new destructive malware used in a highly confident Russia-nexus APT attack against Ukrainian critical infrastructure.

Microsoft identified Void Blizzard, a new Russia-affiliated cyberespionage group, targeting critical sectors in NATO countries and Ukraine.

A joint advisory warns that Russia's APT28 (Fancy Bear) is actively targeting logistics and tech companies supporting Ukraine with espionage and data exfiltration.

Russia-linked APT28 (Sednit/Fancy Bear) targets vulnerable webmail with XSS in Operation RoundPress, stealing data from global entities.