 Do Son
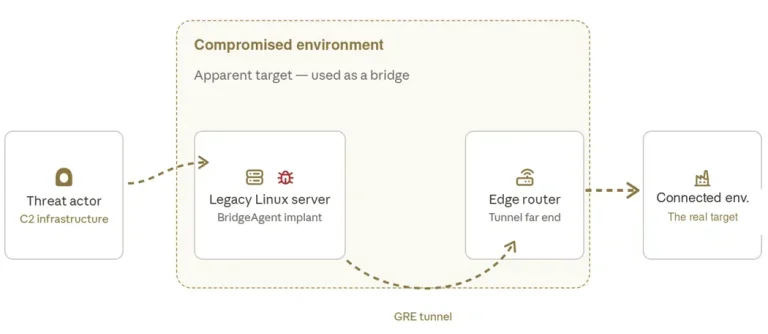
The Fire Ant threat actor uses trusted infrastructure compromise to breach high-value targets. Discover how this group evades detection in networks.
UNC3886
New research by Intezer reveals the OrBit Linux rootkit is actually a fork of the open-source Medusa kit, actively weaponized across multiple APTs.

Sygnia uncovers "Fire Ant," a sophisticated cyber-espionage campaign exploiting VMware ESXi and vCenter since early 2025, using advanced techniques to evade detection and maintain persistent access.

OT-ISAC warns that China-linked APT group UNC3886 is actively targeting Singapore's critical infrastructure, exploiting zero-day vulnerabilities for stealthy, long-term access.

Learn about CVE-2025-21590, an actively exploited vulnerability in Junos OS that allows local code execution for attackers.