
 Do Son
Silver Fox fake software installers impersonate Razer and Edge to disable Windows Defender and deploy malware. See how the campaign works.
ValleyRAT
Kaspersky uncovered a ValleyRAT backdoor adware campaign using signed wallpaper apps to drop malware. Learn how to protect your systems.

Cato CTRL details a new SilverFox ValleyRAT campaign in Japan using three BYOVD drivers and DLL sideloading to kill security tools.

Silver Fox's Ghost distributor delivers MODBEACON, a modular Rust trojan, to picked targets in Operation Phnom Penh, per Qianxin. Here's what to know.
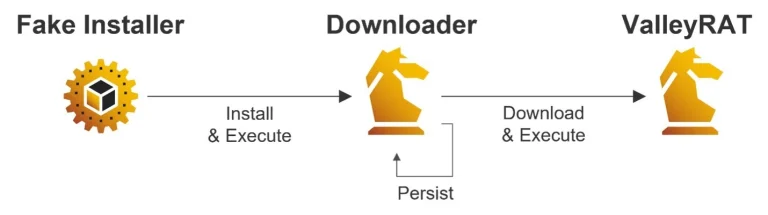
LevelBlue tracks a ValleyRAT malware email campaign using DLL sideloading and fileless execution to hit Japanese and Chinese users.
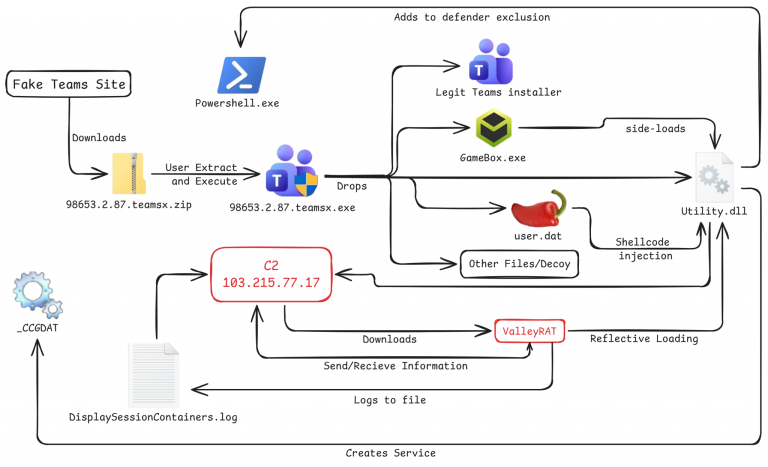
A sophisticated ValleyRAT malware campaign uses fake Microsoft Teams installers and DLL sideloading to evade Windows Defender detection.
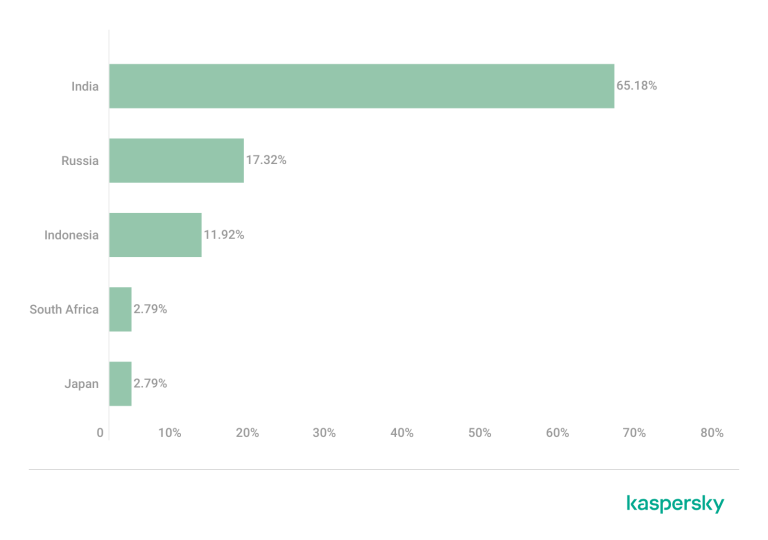
Silver Fox targets India and Russia with tax-themed phishing and the new ABCDoor backdoor. Learn how this Python-based threat hijacks screens and data.

Sekoia TDR reveals Silver Fox's latest tactics. From tax-themed phishing to WhatsApp clones, this China-based group combines espionage with financial theft.
FortiGuard Labs exposes a massive Silver Fox APT campaign targeting Taiwan. Hackers use tax-themed phishing and BYOVD attacks to deploy Winos 4.0 malware.

Silver Fox APT targets users with fake LINE installers delivering ValleyRat. New campaign uses rare "PoolParty" injection to evade detection.

A military-grade backdoor, ValleyRAT, saw an 85% surge after its builder was leaked. The kernel-mode rootkit bypasses Windows 11 defenses and is now a dangerous commodity for cybercriminals.

Chinese APT Silver Fox is using a Cyrillic false flag in an SEO poisoning campaign impersonating Microsoft Teams. The attack installs ValleyRAT for espionage and financial fraud.

A new ValleyRAT campaign targets English job seekers. The malware uses DLL sideloading via a trojanized Foxit PDF Reader executable to run a Remote Access Trojan and exfiltrate data.

Seqrite exposed Operation Silk Lure, a campaign using a malicious Chinese resume (.LNK) to implant ValleyRAT on FinTech systems. It achieves persistence via a “Security” scheduled task and uninstalls AV.

A new report reveals the Silver Fox APT group is abusing a Microsoft-signed vulnerable driver to disable endpoint security and deploy the ValleyRAT backdoor.

Silver Fox APT is conducting a multi-stage espionage campaign, leveraging backdoored medical software like Philips DICOM viewers to infect healthcare organizations

Discover the Healthcare Espionage Campaign by Silver Fox targeting Philips DICOM viewers with malware and keyloggers.

Unveiling the sophisticated Silver Fox APT: Learn how this multi-stage malware campaign deploys the resilient ValleyRAT.
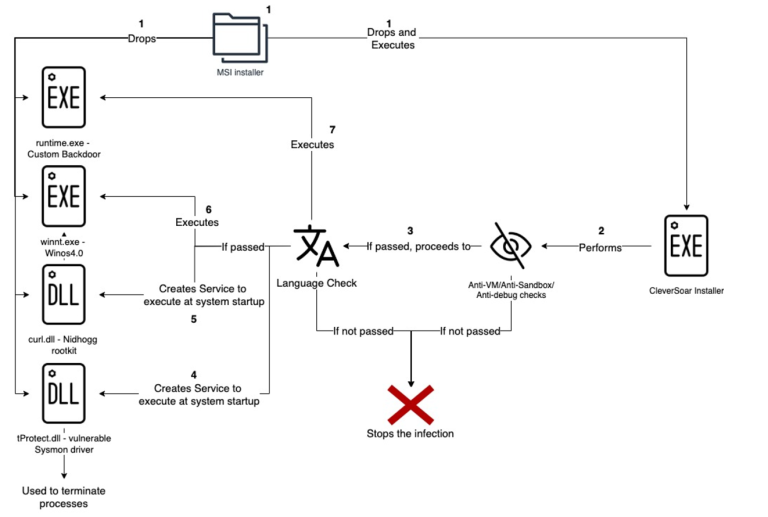
Discover the newly identified CleverSoar installer and its targeted espionage efforts. Explore the advanced evasion techniques and malicious components used in this sophisticated malware campaign.

Uncover the ValleyRAT malware campaign targeting Chinese-speaking users in e-commerce, finance, sales, and management sectors.