 Do Son
Cisco Talos uncovered the KeyDrift malware UAT-11473 campaign exploiting CVE-2026-20127 to steal IPsec keys from Cisco SD-WAN controllers.
Volt Typhoon
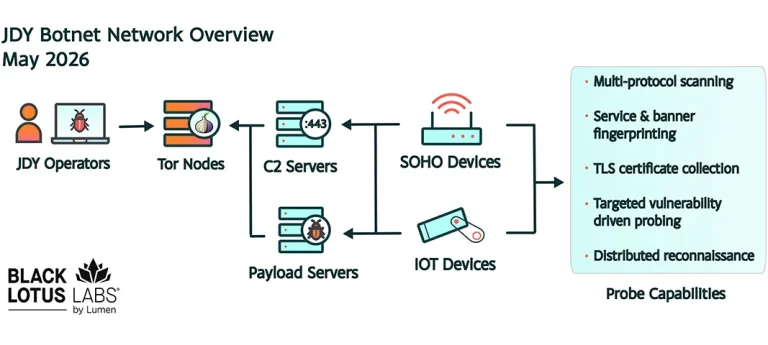
The JDY botnet, a China-nexus IoT network tied to Volt Typhoon, now spans 1,500+ devices and scans for new bugs like CVE-2026-35616 within hours.

Uncover the critical details about Volt Typhoon APT group: a state-sponsored threat targeting US critical infrastructure sectors.

Uncover the resurgence of the Volt Typhoon cyber-espionage group. Learn how this APT actor targets critical infrastructure by exploiting vulnerabilities in legacy network devices.

Uncover the sophisticated cyberattack campaign known as 'Pacific Rim.' Discover how China-based threat groups target high-value infrastructure and government organizations

The VersaMem web shell, uncovered by Black Lotus Labs, is a sophisticated tool specifically designed to exploit Versa Director servers

Industrial Espionage: The most alarming scenario is a targeted attack designed to steal sensitive data (credentials, design plans, etc.)

a trend in China-linked cyberattacks: a sustained focus on compromising Operational Technology environments within critical infrastructure

VOLTZITE, a threat group known for persistent targeting of global critical infrastructure sectors, continues to refine its methods

The KV-botnet operates in the shadows, infecting small-office, home-office (SOHO) routers and firewall devices worldwide.