 Do Son
An exploited Check Point VPN vulnerability allows remote code execution. Patch this Check Point VPN vulnerability now to block active in-the-wild attacks.
vpn
Check Point fixed critical Check Point VPN vulnerabilities. Update gateways to prevent remote code execution under CVE-2026-85102 and CVE-2026-85103.

Cisco patches CVE-2025-20362, a medium-high zero-day vulnerability in ASA/FTD VPN web servers that is being exploited to gain unauthorized access to restricted resources.

A critical vulnerability (CVE-2025-9242) in WatchGuard's Fireware OS could allow an unauthenticated remote attacker to execute arbitrary code.

Australian authorities issue an urgent alert on a critical SonicWall SSL VPN flaw actively exploited by Akira ransomware, urging immediate patching.

A new report reveals a network of Ukrainian and offshore hosting providers are fueling large-scale brute-force and password-spraying campaigns to enable global ransomware attacks.

Google is updating its terms to prohibit cross-region YouTube Premium subscriptions. Users using VPNs to get cheaper prices risk having their accounts canceled.

Huntress and other firms warn of a likely zero-day vulnerability in SonicWall VPNs. Attackers are bypassing MFA and deploying Akira ransomware within hours of initial access.

Microsoft and eSentire expose SilentRoute, a backdoored SonicWall SSL VPN NetExtender client distributed via SEO poisoning, stealing credentials and breaching networks.

Socket uncovers a sprawling network of malicious Firefox extensions, masquerading as games, VPNs, and tools, to hijack affiliate links, steal OAuth tokens, and reroute traffic.

SonicWall and Microsoft uncover a campaign distributing a trojanized NetExtender VPN client that steals credentials by bypassing certificate validation.
Cisco warns of a critical flaw (CVE-2025-20271, CVSS 8.6) in Meraki MX/Z Series devices, allowing unauthenticated remote DoS on AnyConnect VPN. Update firmware now!

A flaw (CVE-2025-4232) in GlobalProtect for macOS allows local users to escalate to root. Public PoC code exists. Update now!

Symantec reveals popular Chrome extensions like Browsec VPN & DualSafe Password Manager are leaking sensitive user data over unencrypted HTTP, risking privacy.
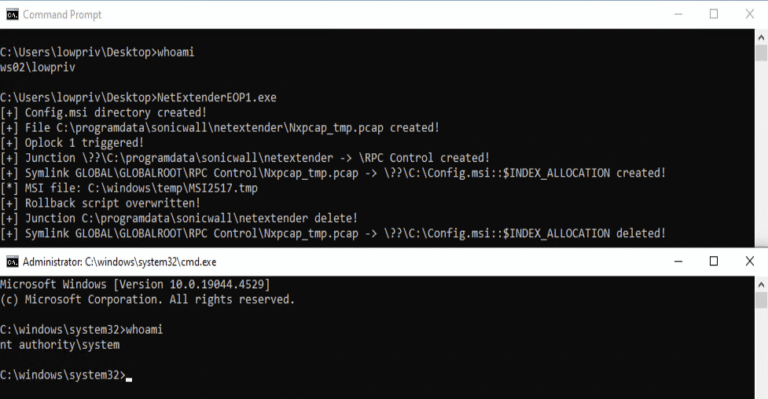
High-risk LPE vulnerabilities in SonicWall NetExtender for Windows (CVE-2025-23009, CVE-2025-23010) allow SYSTEM access or DoS. Patch immediately to version 10.3.2.

Lenze VPN Client for x500 IoT gateways has critical flaws allowing arbitrary code execution via local privilege escalation.

A China-nexus APT group exploited Ivanti Connect Secure VPN vulnerabilities to infiltrate organizations globally, deploying the SPAWNCHIMERA malware toolkit

Learn about Tor Browser, the Dark Web, and how to navigate it safely. This guide covers installation, configuration, security precautions, and the potential risks of exploring the dark web.

Rapid7 reveals details of Ivanti zero-day CVE-2025-22457, a critical stack-based buffer overflow actively exploited by a China-linked group. Learn about the vulnerability and available patches.

SonicWall has patched three vulnerabilities (CVE-2025-23008, CVE-2025-23009, CVE-2025-23010) in its NetExtender VPN client. Update to version 10.3.2 or later to prevent privilege escalation and unauthorized access.

Explore the top VPN vulnerabilities for 2025. Understand the risks from AI attacks and perimeter device exploitation.

Understand the implications of using an Xbox ban VPN to purchase games across regions and avoid account suspension risks.