 Do Son
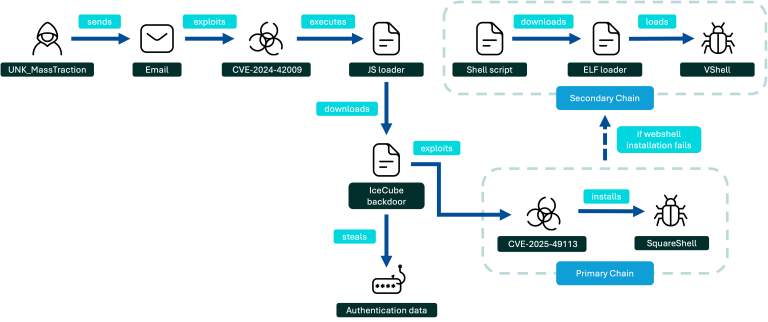
UNK_MassTraction, a suspected China-aligned actor, exploits Roundcube webmail flaws to steal credentials and deploy the VShell backdoor at universities.
VShell
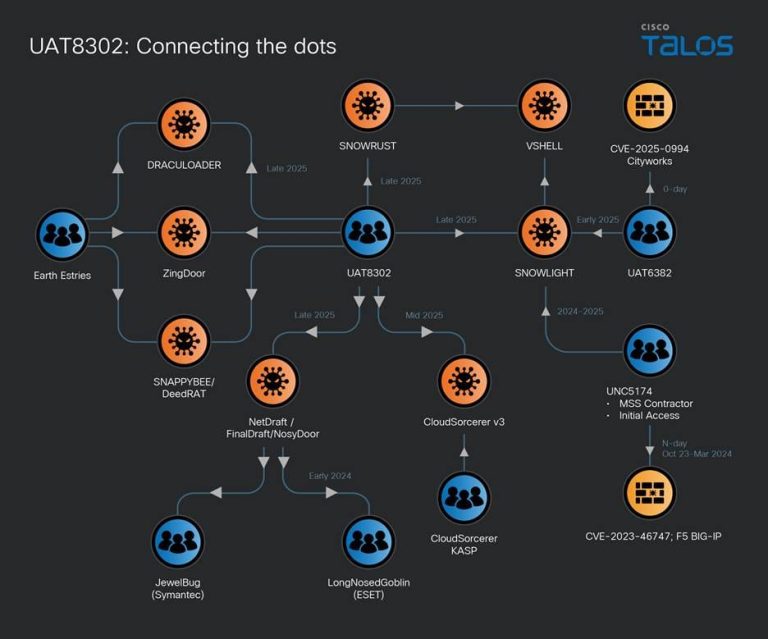
Cisco Talos exposes UAT-8302, a China-linked APT group infiltrating governments via NetDraft and CloudSorcerer. Learn how they share tools with notorious APTs.
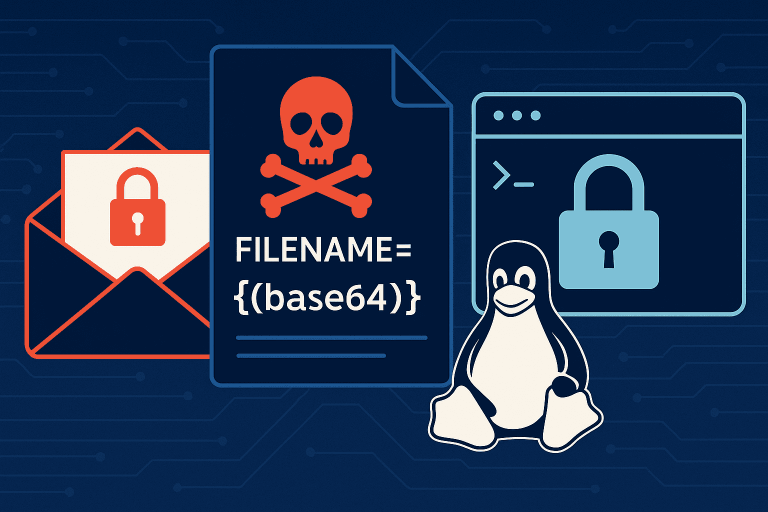
A new report reveals a dangerous Linux malware campaign that uses malicious filenames to execute a stealthy, fileless attack without the victim's knowledge.

JPCERT/CC details a sophisticated, ongoing malware campaign exploiting Ivanti Connect Secure (CVE-2025-0282, -22457) using MDifyLoader, Cobalt Strike, vshell, and Fscan for stealthy persistent access.

Seqrite Labs uncovers Operation DRAGONCLONE, a sophisticated APT campaign targeting China Mobile Tietong with VELETRIX and VShell malware.
A new campaign by Chinese threat actor UNC5174 uses the VShell RAT. Sysdig TRT reports on the group's shift to open-source tools and evasion tactics.