 Do Son
A major VoLTE security flaw leaves millions at risk. Learn how this Verizon IMS vulnerability allows undetected call hijacking and message spoofing.
Vulnerability Research
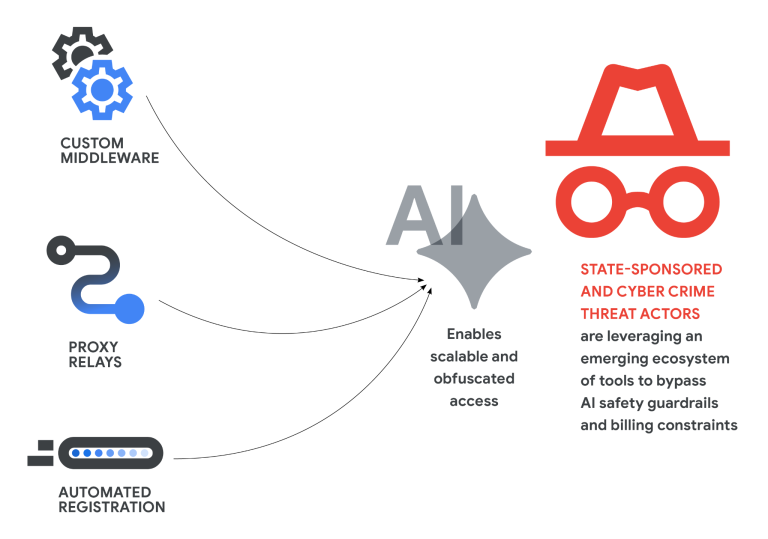
Google GTIG confirms the first AI-built zero-day exploit used in the wild. Discover how AI is industrializing cyber warfare and how Big Sleep is fighting back.
OpenAI unveils Project Daybreak, utilizing the GPT-5.5 lineage and Codex to automate vulnerability patching and Red Teaming in a direct challenge to Anthropic.
Apache MINA issues emergency patches for two 9.8 CVSS RCE flaws left behind by mistake. Unauthenticated attackers can bypass filters via deserialization.

Jenkins patches high-severity RCE in Credentials Binding and XSS in GitHub/HTML Publisher plugins. Secure your CI/CD pipeline by upgrading today.
Langflow patches a critical 9.6 CVSS path traversal vulnerability (CVE-2026-42048). Learn how an unsafe bulk delete function put entire filesystems at risk.
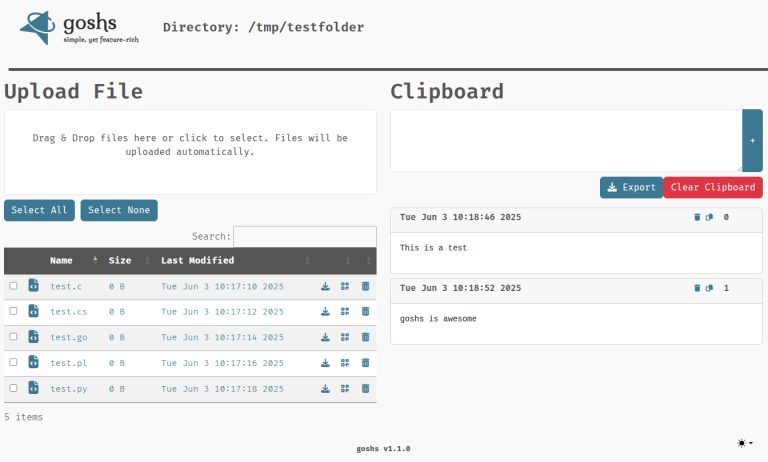
Critical 9.8 flaws in goshs v2.0.0-beta.2 allow unauthenticated attackers to write or delete any file on your system. Update to v2.0.0-beta.3 immediately!

OpenSSL's April 2026 advisory reveals 7 flaws, including a moderate RSA memory leak (CVE-2026-31790). Learn if your version is affected and how to patch.

CVE-2026-34838: A critical 10.0 flaw in GroupOffice allows authenticated users to trigger RCE via insecure deserialization. Update to v26.0.12 immediately!
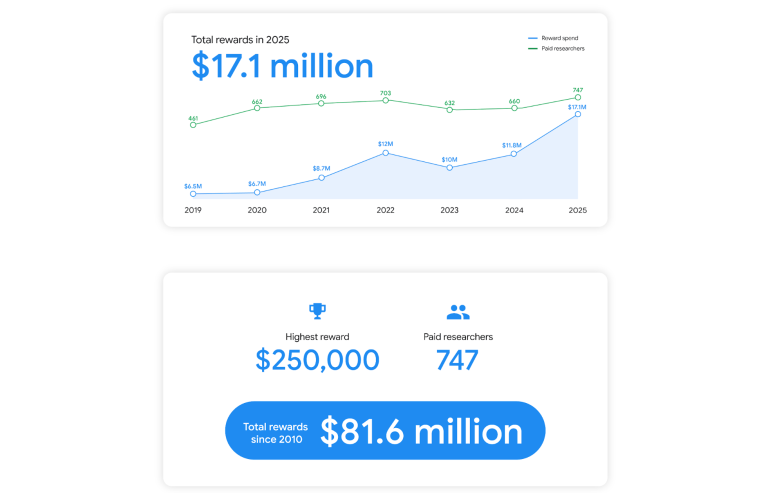
Google’s 2025 VRP hit an all-time high with $17.1M in payouts. Discover how the new AI VRP and elite bugSWAT events are shaping the future of security.

Apple overhauled its Security Bounty program, offering a $2M base reward (up to $5M with bonuses) for zero-click exploits that match mercenary spyware attacks and bypass Lockdown Mode.