 Do Son
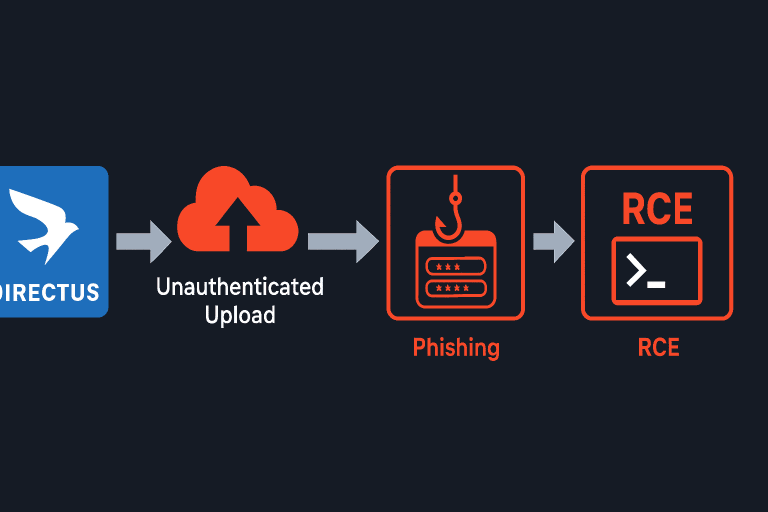
A critical vulnerability in the Directus API (CVE-2025-55746) allows unauthenticated attackers to silently upload and modify files, leading to webshells and RCE.
Vulnerability

A new report reveals a stealthy attack on GeoServer using a critical RCE flaw. Instead of ransomware, attackers are hijacking servers to earn passive income.

A critical flaw in the widely used sha.js library (CVE-2025-9288) can lead to hash collisions and private key extraction, threatening web applications.

A new report from Trend Micro details how the Warlock ransomware group is exploiting a vulnerability in unpatched Microsoft SharePoint servers to attack organizations.

A critical flaw in the AI tool CodeRabbit allowed a researcher to gain RCE and write access to over a million repositories via a malicious pull request.
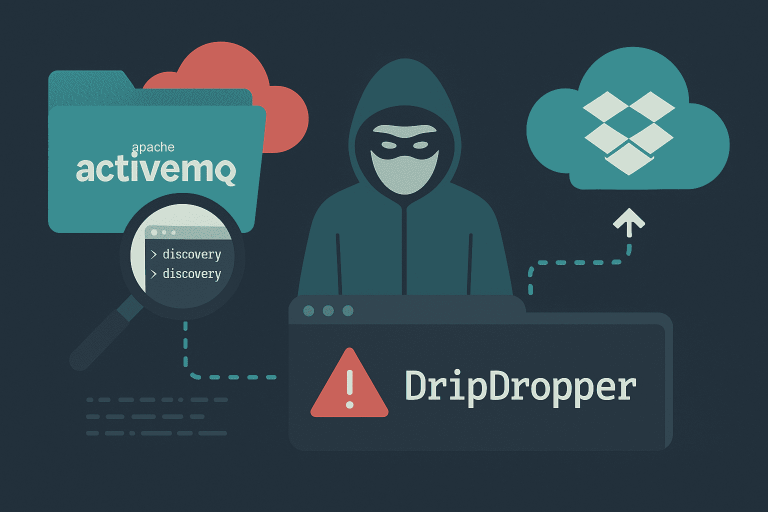
A Red Canary report reveals attackers are exploiting an Apache ActiveMQ flaw to breach Linux systems, then patching the vulnerability to hide their presence.

A critical XXE flaw in Apache Tika's PDF parser could allow attackers to access sensitive data and pivot into internal networks via crafted PDF files.

BI.ZONE Threat Intelligence uncovered a series of targeted cyber-espionage campaigns conducted by the Paper Werewolf (GOFFEE) cluster,...

A critical vulnerability (CVSS 9.3) in Docker Desktop could allow malicious containers to gain full control of the host system. Update now to version 4.44.3.

Apple has released an urgent security update to patch a zero-day vulnerability (CVE-2025-43300) in its Image I/O framework that is being actively exploited in targeted attacks.

A critical vulnerability (CVE-2025-54336) in Plesk Obsidian could allow attackers to bypass the admin password and take complete control of affected servers.

Critical design flaws in Workhorse Software's municipal accounting platform could allow unauthenticated users to download full database backups with sensitive PII and financial records.

Google has released an urgent update for Chrome, patching a high-severity, out-of-bounds write vulnerability in the V8 JavaScript engine. Update your browser now.

A new analysis details how the RansomEXX gang exploited a use-after-free zero-day (CVE-2025-29824) in the Windows Common Log File System to gain SYSTEM privileges.
A critical privilege escalation flaw in Capsule Kubernetes (CVE-2025-55205) allows tenant users to bypass security and launch cross-tenant attacks.
A critical RCE flaw in Trend Micro Apex One has been added to CISA's KEV Catalog due to active exploitation. All agencies must patch by September 8.

A new vulnerability in AMI Aptio UEFI firmware allows for arbitrary code execution in System Management Mode, a privileged environment that can bypass OS controls.

A critical directory traversal vulnerability (CVE-2025-48387) in the popular NPM package tar-fs allows attackers to write arbitrary files and gain RCE.

A new security update for PostgreSQL fixes three vulnerabilities, including two critical flaws that could lead to remote code execution.
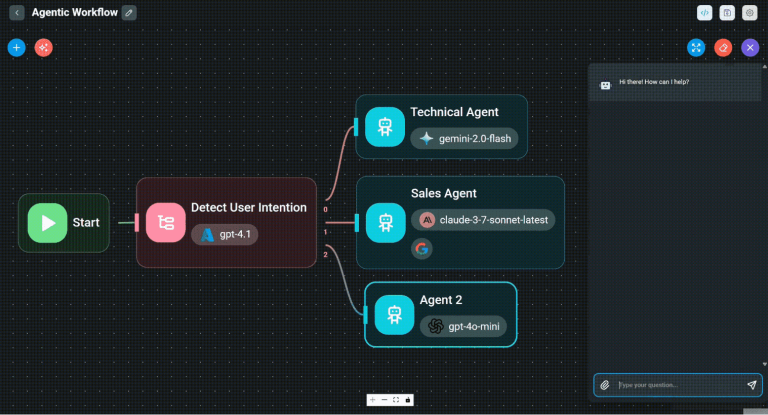
Two critical remote code execution (RCE) vulnerabilities with CVSS scores of 9.8 were found in the open-source Flowise AI platform.

A critical vulnerability (CVE-2025-7972) in Rockwell Automation's FactoryTalk Linx software allows attackers to bypass authentication and alter industrial networks.
ImageMagick has patched four security vulnerabilities, including high-severity memory corruption bugs, that could affect applications using the toolkit.