 Do Son
Discover the impact of the Let's Encrypt certificate lifespan reduction. Learn how the shift to 45-day TLS certificates demands robust ACME automated renewal.
web development
Google officially introduces Chrome JPEG XL support by default in version 155. Explore how this image format enhances quality, compression, and performance.
OpenAI is testing a 'Sign in with ChatGPT' feature across select platforms, enabling seamless single sign-on while preserving user account security.

The Model Context Protocol (MCP) undergoes a massive update to a stateless architecture, eliminating session IDs and introducing multi-round requests.

Protect your app from CVE-2026-23870. Learn how this high-severity React Server Components DoS flaw crashes servers and how to patch your React 19 build today.
Apache Wicket 10.9.0 fixes 3 Critical flaws: Path Traversal (CVE-2026-43975), Session Fixation, and Resource Guard bypass. Secure your Java apps and patch now!
Critical 9.0 CVSS flaw in Thymeleaf (CVE-2026-41901) allows SSTI and arbitrary code execution. Secure your Java web apps—upgrade to v3.1.5.RELEASE now!

Clerk reveals a critical 9.1 CVSS flaw in createRouteMatcher. Crafted requests can bypass middleware gating in Next.js, Nuxt, and Astro. Patch your apps now!
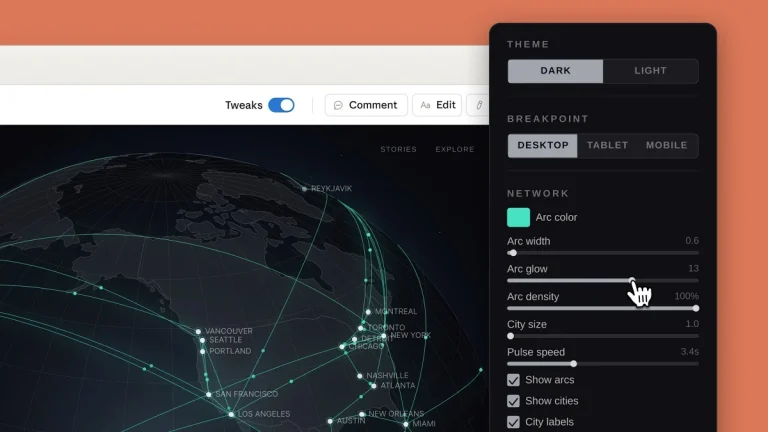
Anthropic launches Claude Design! Powered by the Opus 4.7 vision model, it creates UI prototypes and brand-aligned assets that follow your specific codebase.
Thymeleaf 3.1.4 fixes two critical 9.1 CVSS vulnerabilities. Unauthenticated attackers can bypass security for SSTI. Audit your user input and patch today!
A critical 9.4 CVSS vulnerability in protobuf.js puts 220 million monthly downloads at risk of RCE. Patch your Node.js and browser apps to version 8.0.1+.

Google formally classifies back-button hijacking as a "malicious practice." Fix your navigation scripts by June 15, 2026, or face total search de-indexing.

Axios CVE-2025-62718 allows a critical NO_PROXY bypass via hostname normalization errors. Protect your internal network from SSRF—patch or normalize today!
Laravel Passport patches a 7.1 CVSS authentication bypass where machine tokens masquerade as human users. Protect your app—upgrade to v13.7.1 now!
React patches a 7.5 CVSS DoS vulnerability in Server Components (CVE-2026-23869). Stop CPU exhaustion attacks—update your 19.x dependencies now!

Electron patches 5 flaws (CVSS 7.0-8.4) allowing sandbox escapes and context isolation bypass. Update to v41, 40, or 39 to secure your desktop app now.

Joomla releases critical 8.6 CVSS patches for CVE-2026-23898 & CVE-2026-23899. Prevent arbitrary file deletion and API leaks—update to 5.4.4 or 6.0.4 today!

Lodash (CVE-2026-4800) faces an 8.1 CVSS code injection flaw in the _.template function. Attackers can bypass validation via imports. Update to 4.18.0 now!

2M+ monthly users are at risk as MikroORM patches a critical 9.3 CVSS SQL injection flaw (CVE-2026-34220). Update to 6.6.10 or 7.0.6 immediately to stay safe.
Node.js releases critical updates for 20.x to 25.x, fixing high-severity flaws like the __proto__ header crash and TLS errors. Update to v25.8.2 now.

A critical 9.6 CVSS vulnerability in jsPDF (CVE-2026-31938) allows attackers to inject malicious scripts via XSS. Update to version 4.2.1 immediately.

Google Chrome shifts to a 14-day update cycle starting with M153 in Sept 2026. Discover how this biweekly rhythm impacts security, features, and developers.