
 Do Son
The Dysphoria botnet uses blockchain ENS/SNS domains for covert C2 and turns victims into relays. XLab tracked over 200,000 bots in this IoT DDoS botnet.
XLab
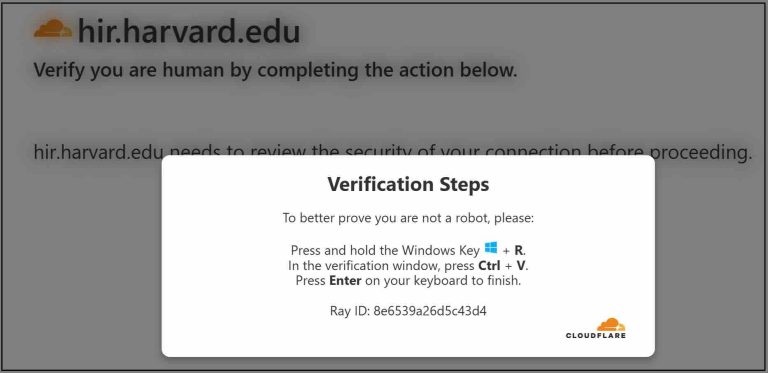
XLab uncovers a massive Ghost CMS poisoning campaign utilizing CVE-2026-26980 to launch FakeCaptcha attacks. Learn how to secure your site.
Urgent: cPanel & WHM hit by global 9.8 CVSS auth bypass. Over 2,000 IPs are actively hijacking servers for data theft and ransomware. Patch immediately!
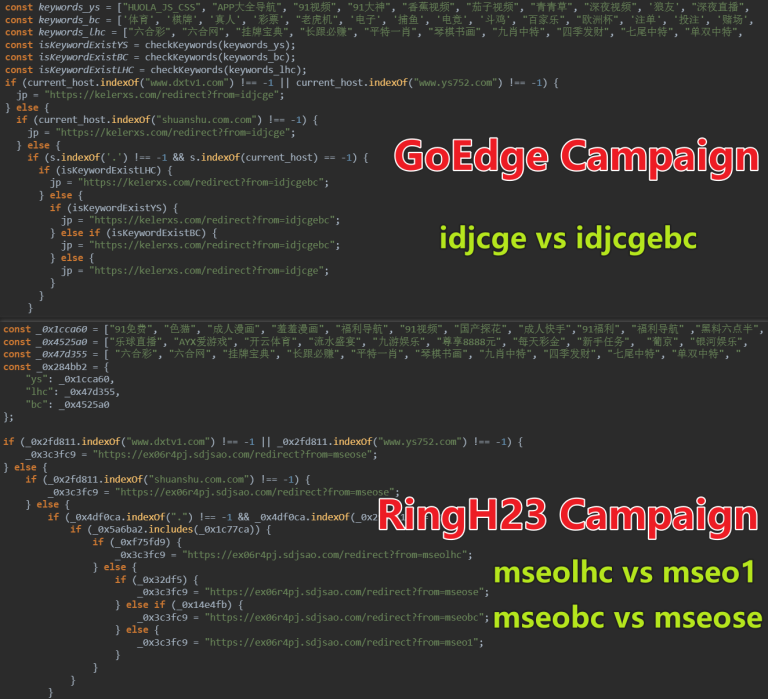
XLab researchers reveal the return of OFAC-sanctioned Funnull. The group is using the new RingH23 framework to hijack CDNs and poison supply chains.

A new report reveals MystRodX, a stealthy backdoor that uses passive wake-up triggers and multi-layer encryption to operate undetected in networks for months.

RapperBot botnet resurfaces with 50,000+ active bots, now demanding Monero extortion to halt DDoS attacks. The self-proclaimed "rapper" malware targets IoT devices globally.

A C++ backdoor named Pickai is actively exploiting ComfyUI servers, compromising nearly 700 AI image generation hosts and posing a supply chain risk