 Do Son
Rapid7 disclosed 17 Zimbra Collaboration Suite flaws, including CVE-2026-10632 and CVE-2026-93640, allowing XSS and root privilege escalation.
Zimbra
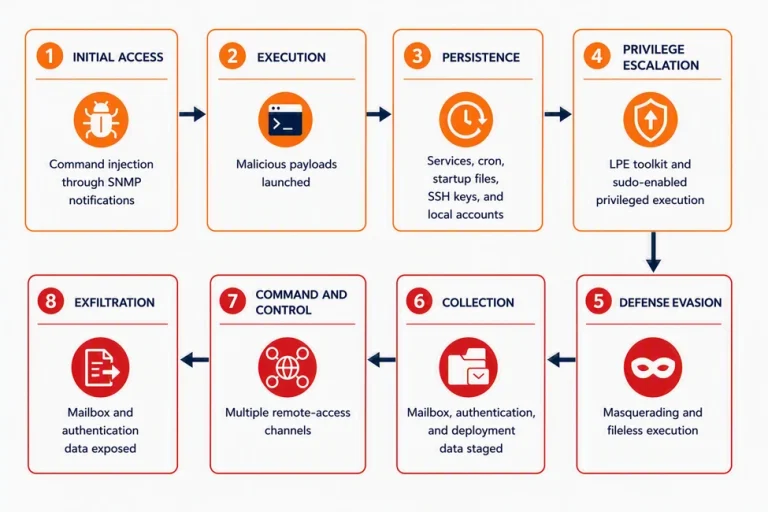
Zimbra CVE-2026-73570 lets one crafted email run code. Microsoft details the Zimbra command injection attacks: web shells, root access, and key theft.
CVE-2026-73570 is exploited in the wild. This unauthenticated RCE hits Zimbra Collaboration via SNMP notifications. Patch to 10.1.20 now.
Proofpoint ties TA488 and TA458 to half-click exploits and webmail zero-days that steal email from Ukrainian, NATO and US government mailservers.
Zimbra 10.1.20 fixes multiple Zimbra vulnerabilities, including an SNMP command injection flaw and several XSS bugs. Admins should upgrade now.

CISA adds 8 vulnerabilities to the KEV Catalog, including Cisco, PaperCut, and Zimbra flaws. Actively exploited threats require immediate patching.

Zimbra 10.1.16 patches critical XSS, XXE, and LDAP injection flaws. Update immediately to secure your email collaboration suite and restore PDF previews.
CISA adds 4 flaws to KEV, including critical Versa Concerto auth bypass (CVSS 9.2) & malicious "Prettier" package. Patch by Feb 12 to stop active attacks.
Zimbra patches a high-severity LFI (CVE-2025-68645) allowing unauthenticated file access and a Flickr Zimlet credential leak. Upgrade to v10.1.13!

Zimbra fixes Critical Stored XSS and an Unauthenticated LFI flaw, urging users to update immediately to mitigate session hijacking and data exfiltration risks.

Zimbra issued an emergency patch (v10.1.12) for a Critical SSRF vulnerability in the chat proxy that lets attackers manipulate internal server requests. Update is urged immediately.
CISA added the Zimbra XSS zero-day (CVE-2025-27915) to its KEV Catalog due to active exploitation since January. Attackers use malicious .ICS files to steal mail data.

Explore the Lotus Blossom group's persistent cyber attacks and learn how they utilize the Sagerunex backdoor for espionage.
CISA Flags Actively Exploited Zimbra (CVE-2023-34192) and Microsoft (CVE-2024-49035) Vulnerabilities
CISA Flags Actively Exploited Zimbra (CVE-2023-34192) and Microsoft (CVE-2024-49035) Vulnerabilities
The newly flagged flaws, CVE-2023-34192 and CVE-2024-49035, target widely used platforms, posing significant threats to both public and private sector entities

Find out about the remote code execution flaw in Zimbra email servers and its potential impact. Take steps to protect your servers from CVE-2024-45519.
The new vulnerability, as revealed by ESET specialists, is identified as CVE-2023-5631 and has a CVSS score of 5.4.