 Do Son
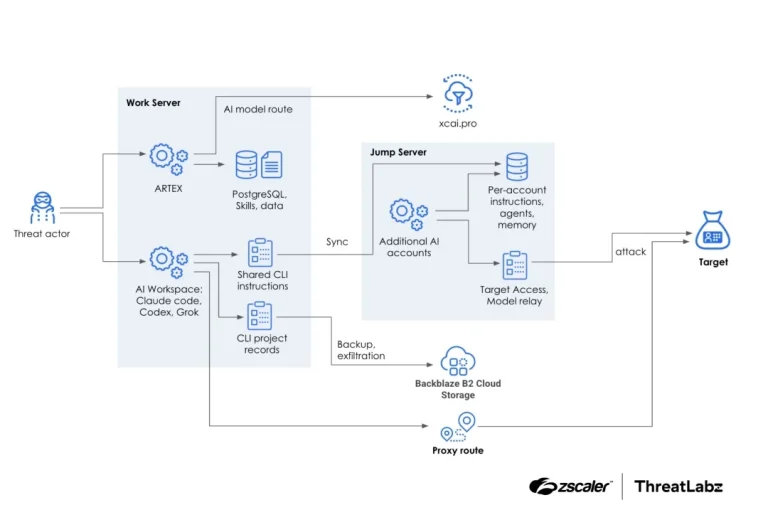
Zscaler ThreatLabz exposes a global ARTEX AI hacking campaign. See how an operator used ARTEX AI hacking tools, DeepSeek, GLM, and Grok to steal data.
Zscaler ThreatLabz
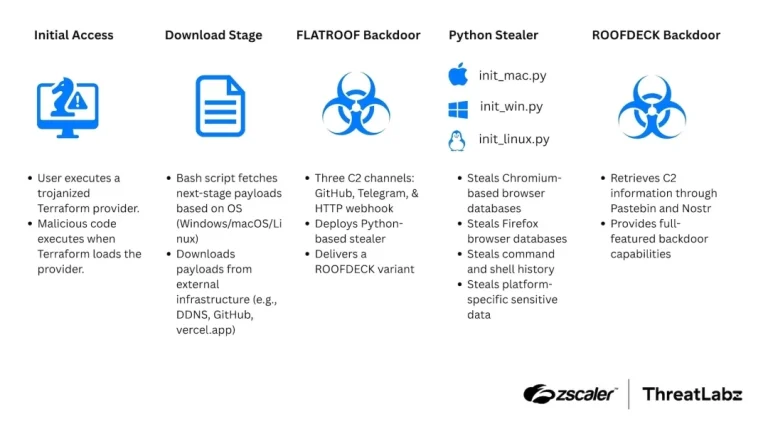
Suspected TraderTraitor hackers used a trojanized Terraform provider to drop FLATROOF and ROOFDECK malware on macOS, Linux, and Windows.
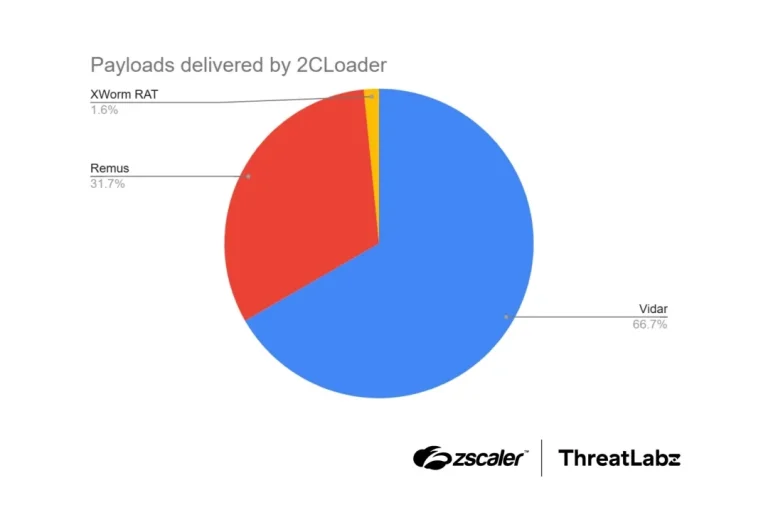
2CLoader malware dodges sandboxes and security tools to deliver Vidar and Remus infostealers. See how it works and how to detect it.

A new GoGRPC backdoor spreads through Microsoft Teams vishing and Quick Assist. Zscaler links the campaign to a likely ransomware access broker.

TELESHIM malware hits Middle East governments and abuses Telegram C2 to hide traffic. Zscaler ThreatLabz found the new backdoor and its tooling.

Edgecution malware abuses a malicious Edge extension and native messaging to backdoor hosts. Zscaler links it to a Payouts King access broker.
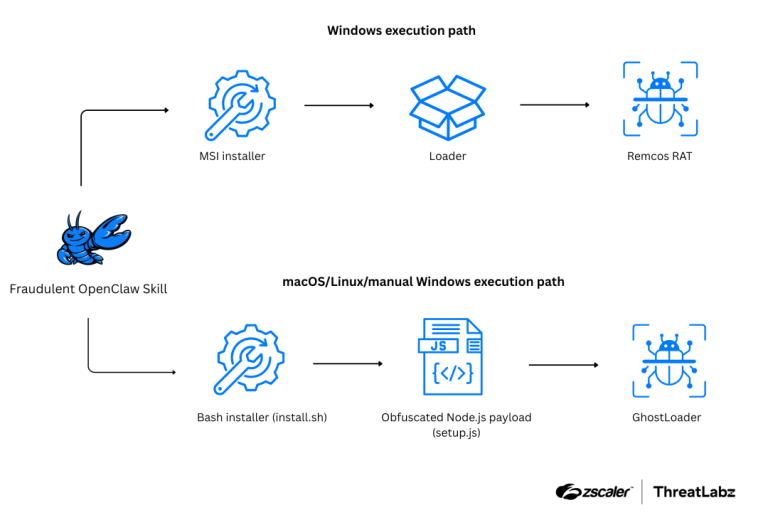
Zscaler ThreatLabz exposes DeepSeek-Claw, a malicious AI skill targeting the OpenClaw framework to deploy GhostLoader and Remcos RAT. Secure your agents now!
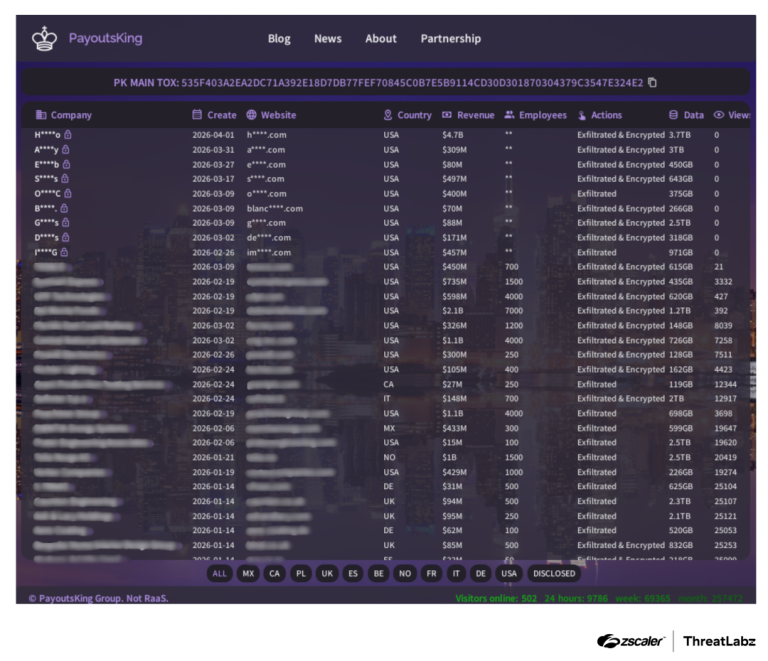
Payouts King, the successor to BlackBasta, uses vishing and direct syscalls to bypass EDR and strike global targets. Learn how to defend your enterprise.

Zscaler reveals a 2026 attack chain using fake Adobe Reader lures to install ScreenConnect via in-memory execution and UAC bypass. Protect your network now!
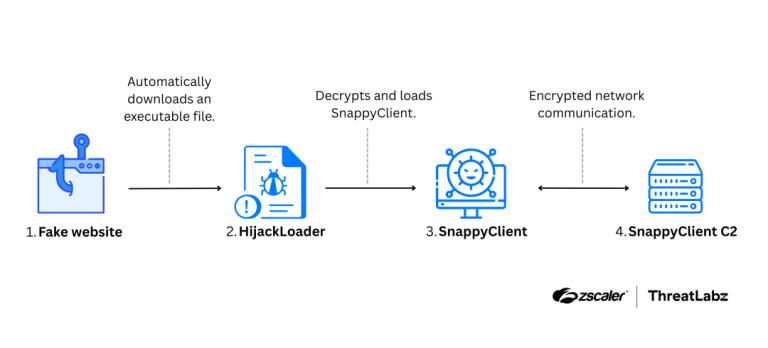
Zscaler ThreatLabz unmasks SnappyClient, a C++ C2 framework linked to HijackLoader. It uses AMSI bypass and Heaven’s Gate to steal crypto and gain remote access.

Zscaler ThreatLabz reveals a surge in Middle East conflict-themed cyberattacks, uncovering 8,000+ malicious domains, LOTUSLITE backdoors, and scams.

Zscaler ThreatLabz uncovers Dust Specter, an Iran-linked cyber campaign hijacking Iraqi government infrastructure to deploy custom AI-assisted malware.

Zscaler analyzes GuLoader's evolution. The malware uses Google Drive, polymorphic code, and exception-based obfuscation to evade detection.

Zscaler reveals Marco Stealer, a new malware harvesting crypto & cloud files. It uses AES-256 encryption & kills analysis tools. Learn how to detect it.

APT28 launches "Operation Neusploit" targeting Europe. Hackers exploit CVE-2026-21509 to deploy MiniDoor malware via RTF files. Patch Office now.

Pakistan-linked spies target India with "Sheet Attack," using Google Sheets for C2 and GenAI to build malware. Learn about SHEETCREEP and FIREPOWER.
New "Gopher Strike" & "Sheet Attack" campaigns hit Indian govt. Linked to Pakistan, attackers use GitHub C2 & GenAI malware to evade detection.

Zscaler detects NodeCordRAT, a new malware in malicious npm packages. It uses Discord as a C2 server to loot crypto wallets and Chrome data.

A notorious cyber-espionage group known for terrorizing South American institutions has launched a new campaign against the...
A new supply chain attack on PyPI is delivering SilentSync, a Python RAT. The malware steals credentials and files from developers' systems.

Zscaler has uncovered kkRAT, a new malware targeting Chinese-speaking users. The RAT steals crypto, hijacks clipboards, and uses RMM tools for covert, long-term control.

Zscaler reveals an AI-powered phishing campaign targeting Brazilian users. DeepSite AI and BlackBox AI generated fake government websites to steal Pix payments and personal data.