 Do Son
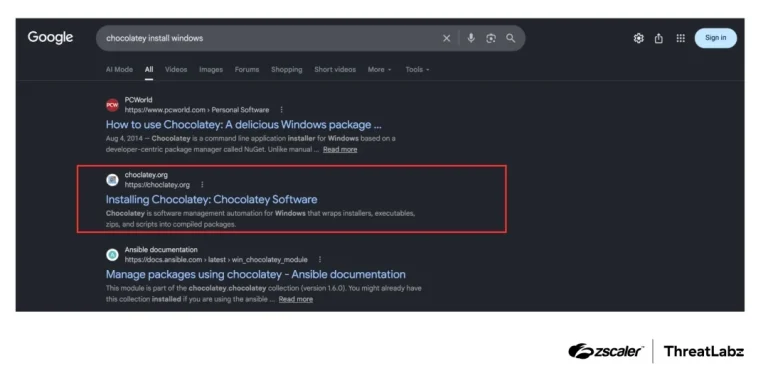
Zscaler uncovers an SEO poisoning campaign using fake Chocolatey and Massgrave sites to drop Armorsteal malware and Python Armorsteal malware modules.
Zscaler

Zscaler details the C2Looper backdoor, a Rust backdoor tied to ransomware that uses GitHub for C2 and likely spreads through ClickFix lures.

Zscaler ThreatLabz analysts discovered the Abyssos modular RAT. This Abyssos RAT gives attackers total remote control, stealing data and credentials.

Tropic Trooper's 2026 campaign uses trojanized SumatraPDF and VS Code tunnels for stealthy East Asian espionage. Learn how to defend your infrastructure.

Zscaler exposed Matanbuchus v3.0, a MaaS downloader pivoting to ransomware. The stealthy C++ malware uses Protobufs for C2, QuickAssist for access, and time-wasting loops to bypass sandboxes.

Zscaler reveals Water Gamayun exploiting the MSC EvilTwin zero-day (CVE-2025-26633) via fake hiring lures to deploy stealthy backdoors.

Russia-linked APT COLDRIVER is using a new multi-stage malware campaign (BAITSWITCH/SIMPLEFIX) with a ClickFix lure to target journalists and activists for espionage.

A new report reveals North Korea's APT37 is using Rust-based malware called Rustonotto, marking a shift toward modern languages and multi-platform attacks.
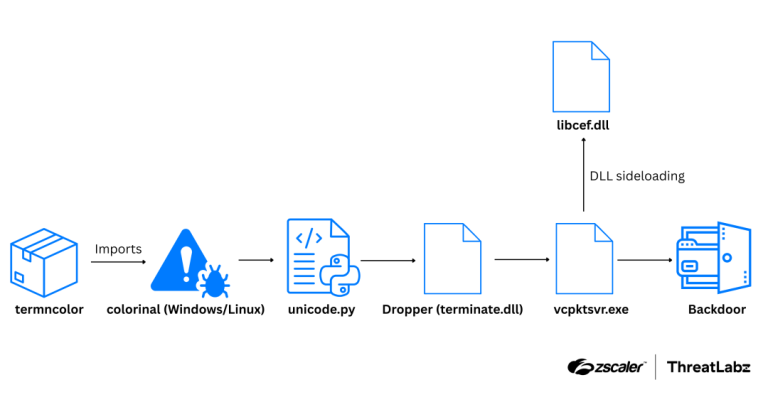
A new report reveals a malicious Python package on PyPI that uses a stealthy dependency and DLL sideloading to deliver a multi-stage malware.

Zscaler uncovers two China-linked APT campaigns, "GhostChat" and "PhantomPrayers," targeting the Tibetan community with sophisticated spyware via fake apps and DLL sideloading.
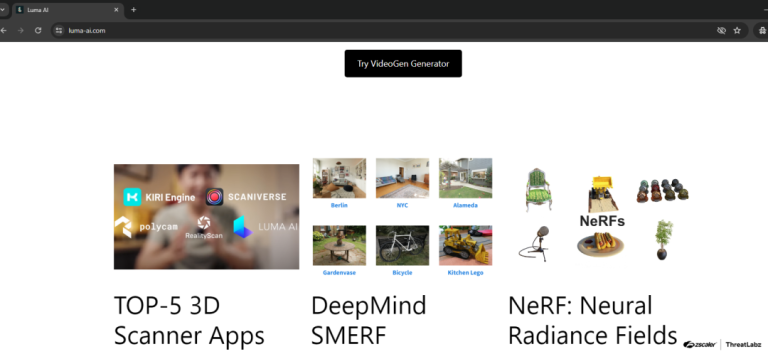
A sophisticated campaign is exploiting AI tool popularity via Black Hat SEO to poison search results, delivering Vidar, Lumma, and Legion Stealers to unsuspecting users.