Skip to content
September 14, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
  • Home
  • News
  • Technology
  • Adoption of Network Security Standards, TLS v1.3 to Bring a Safer Network Environment
  • Technology

Adoption of Network Security Standards, TLS v1.3 to Bring a Safer Network Environment

Do Son March 25, 2018 2 minutes read
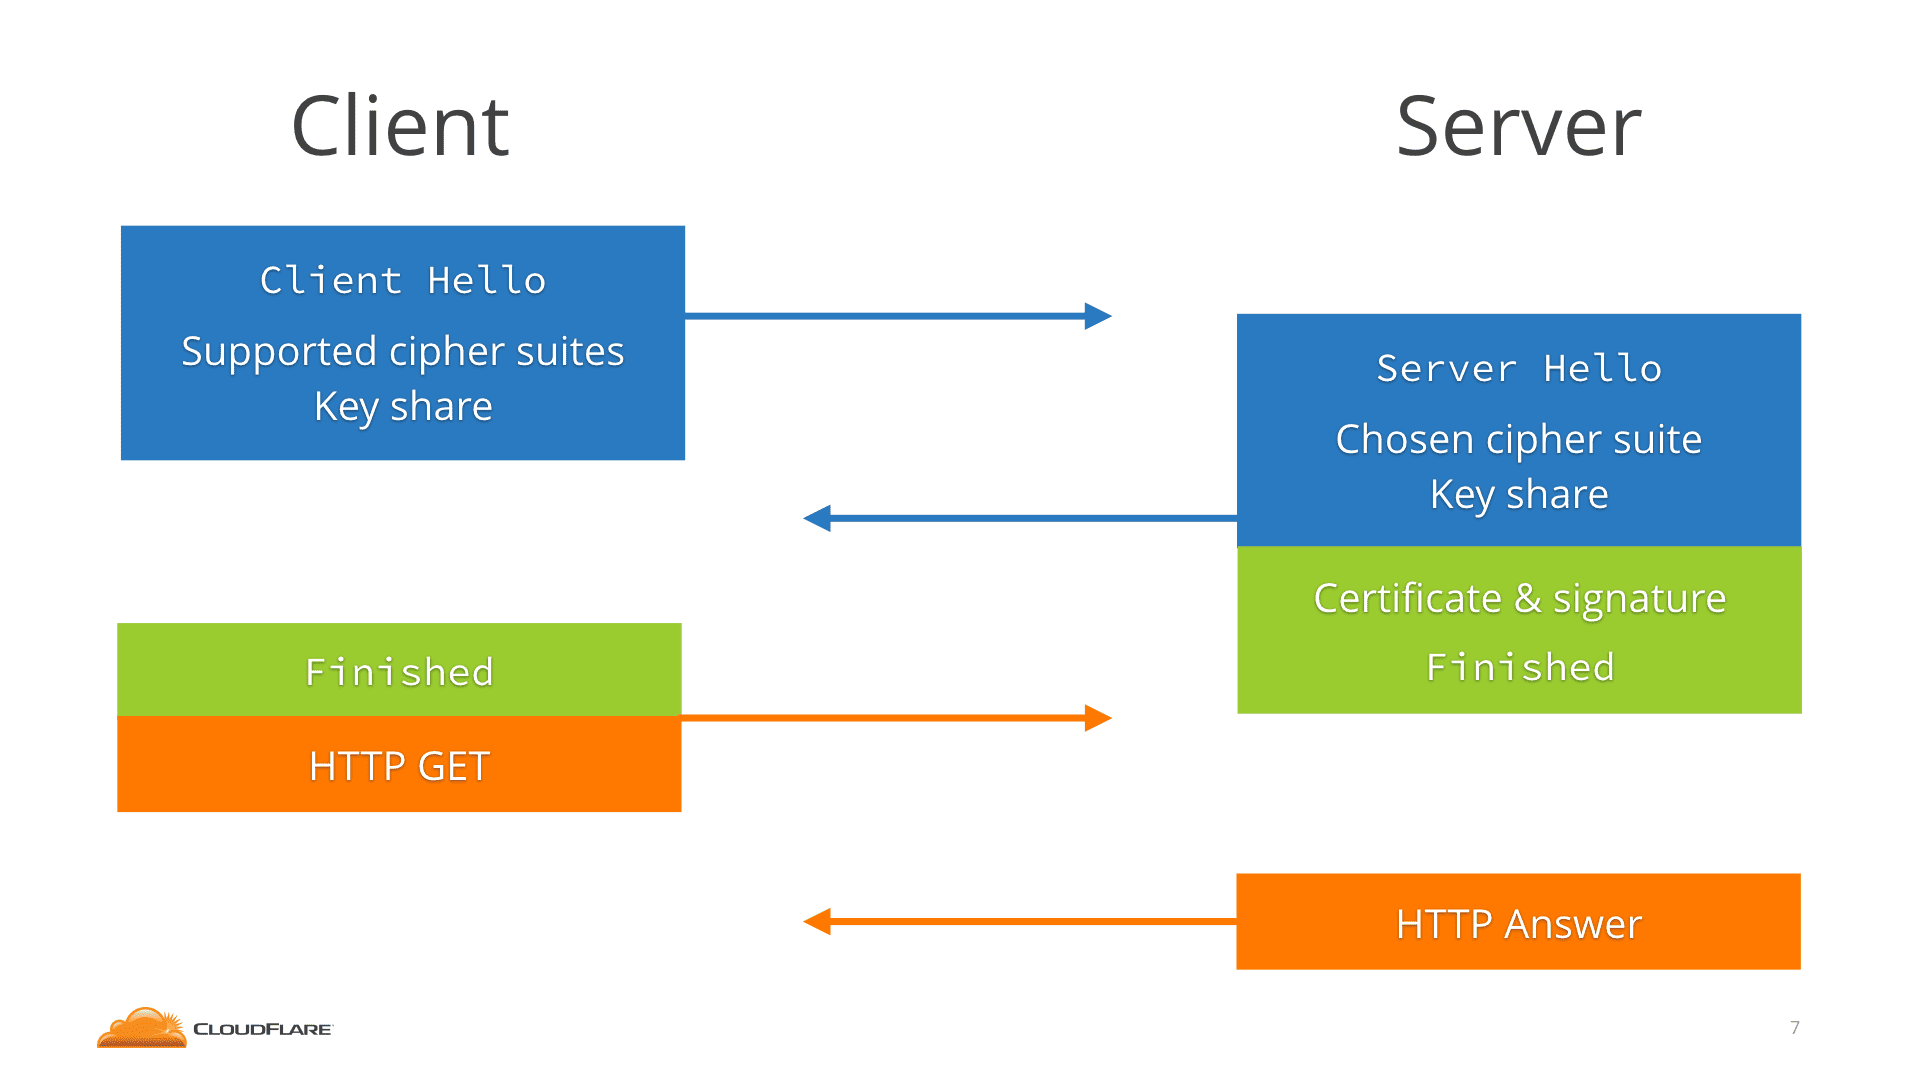
TLS v1.3
Add Daily CyberSecurity as a preferred source on Google

Internet engineers recently passed a security framework that will make encrypted connections on the network faster and more resistant to snoops.

It’s called Transport Layer Security version 1.3 (TLS v1.3), which is not a major update, but rather an iterative improvement that allows the Web to work when there are any malicious actions or programs. The IETF is a team of engineers from all over the world who collaborated on this standard – it took more than four years and drafted 28 drafts before passing TLS 1.3.

Image: Cloudflare

TLS 1.3 mainly supports four handshake modes

  • The “handshake” between client and server has been streamlined and encryption initiated earlier to minimize the amount of data transmitted in the clear.
  • “Forward secrecy,” meaning hackers can’t skim decryption keys from one exchange and use it to decrypt others later.
  • “Legacy” encryption algorithms have been removed as options, as these could occasionally be forced into use and their shortcomings leveraged to break the cipher on messages.
  • A new “0-RTT,” or zero round-trip time, mode in which the server and client that have established some preliminaries before can get right to sending data without introducing themselves to each other again.


The entire standard is 155 pages long. If you want to read or learn more about one of the new features, you can read it here.

Source: TechCrunch

Related coverage

  • Microsoft Launches Gaming Copilot on Windows & Xbox App
  • Beyond the Glow: How iOS 27’s “Snow Leopard” Focus and Siri App Will Redefine the iPhone in 2026
  • Apple Open-Sources Homomorphic Encryption for Enhanced Data Security
Track all actively exploited CVEs →

Support Our Threat Intelligence

Find our tech and OS security coverage helpful? Support our work today and unlock a 100% ad-free reading experience!

Buy Me a Coffee Logo Buy Me a Coffee
Select your plan
Free Pro Team

Hover over a plan to see its benefits.

Stay Ahead of the Threat

Join security professionals receiving zero-hour CVE alerts, PoC updates, and threat analysis directly to their inbox.

No spam. One actionable email per week. Unsubscribe anytime.

SHARE
Share on FacebookShare on XShare on LinkedInShare on TelegramShare on BlueskyShare on Mastodon
Written by
@DdoS · Security Researcher

Do Son

Do Son is the Founder and Editor of SecurityOnline.info. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.

Tags: TLS v1.3

Search

Translation

CVE ALERTS
📧

Email Delivery
Get threat intel straight to your inbox.

♾️

Unlimited Vendors
Track every technology in your stack.

🚨

All New CVE Alerts
Be the first to know about new flaws.

⚙️

Custom EPSS Threshold
Filter noise, focus on real risks.

💬

Slack & Teams Webhook
Integrate directly into your SecOps.

🚫

100% Ad-Free
Enjoy an uninterrupted reading experience.

$7/mo
Subscribe Now

🚨 Active Exploits in the Wild

  • CVE-2026-51990
    A critical remote code execution vulnerability in Sogou Input Method, one of the most widely used Chinese-language input...
    Admin intel📅 Updated: Sep 12, 2026
  • CVE-2026-85706CVSS 10.0
    GitLab has remediated an issue that, under certain conditions, an unauthenticated user could have read arbitrary files from...
    Admin intelCISA KEV📅 Added to KEV: Sep 11, 2026📅 Updated: Sep 11, 2026
  • CVE-2026-42016CVSS 8.1
    JFrog Artifactory (Self Hosted) versions before 7.133.11 are vulnerable to a privilege escalation attack due to a validation...
    Admin intelCISA KEV📅 Added to KEV: Sep 11, 2026📅 Updated: Sep 11, 2026
  • CVE-2026-42018CVSS 7.5
    JFrog Artifactory could return an internal anonymous-user token to an unauthenticated caller when anonymous access is disabled, potentially...
    Admin intelCISA KEV📅 Added to KEV: Sep 11, 2026📅 Updated: Sep 11, 2026
  • CVE-2026-84869CVSS 9.9
    A condition in the ScreenConnect client may allow files to be transferred and executed through an active remote...
    CISA KEV📅 Added to KEV: Sep 11, 2026
  • CVE-2026-20079CVSS 10.0
    A vulnerability in the web interface of Cisco Secure Firewall Management Center (FMC) Software could allow an unauthenticated,...
    Admin intelCISA KEV📅 Added to KEV: Sep 9, 2026📅 Updated: Sep 9, 2026
  • CVE-2025-25249CVSS 8.1
    A heap-based buffer overflow vulnerability in Fortinet FortiOS 7.6.0 through 7.6.3, FortiOS 7.4.0 through 7.4.8, FortiOS 7.2.0 through...
    Admin intelCISA KEV📅 Added to KEV: Sep 9, 2026📅 Updated: Sep 9, 2026
  • CVE-2026-87491
    Out of bounds write in V8 in Google Chrome prior to 153.0.8010.36 allowed a remote attacker to execute...
    Admin intelCISA KEV📅 Added to KEV: Sep 9, 2026📅 Updated: Sep 9, 2026
Powered by CVE Watchtower

🔴 Live Critical Threats

  • CVE-2026-59178CVSS 9.8
    ESPHome Device Builder Dashboard is a dashboard for the ESPHome home management...
  • CVE-2026-90945CVSS 9.8
    Crawlab through 0.6.3 uses a hard-coded HMAC-SHA256 secret for JWT token signing...
  • CVE-2026-90942CVSS 9.6
    Casdoor through 4.4.0 fails to properly mask the instance-wide built-in certificate private...
  • CVE-2026-76461CVSS 9.8
    A vulnerability in the email parsing of Cisco AsyncOS Software for Cisco...
  • CVE-2026-76443CVSS 9.8
    As part of Cisco's ongoing commitment to proactive security and product quality,...
  • CVE-2026-76441CVSS 9.8
    As part of Cisco's ongoing commitment to proactive security and product quality,...
  • CVE-2026-76440CVSS 9.8
    As part of Cisco's ongoing commitment to proactive security and product quality,...
  • CVE-2026-20353CVSS 9.8
    As part of Cisco's ongoing commitment to proactive security and product quality,...
  • CVE-2026-57131CVSS 9.8
    PraisonAI is a multi-agent teams system. Prior to 4.6.58, praisonai.jobs.server.create_app mounts praisonai.jobs.router.create_router...
  • CVE-2026-57124CVSS 9.8
    PraisonAI is a multi-agent teams system. Prior to 4.6.59, the default UI...
Powered by CVE WATCHTOWER

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q2 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.