
 Do Son
Discover the latest critical Apache CXF vulnerabilities, including RCE and XXE flaws, and learn how to secure your open source services framework.
Do Son
Do Son is the Founder and Editor of Daily CyberSecurity. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.

Learn about the critical Memcached SASL vulnerability flaws fixed in version 1.6.42. Discover how timing side channels impacted authentication.
Learn about the Apache ECharts XSS vulnerability (CVE-2026-45249) in the Lines series tooltip rendering logic and find out how to secure your code.

CVE-2026-48095 (CVSS 8.8) is a heap buffer overflow in 7-Zip that a crafted archive can trigger. Update to the patched version now.

Read our weekly threat intelligence briefing. Discover active exploits, critical CVEs, and the latest CISA KEV additions for May 18–24, 2026.

Learn how Mandiant uncovered the critical Knowledge Deliver RCE vulnerability (CVE-2026-5426) and how to protect your systems today.

Security researchers have exposed a malicious Go module backdoor hidden inside the shopsprint/decimal package that executes code using stealthy DNS TXT records.

HUMAN's Satori team disrupted Trapdoor, an Android ad fraud ring using 455 apps and hidden WebViews to fake 659 million daily ad bids.
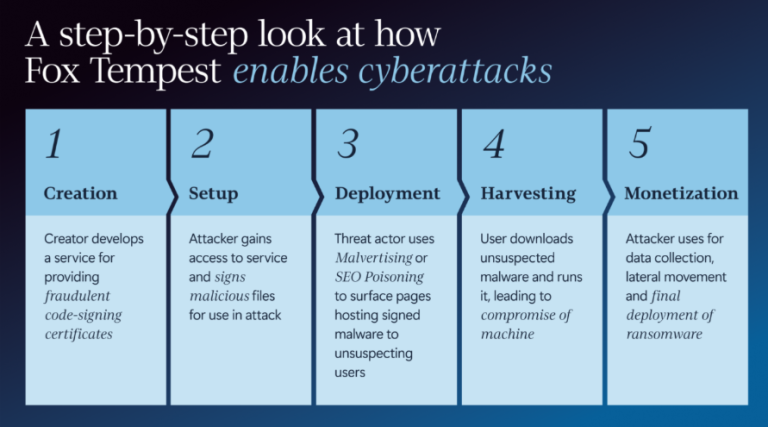
Microsoft's DCU and Resecurity have disrupted Fox Tempest, a major MSaaS ring that forged code-signing certificates for ransomware delivery.

TrendAI exposes Banana RAT, a fileless banking trojan by SHADOW-WATER-063 that uses in-memory execution and fake UI overlays to hijack Pix-QR transfers.

NLnet Labs patches a critical Unbound DNSSEC validation vulnerability allowing unauthenticated remote code execution. Update to 1.25.1.

A critical unauthenticated RCE flaw (CVE-2026-45695) impacts Kopia backup servers. Learn how the Kopia SSH ProxyCommand injection exploit operates and how to patch it.

Urgent: TYPO3 patches a critical 9.2 CVSS flaw (CVE-2026-46725) in Content Element Selector plugin. Unauthenticated attackers can achieve full server RCE.

The FreeBSD Project fixes seven vulnerabilities, including a zero-interaction Wi-Fi shell expansion RCE (CVE-2026-45255) and severe kernel leaks.

An NGINX heap buffer overflow vulnerability known as poolslip allows remote code execution. Learn how to secure your network servers now.
Code security is becoming one of the most difficult operational problems in modern software development, not because...

ConnectWise released a fix for a ConnectWise Automate vulnerability (CVE-2026-9089). Learn about the code download flaw and how to patch it now.

A recent report shows persistent P2Pinfect botnet activity inside Google Kubernetes Engine via exposed Redis instances. Learn how to secure your network.

A critical Angular hostname hijacking vulnerability allows SSRF attacks. Discover the impact on platform-server and how to patch your apps.
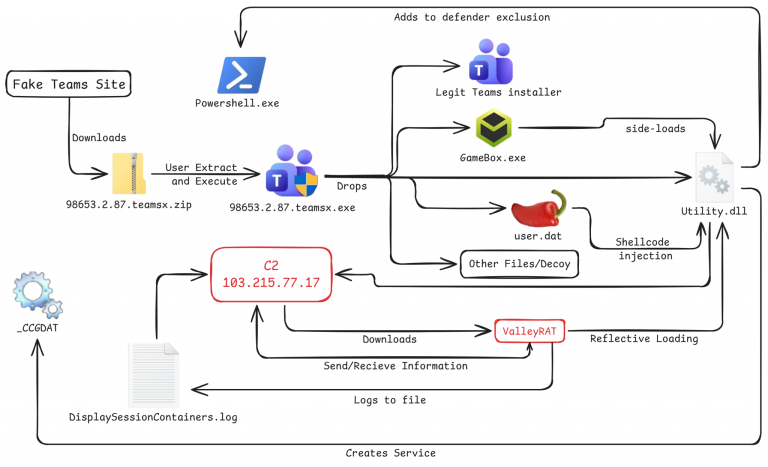
A sophisticated ValleyRAT malware campaign uses fake Microsoft Teams installers and DLL sideloading to evade Windows Defender detection.

Europol completely dismantles 'First VPN,' seizing 33 servers and uncovering an underground database used by thousands of global ransomware operators.

Anthropic’s secret "Mythos" model found 10,000+ bugs in one month for partners like Cloudflare and Mozilla. Discover why this tech remains top-secret.