 Do Son
Learn about the critical Atril single-click RCE vulnerability (CVE-2026-46529). Public details and exploit code are now fully disclosed.
Do Son
Do Son is the Founder and Editor of Daily CyberSecurity. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.

Learn about the latest Screening Serpens cyberattacks exposed by Unit 42. Discover their new RAT variants and advanced defensive evasion tactics.

The FBI issued an alert on the new Kali365 phishing platform. Learn how this PhaaS kit steals Microsoft 365 tokens and bypasses MFA.

Learn about the new Moxa Linux kernel vulnerabilities (CVE-2026-43284). Discover how to apply interim mitigations to prevent privilege escalation.
Cyble researchers uncover a widespread FreePBX exploitation campaign by INJ3CTOR3 deploying the novel JOMANGY webshell for toll fraud.

NVIDIA released updates fixing severe NVIDIA TensorRT-LLM vulnerabilities and Isaac Launchable flaws. Patch your active systems today.
XLab uncovers a massive Ghost CMS poisoning campaign utilizing CVE-2026-26980 to launch FakeCaptcha attacks. Learn how to secure your site.

EclecticIQ warns of a malicious AI installer campaign using SEO poisoning to deliver fileless infostealers to developer environments.

Google CEO Sundar Pichai reveals how Gemini-powered Agentic AI search will shift the web from traditional link clicks to autonomous background task execution.

A major Gemini resource quotas error is rapidly draining developers' weekly usage limits in minutes. Learn about the token tracking bug and Google's resets.
Discover how CVE-2026-48207, a critical PyFory deserialization policy bypass flaw, lets attackers execute remote code, and learn how to patch it now.

Concrete CMS dropped critical Concrete CMS security fixes in version 9.5.1 to eliminate remote code execution vulnerabilities. Update now.

A critical Fission router vulnerability (CVE-2026-46614) allows unauthenticated function invocation in Kubernetes. Learn how to patch it now.

GitHub patches critical GitHub Enterprise Server vulnerabilities (CVE-2026-9312). Learn about key rotation and critical SSRF fixes.
Twig project maintainers patched critical Twig RCE flaws allowing arbitrary code execution via sandbox bypasses. Update to 3.26.0.

A dangerous Windows Kernel EoP vulnerability allows browser sandbox escapes. Public PoC exploit code is available on GitHub.
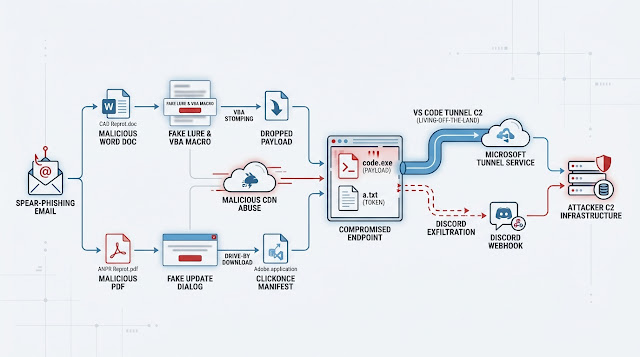
Learn how a sophisticated phishing campaign leverages VS Code Remote Tunnels abuse to bypass security and control enterprise networks.

Internet Systems Consortium released patches fixing six critical BIND 9 flaws that cause memory exhaustion and unexpected daemon crashes.

A sophisticated Android carrier billing fraud campaign hit users worldwide. Learn how fake apps trigger premium SMS abuse and how to stay safe.

Researchers uncover the Tampered Chef malware cluster disguised as PDF editors and tools. Learn how these stealthy threats bypass corporate defenses.
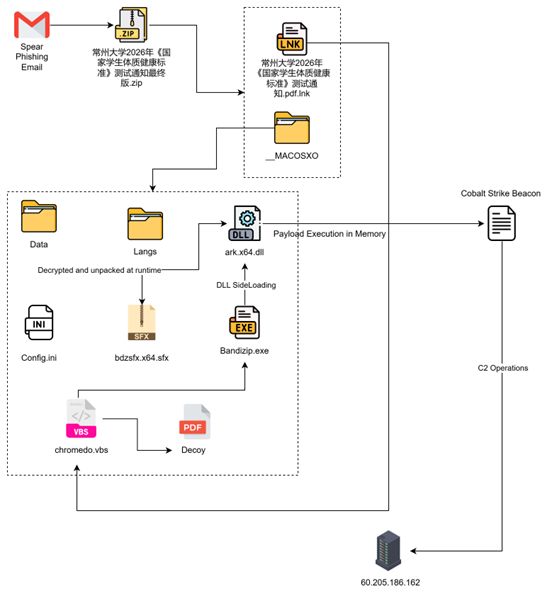
Discover how the Operation Dragon Whistle phishing campaign leverages student fitness lures to deploy stealthy memory-only malware.

Fix the critical Dell Container Storage Modules vulnerability (CVE-2026-40710). Learn how hardcoded credentials expose systems and update now.